
Charter breach exposed personal data from 4.9 million accounts, Have I Been Pwned says
Summary
Have I Been Pwned says leaked data affected 4.9 million Charter accounts. ShinyHunters claimed a vishing attack led to theft from Salesforce; Charter confirmed a breach but said no sensitive personal information or CPNI was exfiltrated.
Key points
- Charter confirmed a breach but said the threat actor did not exfiltrate sensitive personal information or customer proprietary network information (CPNI).
- ShinyHunters claimed the breach began with a vishing call that compromised an employee’s Microsoft Entra account on April 1.
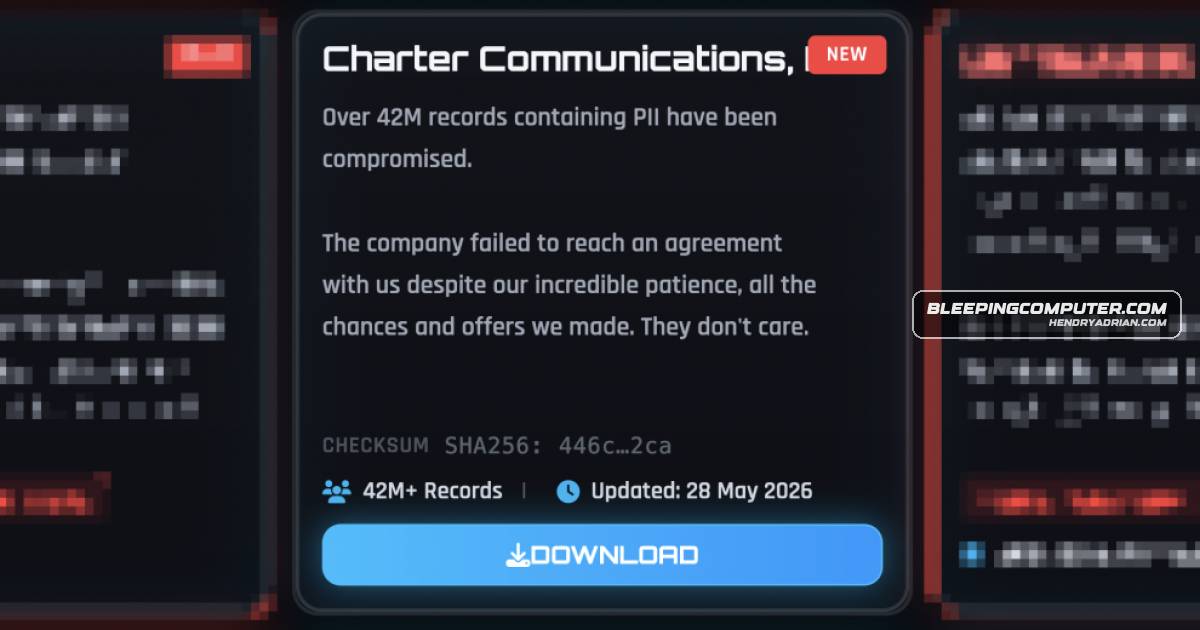
- The group claimed it stole 42 million records from Charter’s Salesforce instance and later leaked the data after Charter reportedly refused to pay a ransom.
- Have I Been Pwned analyzed the leaked data and said 4.9 million accounts were affected, including names, email addresses, phone numbers, and physical addresses.
- About 85,000 records from an internal employee directory reportedly also included job titles.
- The FBI has advised ShinyHunters victims not to pay ransom demands.
Article Details
- Victim Organization
- Charter Communications
- Incident Type
- Data breach involving a reported vishing attack against an employee’s Microsoft Entra account, followed by data theft and extortion.
- Data Types Exposed
- Names
- Email addresses
- Phone numbers
- Physical addresses
- Job titles (in a subset of approximately 85,000 records)
- Plan information (claimed by ShinyHunters)
- Support ticket data (claimed by ShinyHunters)
- CPNI (claimed by ShinyHunters; Charter said no CPNI was exfiltrated)
- Affected Records
- Have I Been Pwned confirmed 4.9 million affected accounts. ShinyHunters claimed it stole 42 million records from Charter’s Salesforce instance.
- Operational Impact
- The breach and exposure of data were reported; no operational disruption was reported. Charter said no sensitive personal information or CPNI was exfiltrated. Have I Been Pwned confirmed that the leaked data included names, email addresses, phone numbers, and physical addresses, with job titles in a subset.
- Ransom Or Extortion
- ShinyHunters reportedly demanded a ransom. After Charter reportedly refused to pay, the group claimed it leaked documents stolen from Charter’s Salesforce instance.
- Claim Status
- confirmed
MITRE ATT&CK
Threat Actors
Salt TyphoonThe article says Charter’s systems were also compromised in a separate wave of breaches by Salt Typhoon; it does not attribute the ShinyHunters incident to this group.ShinyHuntersClaimed responsibility for the Charter breach, said it used vishing to compromise an employee’s Microsoft Entra account and steal records, and reportedly leaked data after Charter refused to pay its ransom demand. Charter has not attributed the attack.
Products
Microsoft EntraShinyHunters claimed responsibility for a breach at Charter Communications that led to the exposure of personal data from 4.9 million accounts after a vishing attack on an employee’s Microsoft Entra account.SalesforceThe group also leaked data taken from Charter’s Salesforce instance after the company reportedly refused to pay the ransom demand, while Charter said no sensitive personal information or CPNI was exfiltrated.