
Krybit Claims Activ’Interim 88 in Germany as a Ransomware Target
Summary
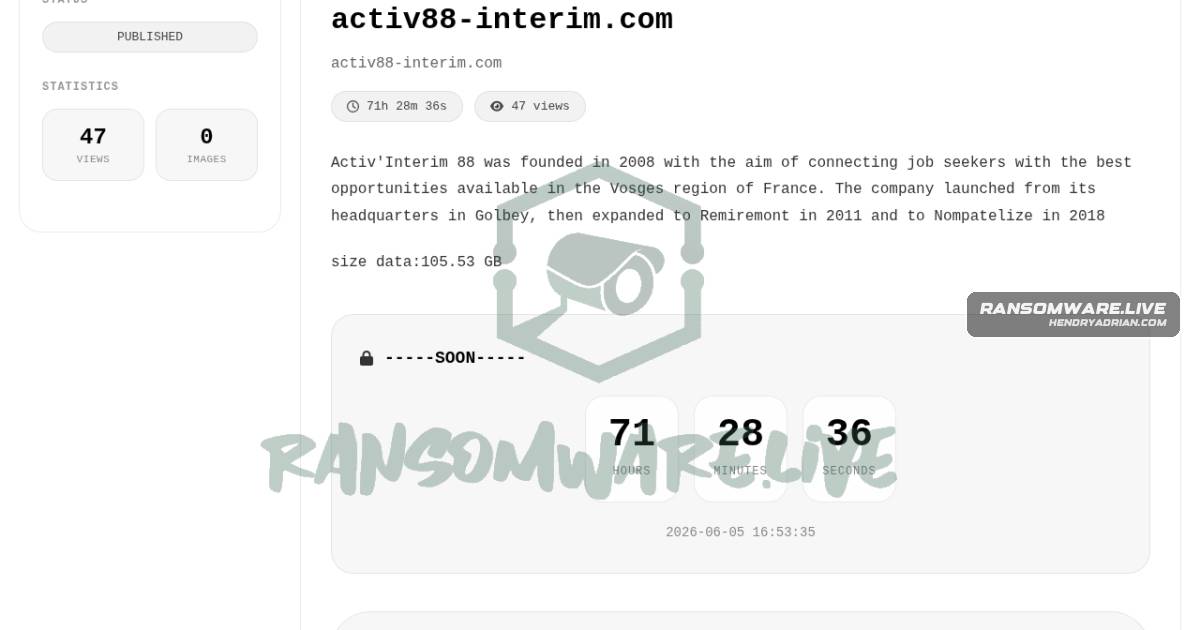
Krybit reportedly claimed Activ’Interim 88 (activ88-interim[.]com) in Germany as a target. The claim was monitored by ransomware.live and is unconfirmed; the article says it cannot verify the group’s claims.
Key points
- The record identifies Activ’Interim 88 in Germany as the claimed victim and lists its sector as business services.
- The alleged ransomware actor is Krybit; the claim is attributed to a post on the group’s site.
- The claim was recorded on June 2, 2026, and monitored by ransomware.live.
- The article says it cannot confirm the claim’s accuracy; no independent confirmation is provided.
Article Details
- Victim
- Activ’Interim 88
- Victim Domain
- activ88-interim.com
- Claim Date
- 2026-06-02
- Encryption Status
- Unknown; the source does not confirm encryption.
- Exfiltration Status
- Unknown; the source does not confirm exfiltration.
- Leak Status
- Krybit reportedly made a claim, but the source does not confirm that victim data was leaked or published.