
Play ransomware group claims incident involving Pearson Ford
Summary
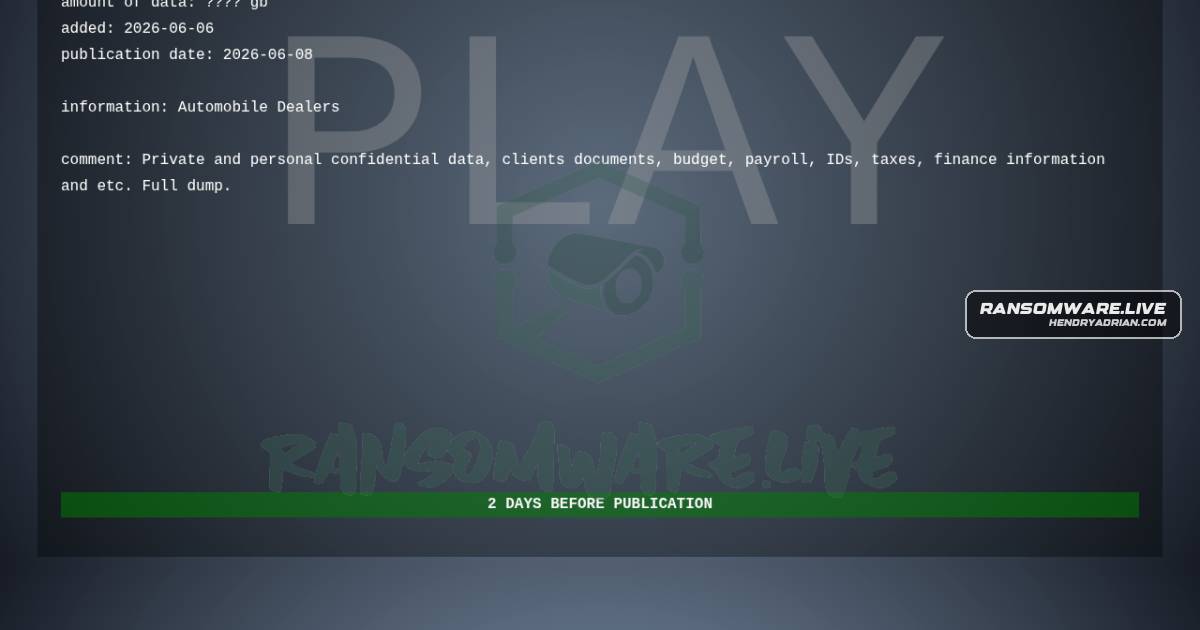
A ransomware.live monitoring post attributes a ransomware claim involving UK-based Pearson Ford to the Play group. The post says the group claimed disruption and a payment demand but cannot confirm the claim.
Key points
- The monitoring post names Pearson Ford in the United Kingdom as the claimed victim.
- It attributes the ransomware claim to the Play group and links it to the group's leak-site post.
- The post alleges malware was used to disrupt operations and demand payment to restore access.
- The monitoring service says it cannot confirm the claim; no victim statement or independent verification is provided.
Article Details
- Victim
- Pearson Ford
- Encryption Status
- Unknown; the article says the incident is based on public group claims and does not confirm encryption.
- Exfiltration Status
- Unknown; exfiltration is not reported.
- Ransom Demand
- The attackers allegedly demanded payment in exchange for restoring access; no amount is stated.
- Leak Status
- Unknown; publication of victim data is not reported.