
Validin Identifies 6,113 Suspected Domains in GHOST STADIUM Investigation
Summary
Validin researchers identified 6,113 suspected domains associated with GHOST STADIUM and found 3,079 resolving and not parked at analysis time. Shared page fingerprints and paths suggest kit reuse; the domains are not all confirmed malicious.
Key points
- The investigation expanded on Group-IB reporting about a phishing kit targeting World Cup fans and ticket buyers.
- Researchers identified 6,113 suspected domains; 3,079 were resolving and not parked at analysis time. The researchers cautioned that the domains were not all confirmed malicious.
- Identical response features, including HTML strings and a favicon hash, plus repeated World Cup-themed paths were used to identify related infrastructure and suggest shared kit deployment.
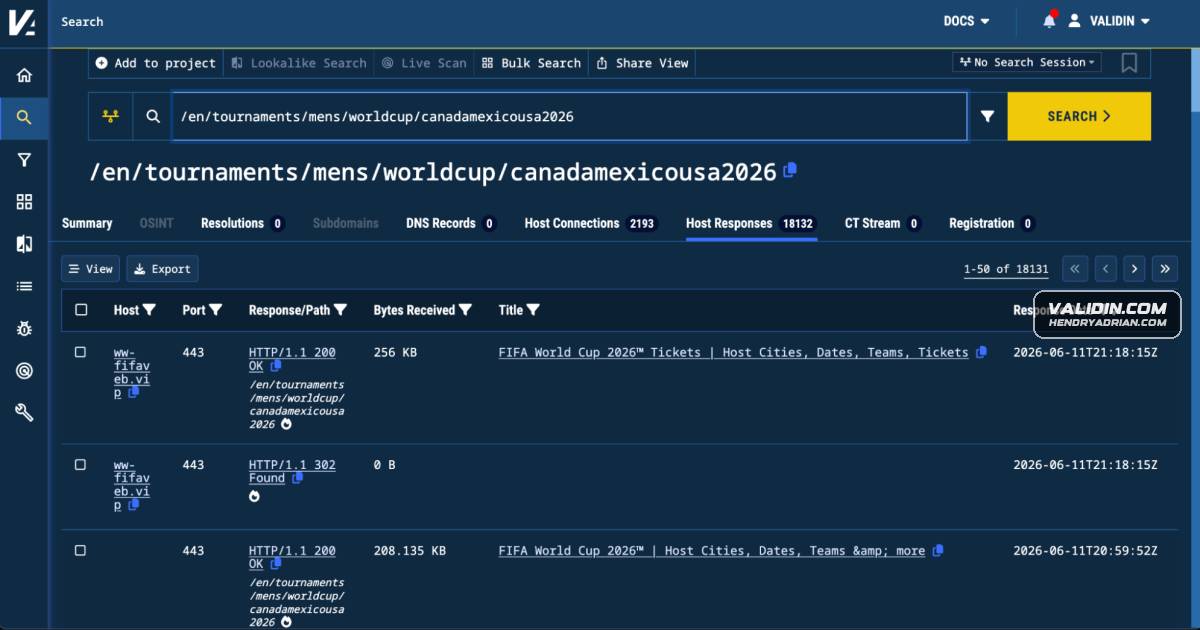
- A search for one repeated path returned about 600 domains; a variant returned 22 more. Lookalike-domain searches produced 5,649 results.
- Most active domains observed were fronted by Cloudflare, limiting direct visibility into origin infrastructure.
- Chinese-language JavaScript comments were consistent with Group-IB’s attribution assessment, but the article notes they are not sufficient on their own to identify malicious domains.
- Defenders can hunt for the anomalous HTML strings, repeated paths, language comments, and FIFA-themed lookalike domains; the researchers advise caution when using the suspected-domain list for blocking.
Article Details
- Attack Vectors
- FIFA-themed phishing pages impersonated ticketing, hospitality, streaming, and gambling services.
- The operators used bulk domain registration and reused a phishing kit across domains, including repeated World Cup-themed paths.
- Many identified domains were fronted by Cloudflare, obscuring their origin infrastructure.
- Defensive Notes
- Monitor for the anomalous HTML string "FIFA World Cup 2026TOfficial Hospitality" and the malformed hospitality marketing phrase identified in the article.
- Hunt for the paths /en/tournaments/mens/worldcup/canadamexicousa2026 and /en/tournaments/mens/worldcup/canadamexicousa2026.html.
- Use the Chinese-language JavaScript comments "Googleç¿»è¯åå§åå½æ°" and "ç½ç«é»è®¤è¯è¨" as secondary fingerprints, not standalone proof of maliciousness.
- Monitor recently registered FIFA-themed lookalike domains and DNS changes; the article advises caution because identified domains were suspected but not all explicitly confirmed as malicious.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | boecey[.]com | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | fifa-ticket-26[.]com | Representative domain from the reported GHOST STADIUM phishing analysis, used as a pivot for identifying related phishing infrastructure. |
| DOMAIN | fifa[.]beer | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | fifa[.]buzz | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | fifa[.]ceo | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | fifa[.]click | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | fifa[.]help | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | muksne[.]com | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | restributor[.]com | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | restributor[.]vip | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | wgss[.]lat | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | wkhby[.]one | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | wkhby[.]vip | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | worldcupticket[.]cc | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | worldcupticket[.]one | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
| DOMAIN | worldcupticket[.]vip | Listed in a path-based pivot for the phishing kit; the article treats domains in the discovered set as suspected, not individually confirmed, malicious infrastructure. |
MITRE ATT&CK
Vendors
Tools
Validin#GHOSTSTADIUMValidin Python SDKWe enriched the result set with DNS resolution and registration data using the newly launched Validin Python SDK, then filtered for currently resolving domains and registration clusters.YARA[YARA Rule Strings] Chinese-language developer comments in JavaScript – “Googleç¿»è¯åå§åå½æ°”, “ç½ç«é»è®¤è¯è¨”