
Resecurity Reports Anubis Ransomware Attack on Adriatic Port Authority
Summary
Resecurity reports that Anubis ransomware disrupted the Adriatic Port Authority, with files allegedly encrypted, data exfiltrated and a $10 million ransom demanded. The article provides no independent corroboration.
Key points
- Resecurity says attackers accessed the authority’s network through a spear-phishing email attachment, then moved laterally using privilege escalation and unpatched systems.
- The article claims thousands of files were encrypted, disrupting cargo tracking, shipping schedules and customs processing and forcing vessels to reroute.
- Resecurity says contracts and employee records were exfiltrated; the article reports a $10 million Bitcoin ransom demand and a threat to publish data within seven days.
- The article says the attack used IT systems rather than directly targeting operational technology, but affected port operations.
- It reports that affected systems were isolated, forensic teams investigated, and recovery relied on backups; negotiations reportedly took place.
- The article offers general recommendations including patching, stronger access controls, staff training and tested backups.
Article Details
- Victim Organization
- Adriatic Port Authority
- Incident Type
- Ransomware attack involving alleged spear-phishing initial access, file encryption, data exfiltration, and extortion.
- Data Types Exposed
- Contracts
- Employee records
- Safety plans and information about security operations
- Affected Records
- Thousands of files were reportedly encrypted; the number of affected records or individuals was not disclosed.
- Affected Data Size
- Not disclosed
- Operational Impact
- Cargo tracking, shipping schedules, and customs processing were reportedly inaccessible. The port could not process incoming and outgoing shipments, vessels were forced to reroute, and recovery efforts used backups.
- Ransom Or Extortion
- The group reportedly demanded 10 million USD in Bitcoin and threatened to publish stolen data within seven days. The article says negotiations reportedly took place, but does not state whether a ransom was paid.
- Claim Status
- confirmed
MITRE ATT&CK
CVE
CVE-2025-26399or derivatives of existing CVEs, such as SonicWall VPNs (lacking MFA), SolarWinds Web Help Desk (CVE-2025-26399), Cisco SSL VPNs, and CitrixBleed2 (CVE-2025-5777).CVE-2025-5777VPNs (lacking MFA), SolarWinds Web Help Desk (CVE-2025-26399), Cisco SSL VPNs, and CitrixBleed2 (CVE-2025-5777).
Threat Actors
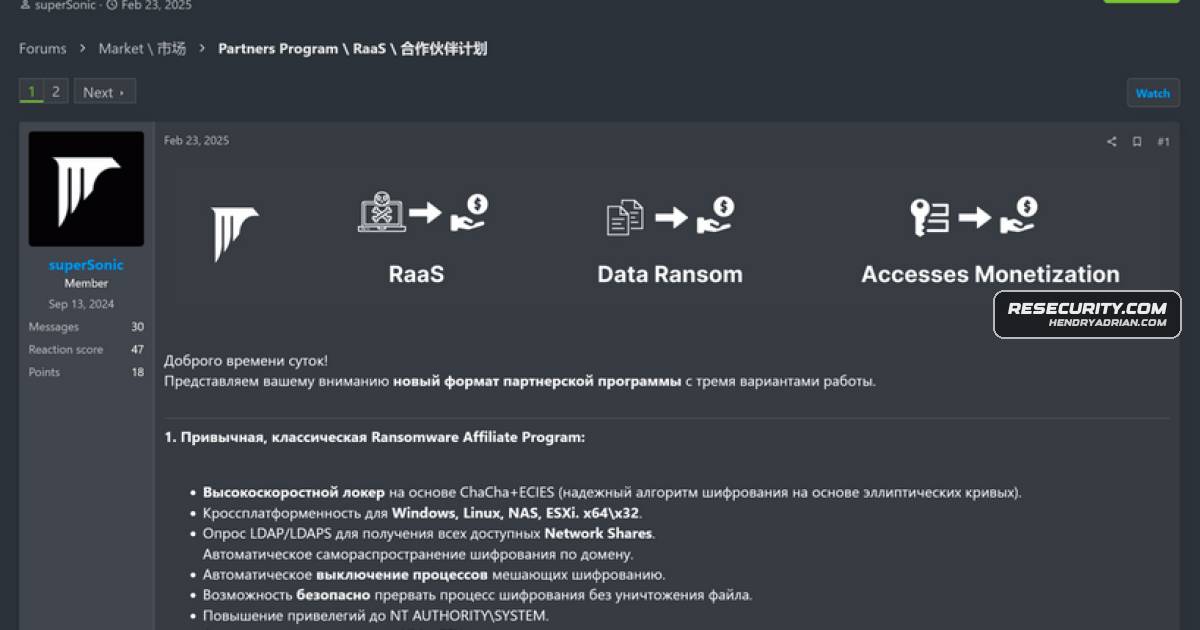
AnubisThe article identifies the Anubis ransomware group as responsible for the Adriatic Port Authority attack. It describes initial access by spear-phishing as Resecurity's belief and the 10 million USD ransom demand as reported.Anubis__mediaNamed as an alias used by the Anubis group on XSS and Exploit.superSonicNamed as an alias used by the Anubis group on RAMP.
Malware
Vendors
Ciscoof existing CVEs, such as SonicWall VPNs (lacking MFA), SolarWinds Web Help Desk (CVE-2025-26399), Cisco SSL VPNs, and CitrixBleed2 (CVE-2025-5777).SolarWindsthe use of N-day vulnerabilities or derivatives of existing CVEs, such as SonicWall VPNs (lacking MFA), SolarWinds Web Help Desk (CVE-2025-26399), Cisco SSL VPNs, and CitrixBleed2 (CVE-2025-5777).SonicWalltakeover (ATO), along with the use of N-day vulnerabilities or derivatives of existing CVEs, such as SonicWall VPNs (lacking MFA), SolarWinds Web Help Desk (CVE-2025-26399), Cisco SSL VPNs, and CitrixBleed2
Products
AzureThe malicious activity was conducted strictly by exploiting IT system vulnerabilities (for e.g., insecure accounts managing Office 365 / Azure), but it resulted in effects within the cyber-physical domain.Office 365The malicious activity was conducted strictly by exploiting IT system vulnerabilities (for e.g., insecure accounts managing Office 365 / Azure), but it resulted in effects within the cyber-physical domain.SolarWinds Web Help Deskof N-day vulnerabilities or derivatives of existing CVEs, such as SonicWall VPNs (lacking MFA), SolarWinds Web Help Desk (CVE-2025-26399), Cisco SSL VPNs, and CitrixBleed2 (CVE-2025-5777).
Countries
AustraliaOperating globally, Anubis has been linked to attacks on healthcare, construction, and engineering sectors in Australia, Canada, Peru, and the U.S.CanadaOperating globally, Anubis has been linked to attacks on healthcare, construction, and engineering sectors in Australia, Canada, Peru, and the U.S.PeruOperating globally, Anubis has been linked to attacks on healthcare, construction, and engineering sectors in Australia, Canada, Peru, and the U.S.United StatesOperating globally, Anubis has been linked to attacks on healthcare, construction, and engineering sectors in Australia, Canada, Peru, and the U.S.
Industries
ConstructionOperating globally, Anubis has been linked to attacks on healthcare, construction, and engineering sectors in Australia, Canada, Peru, and the U.S.EngineeringAnubis Ransomware is a highly adaptive, multi-stage threat targeting critical infrastructure, leveraging both technical exploits (notably VPN and web app vulnerabilities) and social engineering for initial access.HealthcareOperating globally, Anubis has been linked to attacks on healthcare, construction, and engineering sectors in Australia, Canada, Peru, and the U.S.MaritimeA severe ransomware attack orchestrated by the Anubis ransomware group targeted the Adriatic Port Authority, crippling its operations and disrupting maritime logistics across the region.