
Fox Kitten Combines Espionage With Ransomware Access Brokering
Summary
SOCRadar profiles Iranian state-linked Fox Kitten, describing exploitation of VPN and firewall flaws, credential theft, tunneling and custom backdoors, alongside espionage and access brokering for ransomware affiliates. It also outlines defensive measures.
Key points
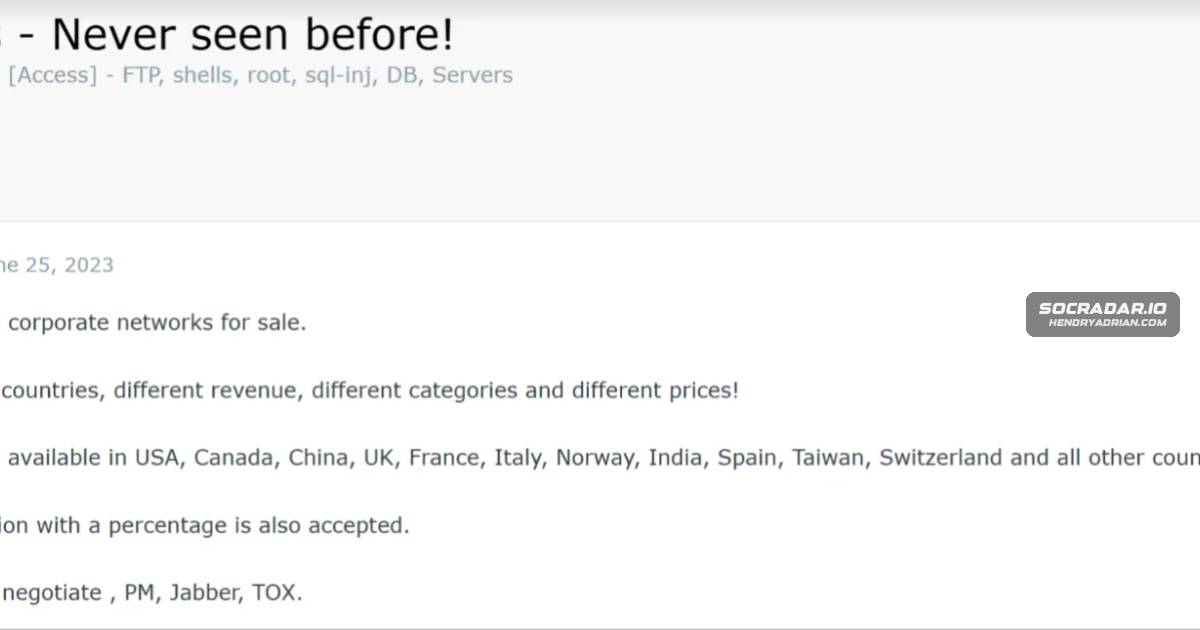
- The article describes Fox Kitten as an Iranian state-linked actor active since at least 2017, with espionage objectives and a parallel operation selling network access to ransomware affiliates.
- It reports that the group targets exposed VPNs, firewalls and remote access gateways, rapidly exploiting vulnerabilities including CVE-2024-24919 and CVE-2024-3400.
- Reported post-compromise activity includes credential harvesting from LSASS and Active Directory, web shells and scheduled tasks for persistence, and lateral movement using RDP, SMB, SSH and VNC.
- The article identifies HanifNet, HXLibrary and NeoExpressRAT as backdoors used in more recent intrusions, and describes proxy and tunneling tools used for command-and-control.
- It summarizes reported campaigns involving critical infrastructure in the Middle East, ransomware affiliates including NoEscape, Ransomhouse and ALPHV, and Pay2Key attacks against Israeli organizations.
- Recommended defenses include patching perimeter devices, monitoring for web shells and tunneling tools, protecting credentials, reviewing persistence mechanisms and segmenting networks.
Article Details
- Attack Vectors
- Exploitation of internet-facing VPN concentrators, firewalls, and remote access gateways for initial access.
- Brute-force attempts against RDP credentials as a secondary access path.
- Credential theft and payload staging using PowerShell; account manipulation using Windows Command Shell.
- Persistence through web shells, masquerading scheduled tasks, elevated local administrator accounts, and replacement of accessibility executables.
- Lateral movement using stolen credentials over RDP, SMB, SSH, and VNC, with PsExec for remote execution.
- Outbound tunneling and proxying to maintain access and communicate with C2 infrastructure.
- Defensive Notes
- Prioritize patching internet-facing VPN concentrators, firewalls, and remote access gateways.
- Scan internet-facing servers for unexpected web shells and changes to IIS modules.
- Monitor for tunneling tools including ngrok, FRPC, Chisel, Plink, and ReverseSocks5, and investigate unusual outbound connections to cloud relay services.
- Monitor for LSASS access, Volume Shadow Copy activity followed by NTDS reads, KeePass database access, and abnormal RDP logins.
- Review scheduled tasks, local administrator accounts, and accessibility executable changes for persistence.
- Use network segmentation to limit internal pivoting and monitor for TightVNC installation and PsExec or SMB-based lateral movement.
MITRE ATT&CK
T1003.001 · LSASS MemoryThe group uses prodump, described as a renamed ProcDump variant, to dump credentials from LSASS memory.T1003.003 · NTDSFox Kitten uses Volume Shadow Copy to extract NTDS.dit for offline Active Directory credential harvesting.T1021.001 · Remote Desktop ProtocolThe article reports that Fox Kitten relies on RDP with stolen credentials for lateral movement.T1053.005 · Scheduled TaskFox Kitten creates scheduled tasks, sometimes named to resemble legitimate system tasks, to maintain access.T1059.001 · PowerShellPowerShell is used for credential access and payload staging.T1059.003 · Windows Command ShellWindows Command Shell (cmd.exe) has been observed in account manipulation tasks.T1090 · ProxyThe group uses FRPC, ngrok, Glider Proxy, ReverseSocks5, Chisel, and MeshCentral for proxying or tunneled access.T1110 · Brute ForceThe article says Fox Kitten uses brute force against RDP credentials as a secondary access path.T1133 · External Remote ServicesFox Kitten targets exposed VPN concentrators and remote access gateways to enter victim environments.T1136.001 · Local AccountThe article reports creation of elevated local administrator accounts for long-term access.T1190 · Exploit Public-Facing ApplicationThe article reports that Fox Kitten gains initial access by exploiting internet-facing VPN and firewall appliances.T1505.003 · Web ShellWeb shells, including China Chopper and custom variants, are deployed on compromised servers for persistence.T1546.008 · Accessibility FeaturesFox Kitten replaces accessibility executables to launch a command prompt at the login screen.T1569.002 · Service ExecutionFox Kitten uses PsExec for remote command execution across compromised hosts.T1572 · Protocol TunnelingFox Kitten uses reverse proxies and tunneling tools to establish outbound tunnels from victim environments.
CVE
CVE-2019-11510[CVE ] exploited vulnerabilities in perimeter devices – CVE-2019-11510, CVE-2024-24919, and other 5 CVEsCVE-2019-19781CVE-2019-19781 — Citrix ADC/Gateway directory traversalCVE-2020-5902CVE-2020-5902 — F5 BIG-IP remote code executionCVE-2022-1388CVE-2022-1388 — F5 BIG-IP authentication bypassCVE-2023-3519CVE-2023-3519 — Citrix NetScaler ADC/Gateway code injectionCVE-2024-24919[CVE ] exploited vulnerabilities in perimeter devices – CVE-2019-11510, CVE-2024-24919, and other 5 CVEsCVE-2024-3400CVE-2024-3400 — Palo Alto PAN-OS command injection (zero-day)
Threat Actors
ALPHVThe article identifies ALPHV (also called BlackCat) affiliates as ransomware partners to whom Fox Kitten allegedly provided network access and credentials.BlackCatThe article gives BlackCat as another name for ALPHV, whose affiliates it identifies as ransomware partners to whom Fox Kitten allegedly provided network access and credentials.Br0k3rThe article says Fox Kitten operators identify themselves as Br0k3r and reports that the 2024 ransomware-facilitation advisory attributed activity to Fox Kitten operating under this handle.Fox KittenThe article describes Fox Kitten as an Iranian state-sponsored group involved in espionage, access brokering, and facilitating ransomware operations.Lemon SandstormThe article identifies Lemon Sandstorm as an alias under which Fox Kitten is tracked.NoEscapeThe article identifies NoEscape affiliates as ransomware partners to whom Fox Kitten allegedly provided network access and credentials.PARISITEThe article identifies Parisite as an alias under which Fox Kitten is tracked.Pioneer KittenThe article identifies Pioneer Kitten as an alias under which Fox Kitten is tracked.RansomHouseThe article identifies Ransomhouse affiliates as ransomware partners to whom Fox Kitten allegedly provided network access and credentials.RUBIDIUMThe article identifies RUBIDIUM as an alias under which Fox Kitten is tracked.UNC757The article identifies UNC757 as an alias under which Fox Kitten is tracked.xplfinderThe article says Fox Kitten operated under the handle xplfinder as of 2024 and reports that the ransomware-facilitation advisory attributed activity to Fox Kitten using this handle.
Malware
HanifNetIt has repeatedly exploited internet-facing VPN and firewall devices worldwide, using tools and custom malware such as HanifNet, HXLibrary, NeoExpressRAT, and Pay2Key to maintain access and support extortion operations.HXLibraryIt has repeatedly exploited internet-facing VPN and firewall devices worldwide, using tools and custom malware such as HanifNet, HXLibrary, NeoExpressRAT, and Pay2Key to maintain access and support extortion operations.NeoExpressRATIt has repeatedly exploited internet-facing VPN and firewall devices worldwide, using tools and custom malware such as HanifNet, HXLibrary, NeoExpressRAT, and Pay2Key to maintain access and support extortion operations.Pay2KeyIt has repeatedly exploited internet-facing VPN and firewall devices worldwide, using tools and custom malware such as HanifNet, HXLibrary, NeoExpressRAT, and Pay2Key to maintain access and support extortion operations.
Vendors
Check PointThe group rapidly weaponizes newly disclosed vulnerabilities in products from Pulse Secure, Citrix, F5, Palo Alto, and Check Point for initial access.CitrixThe group rapidly weaponizes newly disclosed vulnerabilities in products from Pulse Secure, Citrix, F5, Palo Alto, and Check Point for initial access.F5The group rapidly weaponizes newly disclosed vulnerabilities in products from Pulse Secure, Citrix, F5, Palo Alto, and Check Point for initial access.FortinetClearSky’s original Fox Kitten disclosure documented a broad exploitation campaign targeting unpatched Pulse Secure, Citrix, and Fortinet VPN appliances at scale.Palo Alto NetworksThe group rapidly weaponizes newly disclosed vulnerabilities in products from Pulse Secure, Citrix, F5, Palo Alto, and Check Point for initial access.Pulse SecureThe group rapidly weaponizes newly disclosed vulnerabilities in products from Pulse Secure, Citrix, F5, Palo Alto, and Check Point for initial access.
Products
Check Point Security GatewayCVE-2024-24919 — Check Point Security Gateway information disclosureCitrix ADC/GatewayCVE-2019-19781 — Citrix ADC/Gateway directory traversalCitrix NetScaler ADC/GatewayCVE-2023-3519 — Citrix NetScaler ADC/Gateway code injectionF5 BIG-IPCVE-2020-5902 — F5 BIG-IP remote code executionFortinet VPN appliancesClearSky’s original Fox Kitten disclosure documented a broad exploitation campaign targeting unpatched Pulse Secure, Citrix, and Fortinet VPN appliances at scale.KeePass[T1555.005 ] Credentials from Password Stores: Password Managers – Read KeePass databases to steal stored secrets (‘reading KeePass databases using targeted scripts’).Microsoft Teams[T1213.005 ] Data from Information Repositories: Messaging Applications – Accessed Microsoft Teams messages for intelligence (‘accesses Microsoft Teams to mine communications’).PAN-OSCVE-2024-3400 — Palo Alto PAN-OS command injection (zero-day)Pulse Secure VPNCVE-2019-11510 — Pulse Secure VPN arbitrary file read
Tools
Angry IP scanner[T1046 ] Network Service Discovery – Used Nmap and Angry IP Scanner for network discovery (‘Nmap and Angry IP Scanner for network discovery’).Chisel[T1090 ] Proxy – Used FRPC, ngrok, Glider Proxy, ReverseSocks5, Chisel, and MeshCentral as proxying tools (‘reverse proxy tools’).frpc[T1090 ] Proxy – Used FRPC, ngrok, Glider Proxy, ReverseSocks5, Chisel, and MeshCentral as proxying tools (‘reverse proxy tools’).Glider Proxy[T1090 ] Proxy – Used FRPC, ngrok, Glider Proxy, ReverseSocks5, Chisel, and MeshCentral as proxying tools (‘reverse proxy tools’).MeshCentral[T1090 ] Proxy – Used FRPC, ngrok, Glider Proxy, ReverseSocks5, Chisel, and MeshCentral as proxying tools (‘reverse proxy tools’).Ngrok[T1090 ] Proxy – Used FRPC, ngrok, Glider Proxy, ReverseSocks5, Chisel, and MeshCentral as proxying tools (‘reverse proxy tools’).Nmap[T1046 ] Network Service Discovery – Used Nmap and Angry IP Scanner for network discovery (‘Nmap and Angry IP Scanner for network discovery’).PsExec[T1569.002 ] System Services: Service Execution – Used PsExec for remote command execution across the network (‘uses PsExec for remote command execution across the network’).ReverseSocks5[T1090 ] Proxy – Used FRPC, ngrok, Glider Proxy, ReverseSocks5, Chisel, and MeshCentral as proxying tools (‘reverse proxy tools’).SSHMinionA custom tool, SSHMinion, has also been attributed to the group for encrypted tunneled communication.
Countries
AzerbaijanGeographically, operations concentrate on the United States, Israel, Azerbaijan, and the United Arab Emirates, with additional activity across the broader Middle East and North Africa.IsraelGeographically, operations concentrate on the United States, Israel, Azerbaijan, and the United Arab Emirates, with additional activity across the broader Middle East and North Africa.United Arab EmiratesGeographically, operations concentrate on the United States, Israel, Azerbaijan, and the United Arab Emirates, with additional activity across the broader Middle East and North Africa.United StatesFox Kitten has targeted organizations across the Middle East, North Africa, Europe, Australia, and North America, with documented victims in the United States.
Industries
DefensePost-compromise activity includes credential theft, tunneling-based persistence, lateral movement, cloud and messaging collection, and defense evasion through masquerading and timestomping.EducationFox Kitten targets organizations across a broad range of sectors including oil and gas, technology, government, defense, healthcare, manufacturing, engineering, finance, education, and telecommunications.EngineeringFox Kitten targets organizations across a broad range of sectors including oil and gas, technology, government, defense, healthcare, manufacturing, engineering, finance, education, and telecommunications.financeFox Kitten targets organizations across a broad range of sectors including oil and gas, technology, government, defense, healthcare, manufacturing, engineering, finance, education, and telecommunications.GovernmentThat dual mission, combined with a persistent focus on exploiting internet-facing VPN and firewall devices, makes Fox Kitten one of the most disruptive and financially dangerous government-backed groups.HealthcareFox Kitten targets organizations across a broad range of sectors including oil and gas, technology, government, defense, healthcare, manufacturing, engineering, finance, education, and telecommunications.ManufacturingFox Kitten targets organizations across a broad range of sectors including oil and gas, technology, government, defense, healthcare, manufacturing, engineering, finance, education, and telecommunications.Oil and gasFox Kitten targets organizations across a broad range of sectors including oil and gas, technology, government, defense, healthcare, manufacturing, engineering, finance, education, and telecommunications.TechnologyFox Kitten targets organizations across a broad range of sectors including oil and gas, technology, government, defense, healthcare, manufacturing, engineering, finance, education, and telecommunications.TelecommunicationsFox Kitten targets organizations across a broad range of sectors including oil and gas, technology, government, defense, healthcare, manufacturing, engineering, finance, education, and telecommunications.