
Fake Reviews and VirusTotal Activity Promote Crypto Clipboard Hijacker
Summary
Check Point Research reports an unknown actor used fake reviews, inflated downloads and coordinated platform activity to promote malicious tools hiding a Rust clipboard hijacker. It replaces matching crypto wallet addresses on Windows and macOS with attacker-controlled,
Key points
- Check Point Research reported that an unknown actor used paid or promoted posts, fake accounts and a WordPress phishing page to advertise malicious software.
- The software conceals a Rust-based clipboard hijacker in Solana and Pump.fun sniper bots and crash-game predictors, reportedly targeting Windows and macOS users.
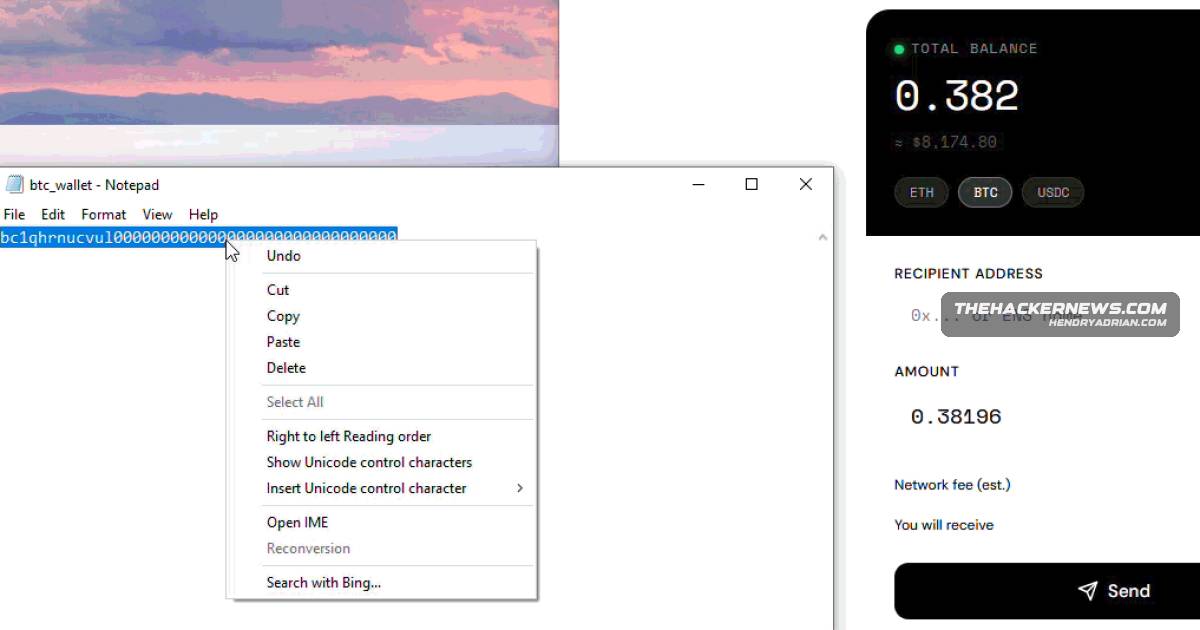
- The malware monitors for cryptocurrency wallet addresses in the clipboard and replaces matches with attacker-controlled addresses from a hard-coded list.
- The actor allegedly used coordinated VirusTotal accounts, described as Ghost Networks, to upvote files and post positive comments intended to make malicious files appear safe.
- Check Point said the actor operated at least six GitHub accounts; one repository had 146 stars and 62 forks.
- SourceForge showed 44,485 downloads, including a suspicious 37,460 attributed to Android devices, although the software was offered only for Windows and macOS.
- The campaign also used a YouTube channel with more than 91,000 subscribers, AI-generated narrators and positive comments to promote the tools.
Article Details
- Event Type
- Cross-platform malware distribution campaign using fake reputation and promotional tactics
- Impact
- A Rust-based clipboard hijacker targets Windows and macOS users. It replaces copied cryptocurrency wallet addresses with attacker-controlled addresses, potentially diverting digital assets to the attackers.
Products
GitHubCheck Point Research uncovered a threat actor using fake reputation tactics across news sites, GitHub, SourceForge, YouTube, VirusTotal, and a WordPress phishing hub to promote malicious warez.SourceForgeCheck Point Research uncovered a threat actor using fake reputation tactics across news sites, GitHub, SourceForge, YouTube, VirusTotal, and a WordPress phishing hub to promote malicious warez.VirusTotalCheck Point Research uncovered a threat actor using fake reputation tactics across news sites, GitHub, SourceForge, YouTube, VirusTotal, and a WordPress phishing hub to promote malicious warez.WordPressCheck Point Research uncovered a threat actor using fake reputation tactics across news sites, GitHub, SourceForge, YouTube, VirusTotal, and a WordPress phishing hub to promote malicious warez.YouTubeCheck Point Research uncovered a threat actor using fake reputation tactics across news sites, GitHub, SourceForge, YouTube, VirusTotal, and a WordPress phishing hub to promote malicious warez.