
Operation Endgame Takes Down 106 SocGholish Servers and Cleans Nearly 15,000 WordPress Sites
Summary
Dutch authorities and international partners disrupted SocGholish infrastructure, took down 106 servers and cleaned 14,971 infected WordPress sites. Owners were urged to update CMS software, change credentials and remove suspicious accounts.
Key points
- The disruption was carried out by Dutch law enforcement with counterparts from Canada, Germany and the U.S. as part of Operation Endgame.
- Authorities took down 106 servers linked to SocGholish and cleaned 14,971 infected WordPress sites.
- Website owners were notified to update their CMS, change credentials and delete suspicious accounts.
- SocGholish, also known as FakeUpdates, is a JavaScript downloader active since 2017 that delivers follow-on malware.
- The malware is distributed through compromised websites, deceptive software-update lures, domain shadowing and traffic filtering.
- The article describes use of SocGholish by multiple actors and affiliates, with follow-on payloads including LockBit, AsyncRAT and NetSupport RAT.
Article Details
- Event Type
- International law enforcement disruption of SocGholish infrastructure and cleanup of infected websites.
- Impact
- Authorities took down 106 servers linked to SocGholish and cleaned 14,971 infected WordPress sites. The disruption was intended to limit criminals’ access to infected systems and reduce further malware spread and the risk of those systems being used in cyberattacks.
MITRE ATT&CK
People
Threat Actors
DEV-0243Identified by the article as an alias for Evil Corp, which it names as a threat actor using SocGholish to deliver follow-on payloads.DridexNamed as a threat actor that has used SocGholish to deliver follow-on payloads.Evil CorpNamed as a threat actor that has used SocGholish to deliver follow-on payloads. The article says DEV-0243, Indrik Spider, and UNC2165 are aliases for Evil Corp.EvilCorpIdentified by the article as an alias for Evil Corp, which it names as a threat actor using SocGholish to deliver follow-on payloads.Gold PreludeListed among the aliases under which operators of SocGholish have been tracked; the article does not specify an equivalence between these aliases.Indrik SpiderIdentified by the article as an alias for Evil Corp, which it names as a threat actor using SocGholish to deliver follow-on payloads.JunkyTDSNamed as an affiliate that has sold traffic to the SocGholish framework.LockBitNamed as a threat actor that has used SocGholish to deliver follow-on payloads; also listed as a payload delivered through SocGholish infections.Mustard TempestListed among the aliases under which operators of SocGholish have been tracked; the article does not specify an equivalence between these aliases.Parrot TDSNamed as an affiliate that has sold traffic to the SocGholish framework.Purple VallhundListed among the aliases under which operators of SocGholish have been tracked; the article does not specify an equivalence between these aliases.RansomHubNamed as a threat actor that has used SocGholish to deliver follow-on payloads.Raspberry RobinNamed as a threat actor that has used SocGholish to deliver follow-on payloads.RomComArctic Wolf reportedly observed SocGholish being used by RomCom to deliver the Mythic Agent in November 2025.TA2726Identified as a traffic-distribution-system operator and as an affiliate that has sold traffic to the SocGholish framework.TA569Listed among the aliases under which SocGholish operators have been tracked. Proofpoint said TA569 opportunistically compromises websites across many industries.UNC1543Listed among the aliases under which operators of SocGholish have been tracked; the article does not specify an equivalence between these aliases.
Malware
AsyncRATMintsLoader, which, in turn, lead to the deployment of additional payloads like GhostWeaver, LockBit, AsyncRAT, and NetSupport RAT.GholoaderOrange Cyberdefense said it has observed SocGholish infections delivering loaders like Gholoader (another JavaScript-based loader) and MintsLoader, which, in turn, lead to the deployment of additional payloads likeGhostWeaverloader) and MintsLoader, which, in turn, lead to the deployment of additional payloads like GhostWeaver, LockBit, AsyncRAT, and NetSupport RAT.LockBitnext-stage malware from various threat actors like Evil Corp (aka DEV-0243, Indrik Spider, and UNC2165), LockBit, RansomHub, Dridex, and Raspberry Robin (aka Roshtyak).MintsLoaderobserved SocGholish infections delivering loaders like Gholoader (another JavaScript-based loader) and MintsLoader, which, in turn, lead to the deployment of additional payloads like GhostWeaver, LockBit, AsyncRAT, andMythic Agent2025, Arctic Wolf revealed that SocGholish was being used by the RomCom threat actors to deliver the Mythic Agent, highlighting the use of the initial access broker’s services by a broad range of actors with variedNetSupport RATin turn, lead to the deployment of additional payloads like GhostWeaver, LockBit, AsyncRAT, and NetSupport RAT.SocGholishDutch law enforcement and international partners disrupted SocGholish infrastructure, took down 106 servers, and cleaned nearly 15,000 infected WordPress sites in Operation Endgame.
Products
Google ChromeIt’s distributed via compromised websites by masquerading as deceptive updates for web browsers like Google Chrome or Mozilla Firefox, and other popular software.Mozilla FirefoxIt’s distributed via compromised websites by masquerading as deceptive updates for web browsers like Google Chrome or Mozilla Firefox, and other popular software.WordPressDutch law enforcement and international partners disrupted SocGholish infrastructure, took down 106 servers, and cleaned nearly 15,000 infected WordPress sites in Operation Endgame.
Tools
KeitaroThreat actors have also employed commercial offerings like Keitaro and zTDS to filter traffic for redirection to SocGholish, or sending them to the original website or any other content if the visitor to the compromisedzTDSThreat actors have also employed commercial offerings like Keitaro and zTDS to filter traffic for redirection to SocGholish, or sending them to the original website or any other content if the visitor to the compromised
Countries
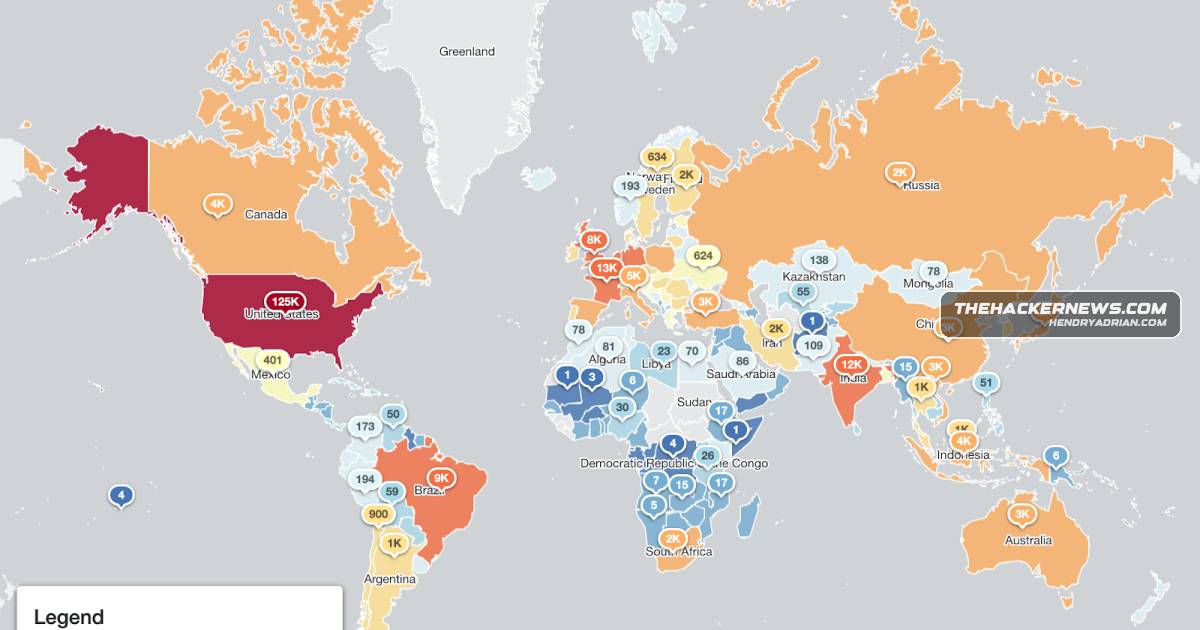
BrazilThe vast majority of the hacked sites were located in the U.S., followed by Germany, France, India, Brazil, Singapore, Italy, Indonesia, Canada, and Vietnam.CanadaDutch law enforcement authorities, along with counterparts from Canada , Germany, and the U.S., have disrupted malicious infrastructure associated with SocGholish and cleaned up nearly 15,000 infected WordPress websites.FranceThe vast majority of the hacked sites were located in the U.S., followed by Germany, France, India, Brazil, Singapore, Italy, Indonesia, Canada, and Vietnam.GermanyDutch law enforcement authorities, along with counterparts from Canada , Germany, and the U.S., have disrupted malicious infrastructure associated with SocGholish and cleaned up nearly 15,000 infected WordPress websites.IndiaThe vast majority of the hacked sites were located in the U.S., followed by Germany, France, India, Brazil, Singapore, Italy, Indonesia, Canada, and Vietnam.IndonesiaThe vast majority of the hacked sites were located in the U.S., followed by Germany, France, India, Brazil, Singapore, Italy, Indonesia, Canada, and Vietnam.ItalyThe vast majority of the hacked sites were located in the U.S., followed by Germany, France, India, Brazil, Singapore, Italy, Indonesia, Canada, and Vietnam.Netherlands“With these actions we deprive cybercriminals of access to infected computer systems,” Maikel Rollman of the Netherlands National High Tech Crime Unit said.SingaporeThe vast majority of the hacked sites were located in the U.S., followed by Germany, France, India, Brazil, Singapore, Italy, Indonesia, Canada, and Vietnam.United StatesDutch law enforcement authorities, along with counterparts from Canada , Germany, and the U.S., have disrupted malicious infrastructure associated with SocGholish and cleaned up nearly 15,000 infected WordPress websites.VietnamThe vast majority of the hacked sites were located in the U.S., followed by Germany, France, India, Brazil, Singapore, Italy, Indonesia, Canada, and Vietnam.
Industries
BankingSome of the most targeted verticals included government, education, banking, healthcare, non-IT services, financial services, IT consulting, utilities, insurance, and transportation.EducationSome of the most targeted verticals included government, education, banking, healthcare, non-IT services, financial services, IT consulting, utilities, insurance, and transportation.Financial ServicesSome of the most targeted verticals included government, education, banking, healthcare, non-IT services, financial services, IT consulting, utilities, insurance, and transportation.GovernmentSome of the most targeted verticals included government, education, banking, healthcare, non-IT services, financial services, IT consulting, utilities, insurance, and transportation.Healthcare“The actor has also compromised websites in virtually every industry, from nonprofits and schools, to healthcare and hospitals, to legal and real estate organizations.”InsuranceSome of the most targeted verticals included government, education, banking, healthcare, non-IT services, financial services, IT consulting, utilities, insurance, and transportation.IT ConsultingSome of the most targeted verticals included government, education, banking, healthcare, non-IT services, financial services, IT consulting, utilities, insurance, and transportation.Legal“The actor has also compromised websites in virtually every industry, from nonprofits and schools, to healthcare and hospitals, to legal and real estate organizations.”Nonprofits“The actor has also compromised websites in virtually every industry, from nonprofits and schools, to healthcare and hospitals, to legal and real estate organizations.”real estate“The actor has also compromised websites in virtually every industry, from nonprofits and schools, to healthcare and hospitals, to legal and real estate organizations.”TransportationSome of the most targeted verticals included government, education, banking, healthcare, non-IT services, financial services, IT consulting, utilities, insurance, and transportation.UtilitiesSome of the most targeted verticals included government, education, banking, healthcare, non-IT services, financial services, IT consulting, utilities, insurance, and transportation.