
Play ransomware group claims Locati Architects as a target
Summary
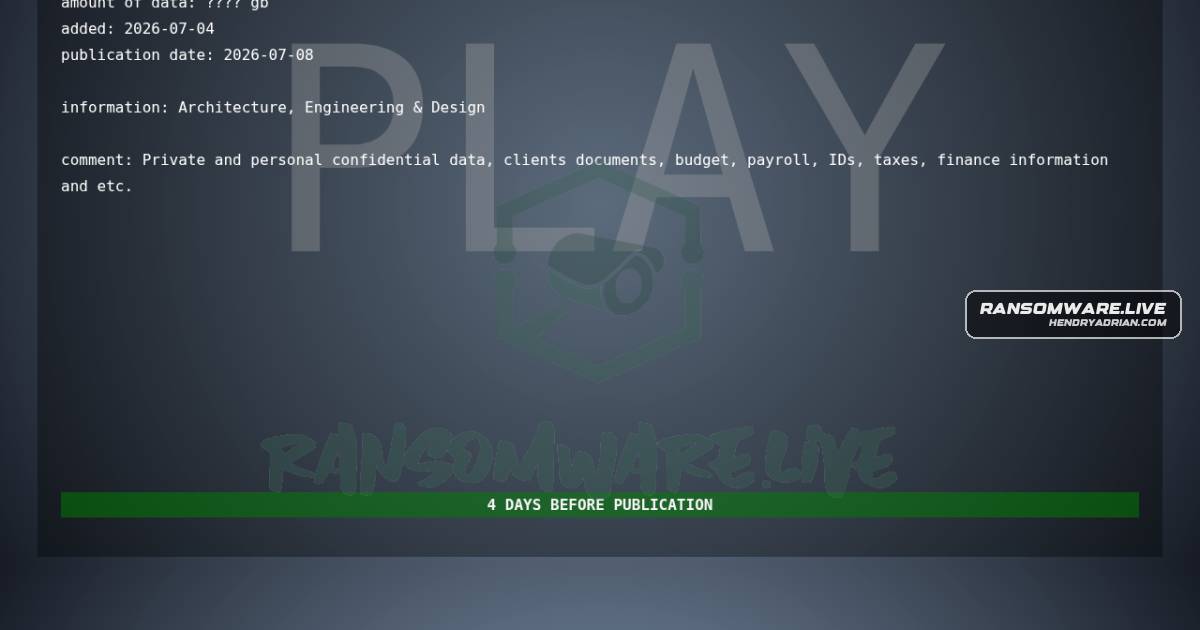
Ransomware.live records an unverified Play ransomware claim targeting Australia-based Locati Architects, dated July 4, 2026. The post alleges encryption and extortion pressure; the article says it cannot confirm the claim.
Key points
- The record names Australia-based construction firm Locati Architects as the claimed victim.
- The claim is attributed to the Play ransomware group and a linked group source; ransomware.live says it monitored the post.
- The post alleges data encryption and pressure to disrupt operations and demand payment.
- The article explicitly says it cannot confirm the group’s claims.
Article Details
- Victim
- Locati Architects
- Victim Domain
- Not disclosed
- Attack Date
- 2026-07-04
- Encryption Status
- Reported as part of an unverified group claim; not independently confirmed.
- Encrypted Size
- Not disclosed
- Exfiltration Status
- Unknown
- Exfiltrated Data
- Unknown
- Exfiltrated Size
- Not disclosed
- Ransom Demand
- The article says payment was threatened, but no amount is stated; the claim is unconfirmed.
- Leak Status
- No leak or publication is reported.