
Fake Itch.io Game Updates Deliver LummaStealer Through Patreon Links
Summary
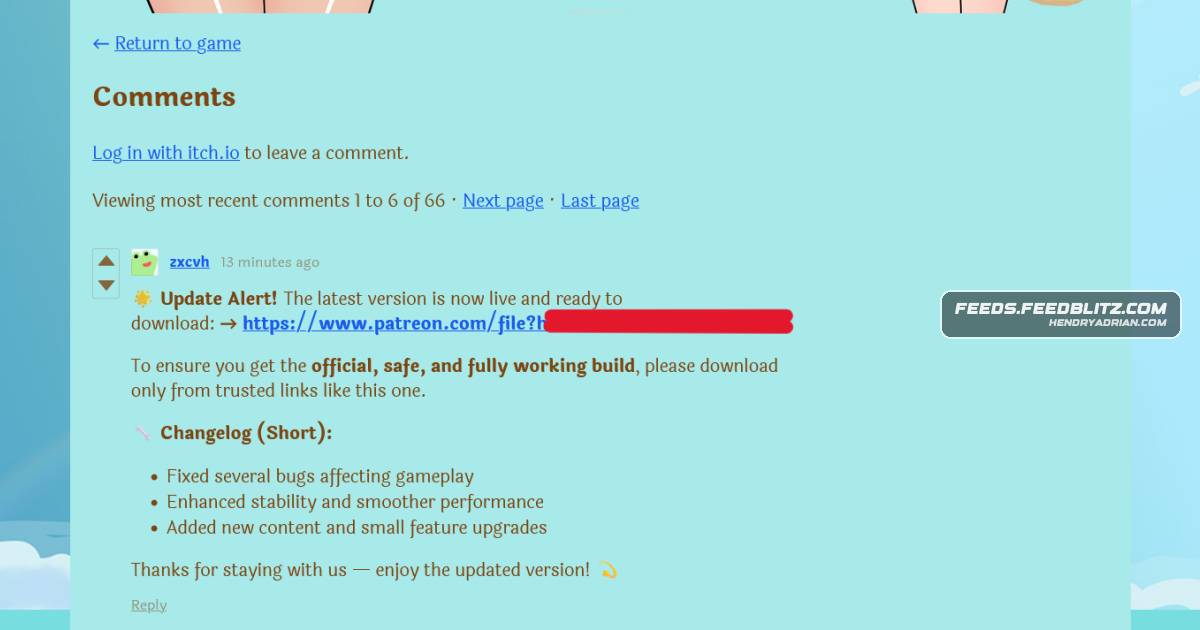
A campaign uses spam comments on legitimate Itch.io games to direct users to fake Patreon game updates that install LummaStealer. The malware uses extensive anti-analysis checks, and new malicious accounts continue appearing after some were removed.
Key points
- Newly created accounts post templated comments on legitimate Itch.io games, linking to Patreon-hosted downloads presented as game updates.
- The “Updated Version.zip” archive contains a nexe-compiled executable, game.exe, which runs obfuscated JavaScript.
- The malware checks system resources, usernames, running processes, display adapters, refresh rates, and disk models to detect analysis environments.
- It writes a DLL named modules.node to the Windows temporary directory and reflectively loads a LummaStealer payload.
- Different samples vary in encoding, names, and some anti-analysis methods, but share campaign identifiers and comment templates.
- Itch.io removed some malicious accounts, but new accounts were still posting the download links.
Article Details
- Attack Vectors
- Newly created Itch.io accounts post templated spam comments in legitimate games, directing users to Patreon links that download an archive named “Updated Version.zip”.
- The archive contains a nexe-compiled Node.js executable, game.exe, which uses anti-analysis checks and drops and loads a modules.node DLL containing a LummaStealer payload.
- Defensive Notes
- Treat unsolicited game-update links posted in game comments as suspicious and avoid downloading the linked archives.
- The malware checks system memory and CPU count, usernames, running processes, video-controller names, display refresh rate, and disk-drive model values to detect analysis or virtualized environments.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 102b99b00a60f33246bd89bd2b3cb9cfae2844d453484e932b3a5ca634fb308c | SHA-256 hash of the malicious game.exe executable. |
| SHA256 | 1d405b03bc5913b6b43c06550ef0b9b02196b270625e4dc5fa0c37e8a424be25 | SHA-256 hash of the malicious modules.node DLL dropped by the executable. |
| SHA256 | 79250523a057a7dd9a6080099c8c2f83eb683ab9b37ecab149fc73524f7c4bd1 | SHA-256 hash of the malicious “Updated Version.zip” archive. |
| SHA256 | 80e538cabade94e1883f9e72bb608dc02f79808aec48136b5bbb00c2a1717f64 | SHA-256 hash of the obfuscated JavaScript file mains.js extracted from the malicious executable. |
| SHA256 | a2bacb00dfdb338b496d3128705f76c8cc935e6bd33e06271fb3e34d769d0a2b | SHA-256 hash of the LummaStealer payload. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe JavaScript file mains.js is obfuscated, and the payloads are Base64-encoded.T1059.001 · PowerShellA newer sample uses a PowerShell command to query the system video adapter with Get-CimInstance.T1059.003 · Windows Command ShellThe malware executes Windows command-line commands including tasklist and wmic to inspect processes and system hardware.T1129 · Shared ModulesThe executable writes modules.node, a DLL, to the %temp% directory and loads it as a Node.js module.T1140 · Deobfuscate/Decode Files or InformationThe malware decodes Base64-encoded strings to write modules.node and load the LummaStealer payload.T1497.001 · System ChecksThe malware checks system memory and CPU count, usernames, running processes, video adapters, refresh rate, and disk models to identify virtualized or analysis environments and stop execution.
Malware
Products
Itch.ioAlongside Steam, indie game platforms such as Itch.io have also been recent targets, notably Malwarebytes’ analysis of fake Itch.io download pages containing malware that spread via compromised Discord accounts.Node.jswith any updates. Static analysis of the file reveals it is compiled with nexe, indicating that it is a Node.js application converted into a PE executable. To our knowledge no articles mentioning the use of thisPatreonAfter patches on mainstream gaming platforms like Steam, indie game platforms as well as Patreon have become the latest platforms for distributing malware.