
AWS GuardDuty Attack Sequences and Detective for Cloud Threat Investigation
· 16:46 · Watch on YouTube ↗
Summary
A demonstration shows how GuardDuty attack sequences and Detective investigation tools link simulated AWS activity, including possible S3 data access, role anomalies, and other findings, to support cloud threat hunting.
Key points
- The presenter says the findings came from penetration testing conducted to exercise AWS threat-detection and investigation services, not from a reported real-world incident.
- GuardDuty groups related signals, including S3 object access and parameter-store queries, into an attack sequence that may indicate potential data compromise.
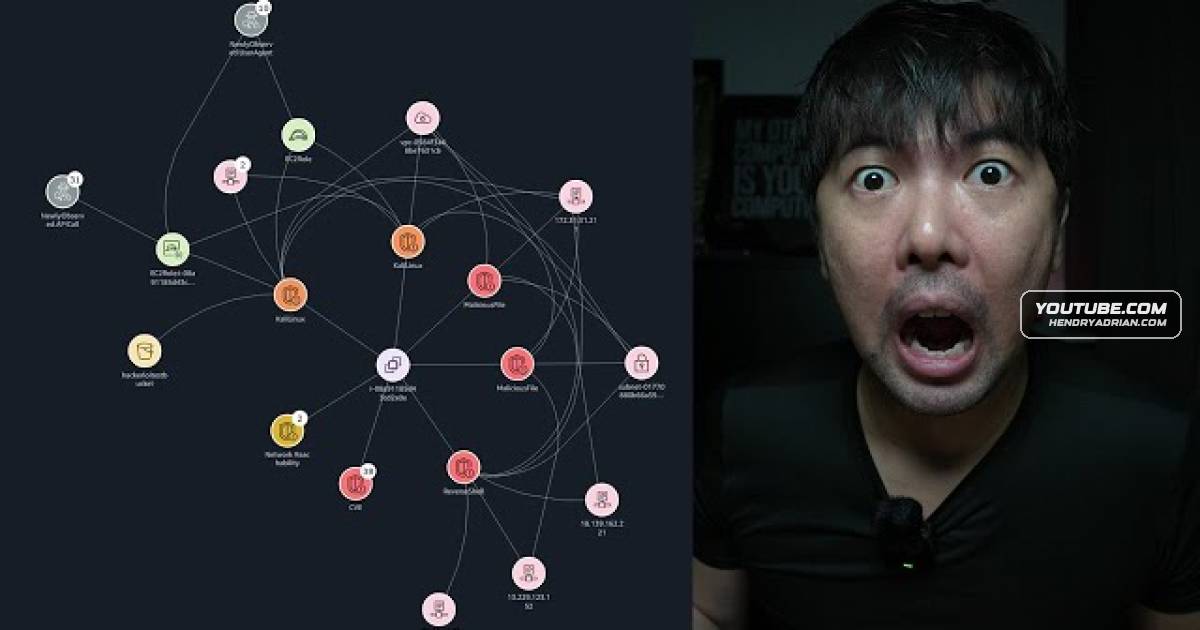
- Detective connects findings and entities, and visualizes activity over a time range to help investigators examine unusual roles, user agents, and network reachability.
- The demonstrated investigation surfaced findings involving a reverse shell, a malicious file, vulnerabilities, and possible credential access; the presenter describes the results as part of the test.
- The walkthrough shows investigation details such as role-policy changes, access-key creation, failed API calls, and role assumptions that can help guide threat hunting.
Article Details
- Topics
- [00:14] GuardDuty attack sequences and simulated AWS activity
- [01:23] Reviewing attack-sequence signals, S3 access, and parameter-store queries
- [04:23] Opening related findings in Detective for investigation
- [07:00] Using the investigation timeline to review findings over time
- [11:30] Examining anomalous role activity and possible privilege escalation or persistence
- [13:31] Searching AWS entities and reviewing API calls and role interactions