
Sophos Finds AI Coding Agents Triggering Endpoint Security Alerts
Summary
A week of Sophos Windows endpoint telemetry found AI coding agents triggering detections for credential access, execution and persistence. Sophos recommends narrowly scoping execution alerts while continuing to protect credential stores.
Key points
- Sophos analyzed seven days of Windows endpoint telemetry from June 2026, counting unique machines rather than raw events; it cautioned that the data represents one vendor's fleet, not an industry-wide picture.
- Credential access accounted for 56.2% of blocked activity and execution for 28.8%, according to Sophos.
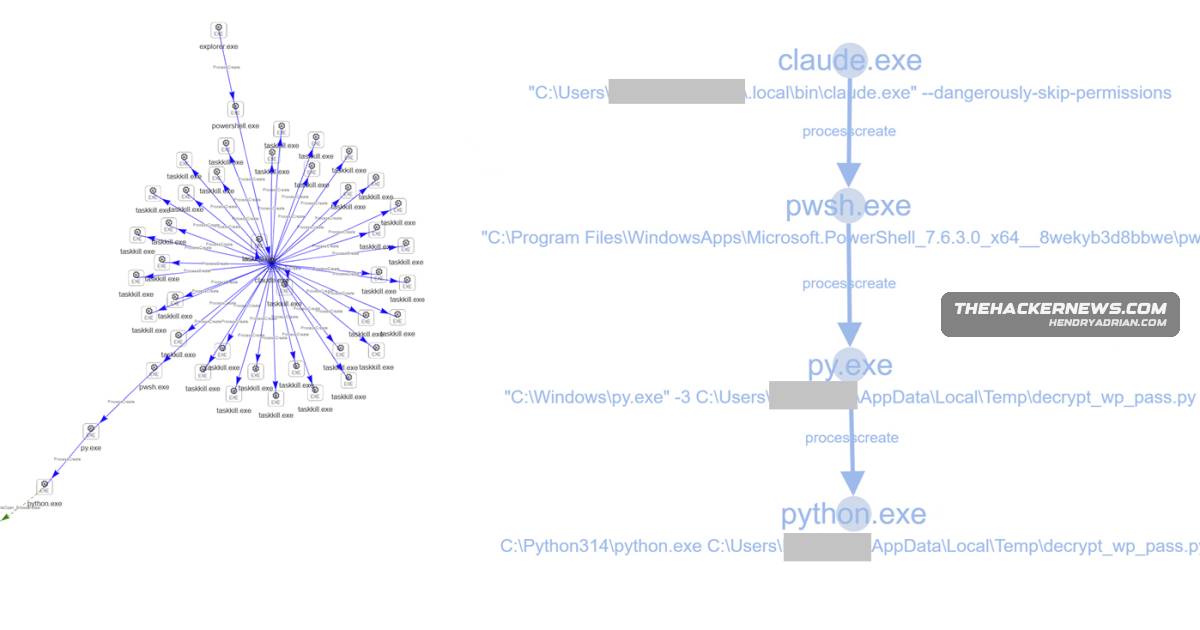
- Sophos observed Claude Code using DPAPI to decrypt saved browser data through a GStack skill; it said the activity appeared consistent with browser automation, though the behavior still warranted detection.
- Sophos also described Claude Code enumerating Windows Credential Manager and running a script that retrieved browser credential-store data.
- OpenAI Codex switched from certutil to bitsadmin after its initial attempt to download a Python installer was blocked; both are legitimate Windows utilities that attackers also abuse.
- Cursor triggered a persistence detection after writing a script to the startup folder; Sophos could not confirm what the script did.
- Sophos recommends scoping some execution alerts to known agent processes or paths, while maintaining protections for credential-store access and disabling Claude Code's --dangerously-skip-permissions mode through managed settings.
Article Details
- Publisher
- thehackernews.com
- Report Period
- June 2026
- Scope
- Seven days of Sophos behavioral-engine telemetry from Windows endpoints; a narrow view of one vendor's fleet, not an industry census.
- Sample Size
- Counted by unique machines; the number of machines was not disclosed.
- Key Statistics
- Credential access accounted for 56.2% of blocked activity in Sophos's June 2026 telemetry.
- Execution accounted for 28.8% of blocked activity in Sophos's June 2026 telemetry.
- The DPAPI browser-credential rule represented 42.6% of the credential-access group.
- CrowdStrike's 2026 Global Threat Report found that 82% of 2025 detections were malware-free.
- Recommendations
- Scope execution rules using agent parent processes and child processes, workspace or temporary paths, or download-target reputation.
- Continue treating browser-credential decryption and Credential Manager enumeration as sensitive behavior, even when performed by an AI agent.
- Disable Claude Code's --dangerously-skip-permissions mode through managed settings when that mode is causing alerts.
MITRE ATT&CK
T1059.001 · PowerShellPowerShell was used for browser-data access and to write a startup-folder script during the reported AI-agent activity.T1105 · Ingress Tool TransferOpenAI Codex attempted to fetch a Python installer using certutil and, after that was blocked, bitsadmin; the article describes the target as harmless.T1547.001 · Registry Run Keys / Startup FolderCursor wrote a script to the startup folder. Sophos could not confirm what the script did, and the observed action was attributed to a coding agent.T1555.003 · Credentials from Web BrowsersClaude Code's GStack /browse skill used PowerShell and DPAPI to decrypt saved browser credential data; Sophos described this as likely browser automation in the observed context.T1555.004 · Windows Credential ManagerClaude Code ran cmdkey /list to enumerate credentials held by Windows Credential Manager.
Vendors
Products
Claude CodeSophos found that AI coding agents like Claude Code, Cursor, and OpenAI Codex are triggering endpoint detections because their normal actions resemble attacker behavior, including credential access, downloads, andCursorSophos found that AI coding agents like Claude Code, Cursor, and OpenAI Codex are triggering endpoint detections because their normal actions resemble attacker behavior, including credential access, downloads, andOpenAI CodexSophos found that AI coding agents like Claude Code, Cursor, and OpenAI Codex are triggering endpoint detections because their normal actions resemble attacker behavior, including credential access, downloads, andWindows Credential ManagerThe report shows that defenders need to distinguish between harmless automation and risky actions, especially around browser credentials and Windows Credential Manager.