
Injective Labs SDK Compromise Spreads Wallet-Stealing npm Packages
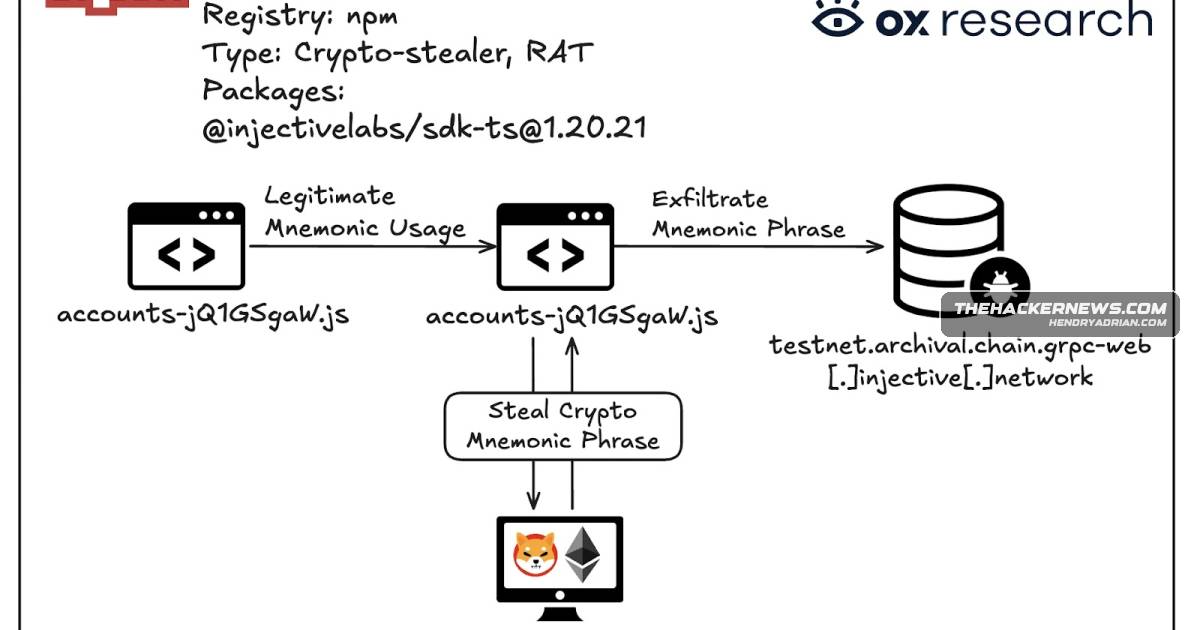
Summary
Reports say attackers compromised Injective Labs’ SDK repository and published malicious versions across 18 npm packages to steal wallet keys and seed phrases. Users are advised to upgrade to 1.20.23 and rotate exposed credentials.
Key points
- The Injective Labs SDK GitHub repository was reportedly compromised by unknown threat actors.
- Malicious version @injectivelabs/[email protected] was published on July 8, 2026; the article says it has since been deprecated, though its GitHub release artifacts remained available.
- The malicious version was also published across 17 related @injectivelabs packages, exposing users through transitive dependencies.
- Socket reported that fake telemetry in trackKeyDerivation() collected private-key generation data and mnemonic phrases.
- The malware queued captured data and sent it in an HTTPS POST to testnet[.]archival[.]chain[.]grpc-web[.]injective[.]network.
- StepSecurity said the release used the repository’s trusted-publisher OIDC pipeline and commits were pushed under a trusted maintainer’s identity.
- Users are advised to upgrade to clean version 1.20.23, check transitive dependencies, and rotate any wallet keys or mnemonic phrases passed through affected packages.
Article Details
- Victim Organization
- Injective Labs
- Incident Type
- Software supply-chain compromise involving malicious npm packages that exfiltrated cryptocurrency wallet private keys and mnemonic seed phrases.
- Incident Date
- 2026-07-08
- Data Types Exposed
- Cryptocurrency wallet private keys
- Mnemonic seed phrases
- Affected Records
- Unknown
- Affected Data Size
- Unknown
- Operational Impact
- The compromised package could expose wallet credentials when its key-generation or mnemonic-reading functionality was used. The source does not confirm how many users were affected or whether credentials were successfully exfiltrated.
- Ransom Or Extortion
- None reported
- Claim Status
- confirmed
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | testnet[.]archival[.]chain[.]grpc-web[.]injective[.]network | External server identified by the article as the destination for wallet key and mnemonic data exfiltrated by the malicious package. |
Products
@injectivelabs/sdk-tsUnknown threat actors compromised the Injective Labs SDK GitHub repository and published a malicious npm package, @injectivelabs/[email protected], to steal cryptocurrency wallet private keys and mnemonic seed phrases.GitHubUnknown threat actors compromised the Injective Labs SDK GitHub repository and published a malicious npm package, @injectivelabs/[email protected], to steal cryptocurrency wallet private keys and mnemonic seed phrases.npmUnknown threat actors compromised the Injective Labs SDK GitHub repository and published a malicious npm package, @injectivelabs/[email protected], to steal cryptocurrency wallet private keys and mnemonic seed phrases.