
StepSecurity Adds Inventory of AI Agent Skills on Developer Machines and GitHub
Summary
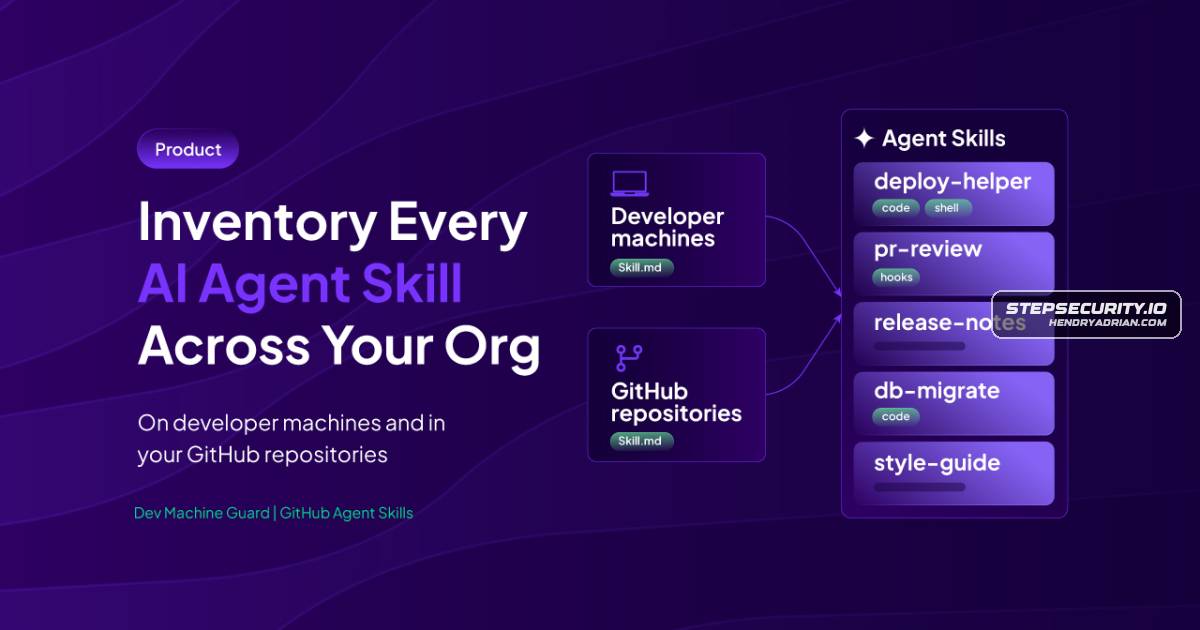
StepSecurity introduced inventories of AI agent skills on developer machines and in GitHub repositories, showing execution-related flags, sources and content differences to help teams review skills that may run code or hooks.
Key points
- Dev Machine Guard inventories skills in supported locations on developer devices, including shared, agent-specific and project folders, plugins and the skills.sh lock file.
- The device inventory shows skill scope, source, executable-content flags, content hashes, available Claude Code usage counts and device counts.
- A new GitHub inventory scans the default branch of each non-archived GitHub.com repository daily; GitHub Enterprise Server is not supported.
- Repository details include skill paths, agent and package information, source, files and scripts, declared behavior and skills.sh provenance.
- StepSecurity recommends reviewing skills flagged for shell execution, hooks or code, checking pre-approved tools and origins, and comparing differing or unmanaged copies.
- The article says skills may bundle scripts or hooks that run with developer privileges, making them a potential supply-chain risk.
Article Details
- Event Type
- Product capability launch
- Impact
- StepSecurity added inventory views for AI agent skills detected on developer machines and committed to organizational GitHub repositories. The views surface executable content, hooks, content variation, and skill provenance to help security teams review skills that could execute with developer privileges or spread through repositories.
Malware
Vendors
GitHubthe skills detected in supported locations on your developer machines, and a new Agent Skills page under GitHub shows the skills committed to your organization's repositories on GitHub.com. Together, they answer twoStepSecurityStepSecurity now gives security teams an inventory of both. Dev Machine Guard shows the skills detected in supported locations on your developer machines, and a new Agent Skills page under GitHub shows the skills
Products
Claude Codeplus optional scripts and resources, that an AI coding agent loads to gain a specialized capability. Claude Code, Codex, GitHub Copilot, Cursor, Gemini CLI, Windsurf, and many other agents load them.Codexscripts and resources, that an AI coding agent loads to gain a specialized capability. Claude Code, Codex, GitHub Copilot, Cursor, Gemini CLI, Windsurf, and many other agents load them.Cursorthat an AI coding agent loads to gain a specialized capability. Claude Code, Codex, GitHub Copilot, Cursor, Gemini CLI, Windsurf, and many other agents load them.Dev Machine GuardStepSecurity now gives security teams an inventory of both. Dev Machine Guard shows the skills detected in supported locations on your developer machines, and a new Agent Skills page under GitHub shows the skillsGemini CLIan AI coding agent loads to gain a specialized capability. Claude Code, Codex, GitHub Copilot, Cursor, Gemini CLI, Windsurf, and many other agents load them.GitHub Copilotand resources, that an AI coding agent loads to gain a specialized capability. Claude Code, Codex, GitHub Copilot, Cursor, Gemini CLI, Windsurf, and many other agents load them.Windsurfagent loads to gain a specialized capability. Claude Code, Codex, GitHub Copilot, Cursor, Gemini CLI, Windsurf, and many other agents load them.