
HEXACON2024 Talk Demonstrates Cross-CPU Allocation Exploits Against Linux Kernel Vulnerabilities
· 37:29 · Watch on YouTube ↗
Summary
The talk details cross-CPU allocation exploits for Linux kernel vulnerabilities in nf_tables and Traffic Control, including CVE-2023-31248 and CVE-2024-36978, and demonstrates privilege escalation despite allocator mitigations.
Key points
- The presenters describe two Linux kernel vulnerabilities explored in KernelCTF: an nf_tables use-after-free and a Traffic Control flaw.
- The nf_tables flaw occurs because lookup by chain ID can return a deactivated chain, enabling a use-after-free.
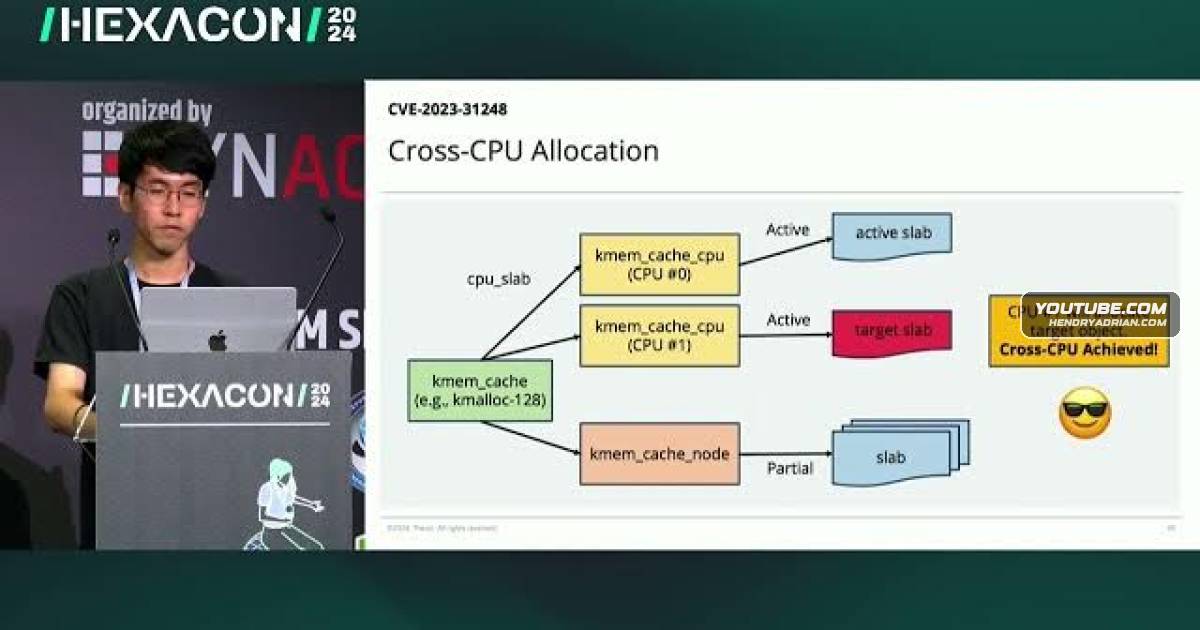
- Cross-CPU allocation lets the exploit reallocate a freed object on another CPU, supporting the nf_tables exploit despite a cross-cache mitigation.
- The presenters report obtaining root on Ubuntu 22.10 with the nf_tables exploit.
- For CVE-2024-36978, mismatched Traffic Control queue-band values lead to an out-of-bounds write that the talk demonstrates exploiting.
- The second exploit uses allocator behavior and race conditions to bypass mitigations in the KernelCTF environment.
Article Details
- Topics
- [00:37] Two Linux kernel vulnerabilities and cross-CPU allocation
- [02:07] nf_tables lookup flaw causing a use-after-free
- [09:05] Slab allocator behavior and cross-CPU object reallocation
- [13:16] nf_tables exploit sequence, information leaks, and root access
- [21:46] CVE-2024-36978 in the Traffic Control subsystem
- [23:09] Kernel allocator mitigations and techniques used to bypass them