
Krybit Claims Euroins Insurance Company AD as a Ransomware Victim
Summary
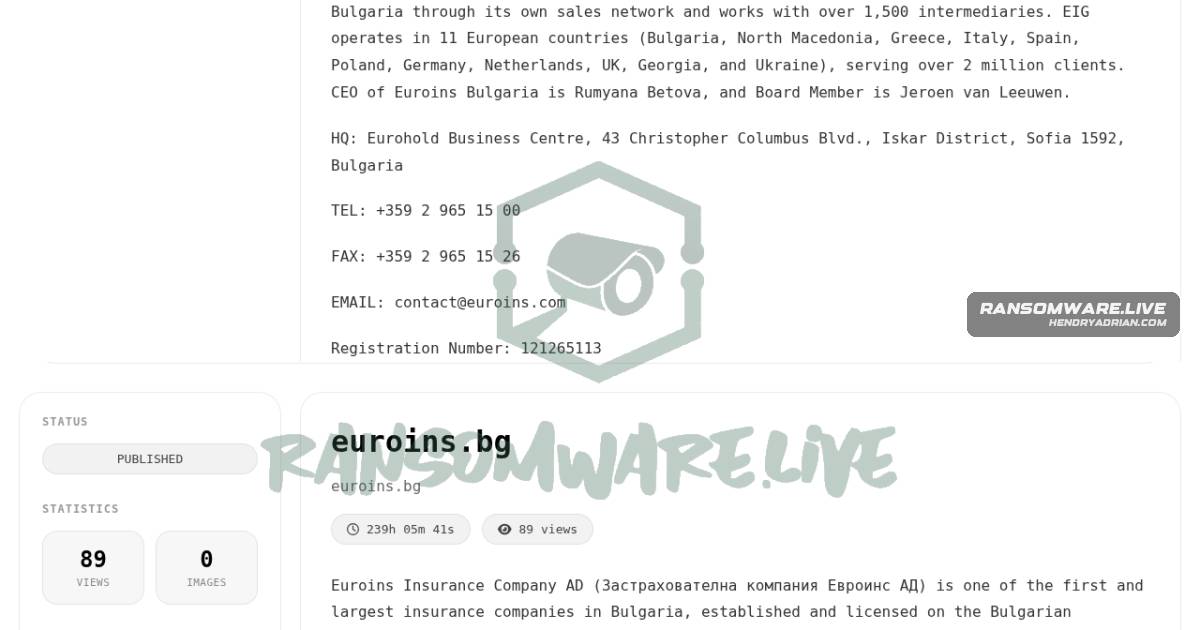
Ransomware.live lists Euroins Insurance Company AD in Bulgaria as a Krybit ransomware claim, citing the group’s leak site. The post’s claims of disruption, encryption and extortion are unconfirmed.
Key points
- The monitoring post names Euroins Insurance Company AD in Bulgaria as the victim and Krybit as the ransomware actor.
- It attributes the claim to a post on Krybit’s leak site and says ransomware.live monitored it.
- The post lists discovery and publication timestamps of July 18, 2026.
- Disruption consistent with encrypted systems and extortion demands are claims in the post; the author says they could not confirm the information.
Article Details
- Victim
- Euroins Insurance Company AD
- Victim Domain
- euroins.bg
- Claim Date
- 2026-07-18
- Encryption Status
- Unverified; the post describes disruption consistent with encrypted systems based on the ransomware group's claim.
- Exfiltration Status
- Unknown
- Ransom Demand
- The post says the group made extortion demands, but gives no amount; the claim is unverified.
- Leak Status
- The group claim is linked to its blog; publication or leakage of victim data is not reported.