

Ransomware Group Thegentlemen Claims Metalware Corporation as a Victim
Thegentlemen claims it targeted Montreal-based manufacturer Metalware Corporation. The post says the claim is unconfirmed.
Thegentlemen claims it targeted Montreal-based manufacturer Metalware Corporation. The post says the claim is unconfirmed.
A ransomware.live post records Qilin’s claim that it targeted XICO in Mexico and encrypted data. The publisher says the claim is unverified.
Ransomhouse claimed a ransomware attack on Lima’s Hospital Hermilio Valdizán, with services reportedly disrupted. The post says the claim is unconfirmed and cites the group’s onion site: hxxp://zohlm7ahjwegcedoz7lrdrti7bvpofymcayotp744qhx6gjmxbuo2yid[.]onion/r/cd414b5bf
A ransomware.live monitoring post records netrunner’s claim that Main Place Mall in Malaysia was targeted. The post says the claim has not been independently confirmed.
Incransom claims it stole customer, financial, utility, and OT security data from Sangre de Cristo Electric Association. The monitoring post says the claims are unverified and negotiations reportedly ended.
Ransomware.live records an unverified krybit claim targeting French managed services provider EURODITEL/RESOTELECOM, published and discovered on October 1, 2026.
A ransomware group called ransomhouse claims it attacked Brazilian logistics operator Terca, disrupting some operations. The monitoring post says the claim is unverified and has not been confirmed by Terca.
Booba Project claims it stole 70 GB of medical data from Associated Gastroenterologists of Central New York. The report, monitored by ransomware[.]live, says the claim is unverified.
The Booba Project claimed it targeted Brazil’s FUNAP and stole 26 GB of data. The monitoring post says the claim is unverified.
A ransomware.live monitoring post records Krybit’s claim against DISK PRECISION GROUP (diskprecision[.]com), alleging operational disruption. The post says the claim is unverified.
Ransomware.live reports an unverified AuditTeam claim targeting Italian IT firm ProMind IT. The post says the company’s website is offline; the group’s claims have not been confirmed.
AuditTeam claimed it targeted Italian medical device maker Steelco and affected its operations in Italy. The claim is based on public group claims and has not been confirmed.
A public claim attributed to the Genesis ransomware actor says it targeted US healthcare provider TLC Perinatal. The report says operations were disrupted, but notes the claim is unconfirmed.
Genesis claimed an attack on VPNE. The post says the claim is based on public statements by the ransomware group and has not been independently confirmed.
Ransomware group chaos claims Park Dental has not responded to its demands and threatens to release allegedly stolen data. The monitoring post says the claims are unverified.
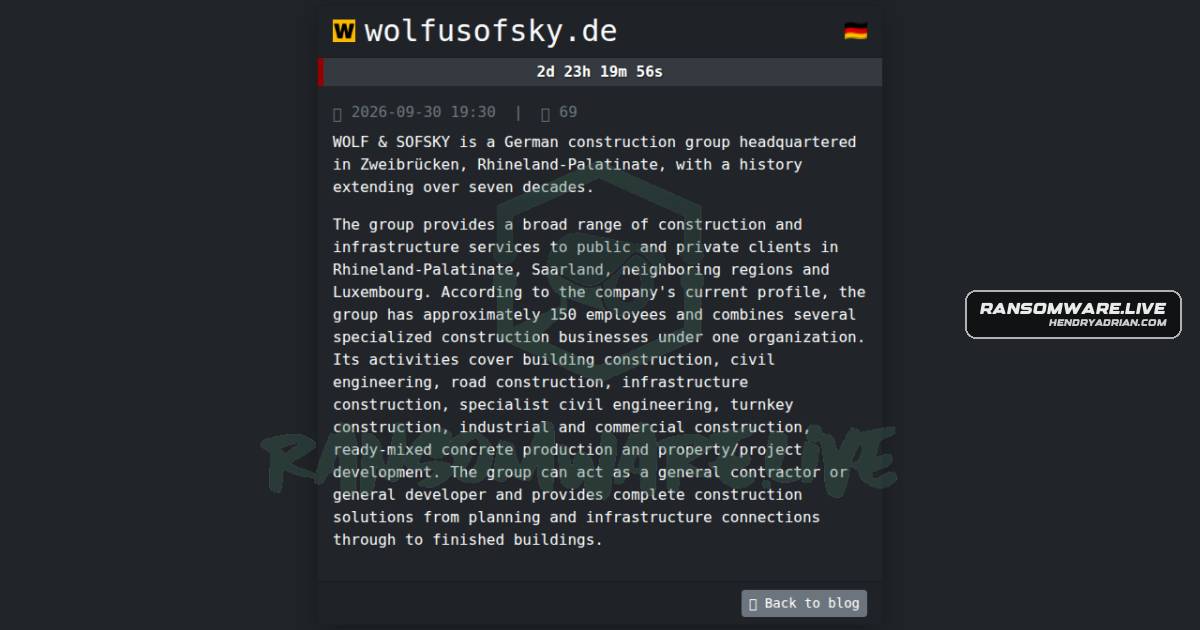
Ransomware.live recorded an unverified Safepay claim targeting wolfusofsky[.]de in Germany, with the claim published and discovered on September 30, 2026.
A ransomware.live monitoring post says Vexy Ransomware allegedly targeted Summit Electric Supply; the claim and reported operational disruption are unconfirmed.
A ransomware.live record says Eclipse claimed an attack on The Japan Times, allegedly disrupting services and subscriptions. The claim is unverified.
Ransomware group pear claimed Software Answers, a US-based accommodation software provider, as a victim. The monitoring post says the claim is unverified.
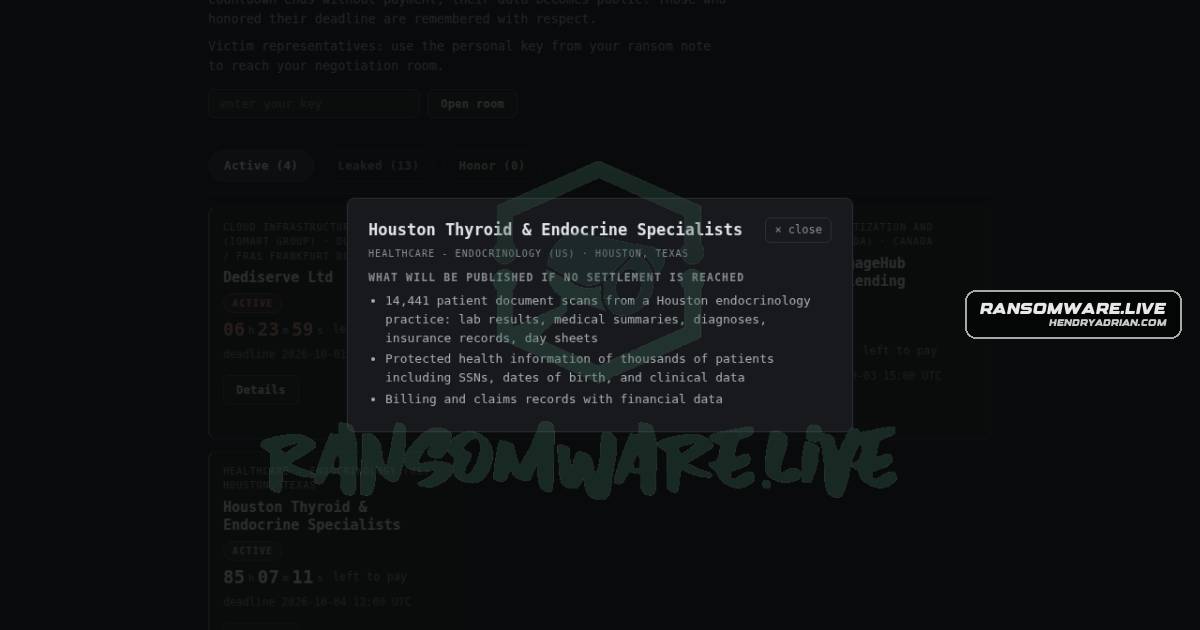
Ransomware group N0n claims it stole 14,441 patient document scans and other sensitive records from Houston Thyroid & Endocrine Specialists. The monitoring post says the claims are unverified.
A ransomware.live monitoring post says the Play group claimed to target German manufacturer Orth Automobile. The post says the claim could not be independently confirmed.
The Play ransomware group claimed Airtech Mechanical Services in the United States was affected by an attack. The monitoring post says the claim has not been independently confirmed.
A ransomware.live monitoring post records Play’s claim that it targeted German technology firm Titus. The claim is unverified, and the post says it cannot confirm the information.
Ransomware group settra claims it has 27 years of DFI Retail Group email archives, records on 397 stores, and 40,000 medical files. The monitoring post says the claims are unverified.