

DragonForce Claims Ransomware Attack on Homewood Sales
Ransomware.live listed Homewood Sales as a DragonForce ransomware victim, citing a group post published September 4, 2026. The claim is unverified, and the company’s response is not provided.
Ransomware.live listed Homewood Sales as a DragonForce ransomware victim, citing a group post published September 4, 2026. The claim is unverified, and the company’s response is not provided.

DragonForce allegedly leaked more than 340 GB of RubberMill data, including credentials, email archives, SSNs, payment records and engineering files. The post says the group’s claims could not be confirmed.
A ransomware.live record says the Chaos group claimed to target Evergenbio.com, a US healthcare-sector company. The claim is unverified; no specific data theft, encryption, or operational impact is confirmed.

A ransomware.live monitoring post records Vexy Ransomware’s claim naming Sancity as a victim, published and discovered on September 6, 2026. The post says the claim is unverified.
Ransomware group Panzer reportedly claimed an attack affecting Edacentrum, a Swedish electronics, design and applications network. The claim was listed on September 6, 2026, and has not been independently confirmed.
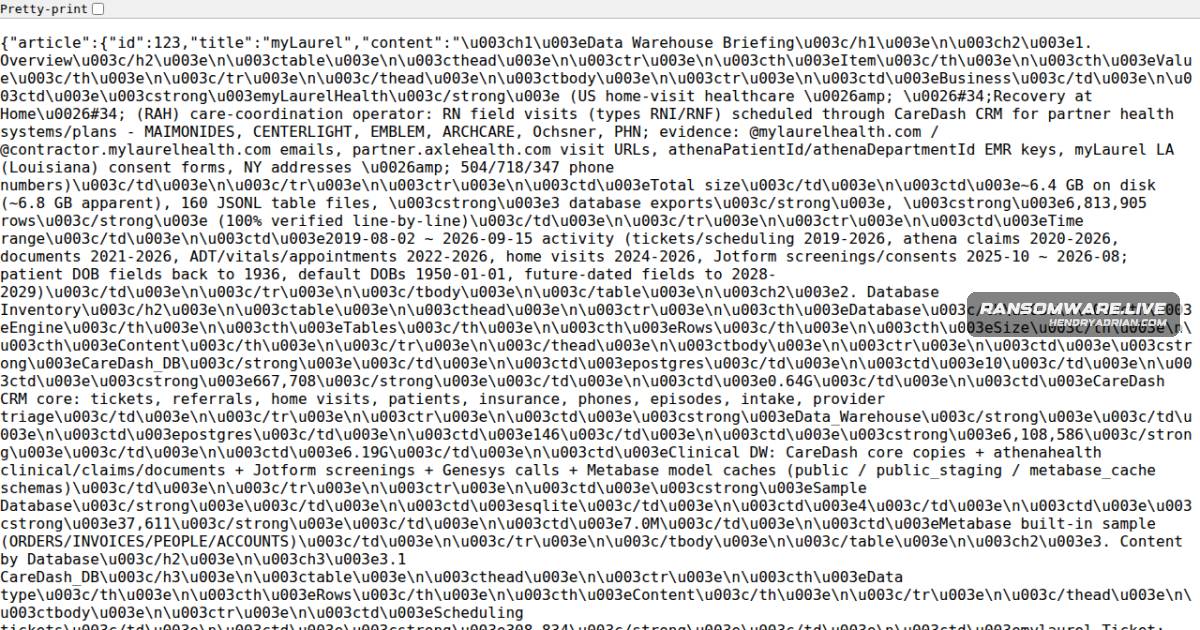
Ransomware.live reports that the direwolf group allegedly targeted US elderly care provider myLaurel, encrypted critical files and demanded a ransom. The claim is unverified.
A ransomware.live post reports Panzer’s claim of an incident affecting Saudi Arabia’s KHALED ALFAGIH ENGINEERING CONSULTANCY, with operations reportedly disrupted. The post says the claim could not be confirmed.
A ransomware.live record says Qilin claimed an attack on US-based Nolan Consulting Group, a professional services organization. The claim was published September 5, 2026, and the record says it could not be confirmed.
A ransomware.live monitoring post records Qilin's claim targeting US-based G&S Technologies, published September 5, 2026. The post says the claim has not been independently confirmed.
A ransomware group identified as Qilin claimed an attack on French manufacturer Jouvet SAS, alleging data encryption and operational disruption. The report says the claim could not be independently confirmed.
A ransomware.live listing attributes to DYSPHOR1A an unverified claim that 30 GB of CitizensPay agent information was compromised, with a reported ransom demand of $7,000–$25,000.
A ransomware monitoring post attributes an incident affecting Brazilian aviation company Lider Aviacao to thegentlemen. The post says the claim is unverified and provides no independent confirmation.
A ransomware.live post says the group kazu claimed to target Spirit Cultural Exchange, a U.S. provider of cultural exchange and J-1 visa programs. The post says the claim could not be confirmed.

A ransomware group called direwolf claims it targeted US healthcare organization Mission Pet Health. The report attributes operational disruption and data compromise to the incident but says the claims are unconfirmed.
Thegentlemen allegedly exposed more than 3.5 million Veradigm patient records, including sensitive patient and guarantor information. The claim is unconfirmed, according to the report.
A ransomware.live monitoring post attributes a claim of operational disruption at Polish pharmacy chain Zdrowit to thegentlemen. The post says the claim is unconfirmed.
A ransomware.live monitoring post attributes a ransomware claim against Leo Schachter Diamonds to thegentlemen. The post lists September 2 and 5, 2026 dates but says the claim has not been verified.
A ransomware claim says Vexy Ransomware targeted Mega Velocity, a technology company. The claim was published on September 5, 2026; its accuracy has not been confirmed.
Ransomware.live reports that Qilin claims to have encrypted files at Bauman Law Group and demanded payment. The claim was published on September 5, 2026, and has not been independently confirmed.
Ransomware.live reports that Qilin claimed to target the Philippine Ports Authority and encrypt systems, allegedly disrupting operations. The post says the claim has not been independently confirmed.
A ransomware claim attributed to pear names US healthcare company Kovo Healthtech Corp and alleges disruption to its systems. The report says the claim’s accuracy could not be confirmed.
Ransomware.live reports that the pear ransomware group listed EdgeChem Jamaica Limited, a Jamaican coatings manufacturer, as a victim. The claim was discovered September 5, 2026, and has not been independently confirmed.
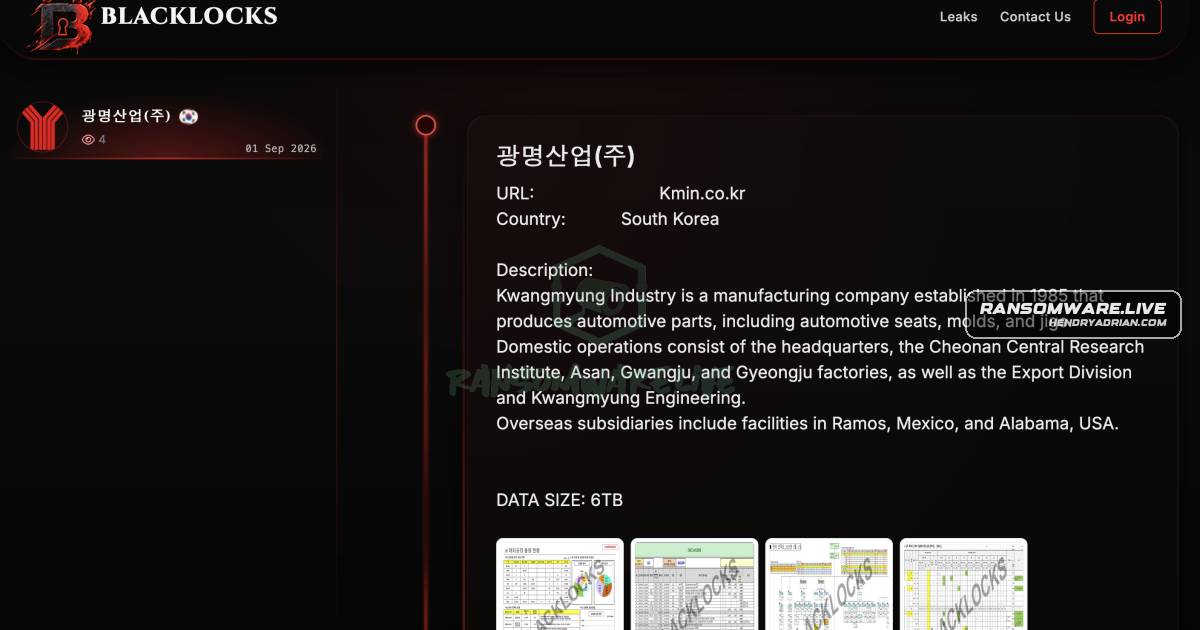
BlackLocks claimed to have targeted South Korean manufacturer Kwangmyung Industry, alleging impacts to domestic operations and facilities in Mexico and the United States. The post says the claims are unverified.
The ransomware group emperador claims it accessed the Jujuy Judicial Branch’s WordPress databases and credentials, citing 4.2 GB of data and demanding a ransom. The claim has not been confirmed.