cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · thehackernews.com

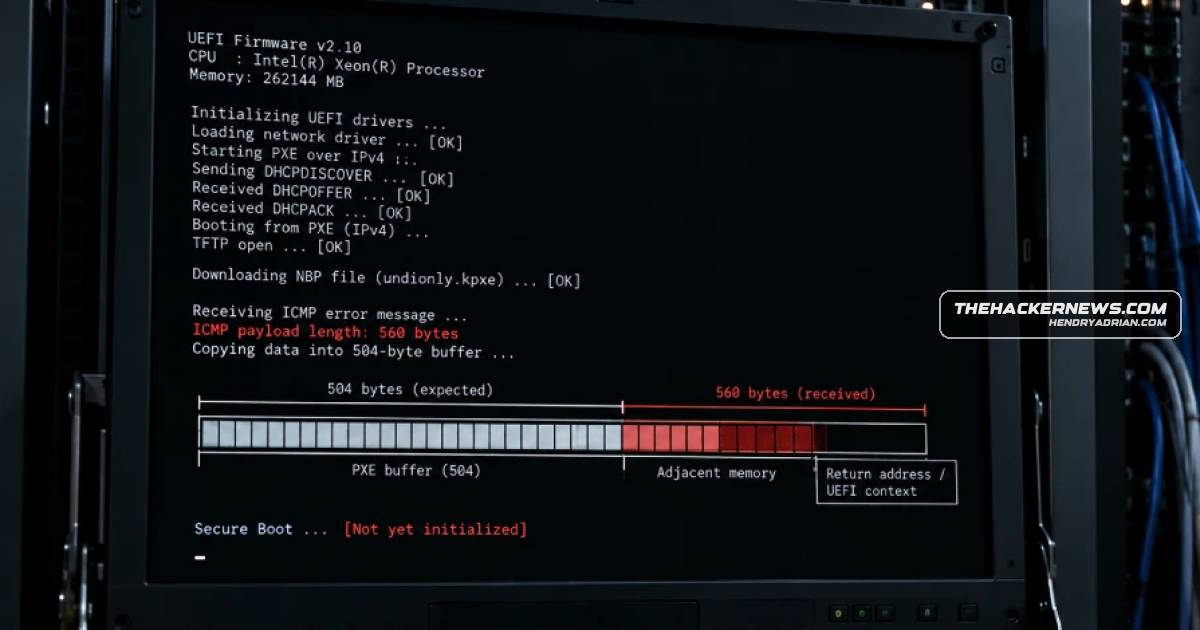
EDK II PXE Flaw Could Enable Pre-Secure Boot Code Execution

CVE-2026-97631 is a buffer overflow in EDK II PXE network-boot code that can crash or, with build-specific exploitation, run code before Secure Boot. A fix is merged but not yet in a stable release; no exploitation is known.
Oct 28, 2026
Vulnerability & Exploit · thehackernews.com

Adobe Patches Eight Campaign Classic Flaws and Critical Connect Code-Injection Bug

Adobe patched eight critical flaws in Campaign Classic that could enable code execution, security-feature bypass or privilege escalation, plus CVE-2026-48360, a CVSS 9.6 code-injection flaw in Connect. Adobe reports no known in-the-wild exploitation.

Oct 28, 2026
Vulnerability & Exploit · securityweek.com

Four EPICS Base Flaws Patched, Including One That Could Enable Code Execution

CISA disclosed four unauthenticated network-triggerable flaws in EPICS Base 7.0.10 and earlier, including one that could potentially enable remote code execution. EPICS 7.0.11 patches the issues; no public exploitation has been reported.

Oct 28, 2026
Vulnerability & Exploit · securityweek.com

Defused Reports Probing of Patched Oracle EBS Vulnerability

Defused says its decoys recorded exploratory attempts against Oracle EBS flaw CVE-2026-101767 on October 27. Oracle patched the critical remote SQL injection in its October CPU; no other in-the-wild exploitation reports are cited.

Oct 28, 2026
Vulnerability & Exploit · securityweek.com

CISA Adds Node2Shell Brotli Flaw to KEV as Honeypots Record Exploitation Attempts

CISA added the Node2Shell Brotli flaw (CVE-2026-111497) to its KEV catalog. Honeypots recorded attempts, but ELLIO found its observed exploit failed; patches are pending for affected VMware products.

Oct 28, 2026
Vulnerability & Exploit · thehackernews.com

Tailscale 1.104.4 Fixes SSH Forwarding Flaws That Could Enable Root Access

Tailscale 1.104.4 fixes SSH forwarding flaws that could let an attacker on a policy-authorized device reach root-only sockets. Users should update or temporarily disable forwarding; no real-world exploitation is reported.

Oct 28, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds PolyShell and Brotli Flaws to KEV Amid Exploitation Reports

CISA added Adobe Commerce/Magento’s PolyShell flaw and Brotli-related CVE-2026-111497 to its KEV catalog. Reports describe ongoing PolyShell attacks and Brotli exploit traffic; vendors issued fixes, with FCEB agencies’ deadline set for November 10.

Oct 28, 2026
Vulnerability & Exploit · cyber.gc.ca

Cyber Centre Warns of Critical Google Brotli Vulnerability CVE-2026-111497

The Canadian Cyber Centre warns that CVE-2026-111497, a remotely exploitable out-of-bounds write in the Google Brotli decoder, could cause memory corruption, information disclosure, crashes or code execution. CISA added it to its KEV database.

Oct 28, 2026
Vulnerability & Exploit · sophos.com

Node2Shell Brotli Vulnerability CVE-2026-111497 Reported in Active Exploitation

CVE-2026-111497, a critical buffer overflow in the Brotli decoder, could enable memory disclosure, denial of service, or remote code execution. Active exploitation has been reported, and CISA added it to its KEV Catalog.

Oct 28, 2026
Vulnerability & Exploit · fieldeffect.com

Brotli Flaw Reaches File-Processing Workflows, Expanding Exposure

Research on CVE-2026-111497 expands the affected-product list and shows Brotli can be reached through JPEG XL/FFmpeg file processing, with demonstrated memory corruption and instruction-pointer control. A reported Node.js exploitation attempt remains unconfirmed.

Oct 28, 2026
Vulnerability & Exploit · zscaler.com

CVE-2026-111497 Brotli Flaw May Enable RCE Across Node.js and Other Software

CVE-2026-111497 is an out-of-bounds write in the Brotli decoder that may allow crashes, memory disclosure or RCE when vulnerable software decompresses attacker-controlled data. Zscaler reports reconnaissance and exploitation attempts.

Oct 28, 2026
Vulnerability & Exploit · bleepingcomputer.com

Threat Actors Scan for Recently Patched Oracle E-Business Suite Flaw

Defused reported exploratory exploit attempts against Oracle E-Business Suite CVE-2026-101767, an unauthenticated flaw that can lead to remote code execution. Oracle released patches on October 20; exploitation in the wild is not confirmed.

Oct 28, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Warns of Active Exploitation of Critical Brotli Node2Shell Flaw

CISA says attackers are exploiting CVE-2026-111497, a critical Brotli decoder flaw that can cause crashes, memory disclosure, denial of service, or potentially remote code execution. It urges prompt patching and lists mitigations.

Oct 28, 2026
Vulnerability & Exploit · securityweek.com

Tailscale Prepares Patches for Tailworm Privilege-Escalation Flaws

A Cyberdione Labs report describes 11 Tailworm findings affecting Tailscale and headscale, including SSH flaws that researchers say enabled wormable privilege escalation in lab tests. Tailscale said fixes were pending release and advised reviewing SSH policies.

Oct 27, 2026
Vulnerability & Exploit · thehackernews.com

Apple Backports Fix for Exploited CoreGraphics Flaw to Older iPhones and iPads

Apple backported a fix for CVE-2026-86950, a CoreGraphics flaw it says may have been exploited in targeted attacks, to iOS 18.7.11 and iPadOS 18.7.11. The updates also fix other security issues.

Oct 27, 2026
Vulnerability & Exploit · thehackernews.com

GoAhead 6.1.1 Fixes TLS Flaws and Login Bypass in Embedded Web Server

GoAhead 6.1.1 fixes three backend-specific TLS flaws and a login bypass. No exploitation had been reported as of Oct. 27, 2026; the affected device population and manufacturer firmware rollouts remain unknown.

Oct 27, 2026
Vulnerability & Exploit · securityweek.com

HPE Patches 72 Aruba Networking Flaws, Including Eight Critical Bugs

HPE patched 72 vulnerabilities in Aruba AOS-8 and AOS-10, including eight max-severity flaws that could enable remote code execution or administrative access. HPE says it has no evidence of exploitation and urges customers to patch.

Oct 27, 2026
Vulnerability & Exploit · thehackernews.com

Microsoft Fixes Android Authenticator Flaw That Could Expose Work Account Tokens

CVE-2026-80097 let a permissionless Android app impersonate a trusted app to obtain Microsoft Authenticator work-account tokens. Microsoft says exploitation requires user interaction and has not occurred; update Authenticator to version 6.2606.4246 or later.

Oct 27, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Two Actively Exploited Vulnerabilities to KEV Catalog

CISA added CVE-2026-48356 in Adobe Commerce and Magento and CVE-2026-111497 in Google Brotli to its KEV Catalog based on evidence of active exploitation, urging organizations to prioritize remediation.

Oct 27, 2026
Vulnerability & Exploit · securityweek.com

CVE-2026-30612 Exposed Popcorn Time Users to Malicious Updates

Eye Security found that the abandoned Time4Popcorn updater downloaded and ran unsigned executables over HTTP. It sinkholed update domains and disabled the updater for about 2 million systems; Android users remain exposed, and the app should be uninstalled.

Oct 27, 2026
Vulnerability & Exploit · thehackernews.com

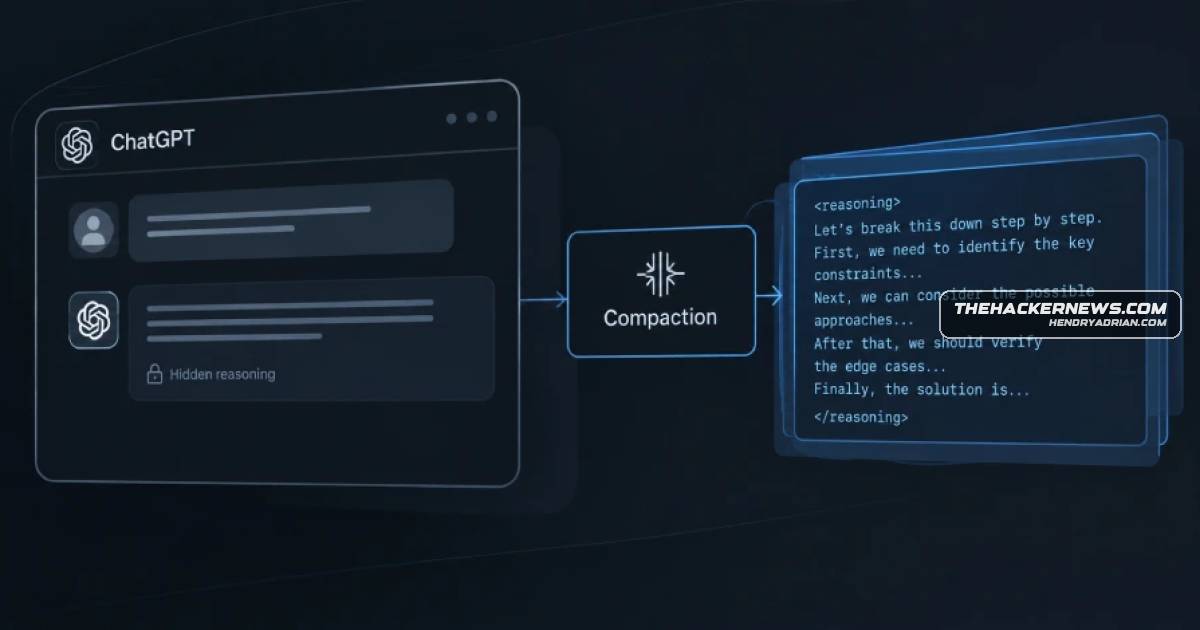
Xint Demonstrates OpenAI Compaction Flaw That Could Expose Hidden Reasoning

Xint says a compaction prompt could copy reasoning returned by OpenAI’s gpt-5.6-sol into an encrypted item, which cheaper models repeated as text. OpenAI fixed the issue Oct. 23; Xint could not verify the text was verbatim or whether it was exploited.

Oct 27, 2026
Vulnerability & Exploit · socradar.io

Critical Wasmtime Flaws Could Enable WebAssembly Sandbox Escapes

Two critical Cranelift flaws can let crafted Wasm modules escape Wasmtime’s sandbox: one affects all architectures, the other ARM64. No exploitation was reported; upgrade to fixed releases, with no workaround available.

Oct 27, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Actively Exploited PHP2Shell Flaws to KEV Catalog

CISA added the actively exploited PHP2Shell flaws to its KEV catalog. Patches are available for PHP 8.2–8.5; a separate Brotli decoder flaw, CVE-2026-111497, also affects PHP Windows builds and other software.

Oct 27, 2026
Vulnerability & Exploit · cyber.gc.ca

Canada Warns of Critical PHP Vulnerabilities CVE-2026-109618 and CVE-2026-109619

Canada’s Cyber Centre warns that two PHP use-after-free vulnerabilities could allow unauthenticated code execution. A PoC is reportedly available, but no active exploitation had been identified; organizations should update affected installations and prioritize internet-

Oct 27, 2026
PreviousPage 13 of 65 Next
© 2026 cyber.hendryadrian.com