cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3576 articles

Security News · crowdstrike.com

CrowdStrike Adds Supply-Chain and AI Workload Protections to Falcon Cloud Security

CrowdStrike says generally available Falcon Cloud Security updates add supply-chain scanning, expanded cloud-risk visibility, real-time detections across Azure and Kubernetes, AI anomaly detection, and protection for AI and specialized workloads.


Nov 4, 2026
Security News · crowdstrike.com

CrowdStrike Adds Seraphic Enterprise Browser Security to Falcon Platform

CrowdStrike says Falcon Seraphic Enterprise Browser is now available on the Falcon platform, with browser-session protections, data controls, extension management and access to private applications, including on unmanaged devices.

Nov 4, 2026
Security News · crowdstrike.com

CrowdStrike Announces Falcon Features to Detect and Respond to AI Agent Threats

CrowdStrike announced Falcon capabilities for detecting unusual AI agent behavior, investigating whether actions came from an agent or its user, and coordinating response and approval controls. Several features are listed for Q4; others are generally available or in bet

Nov 4, 2026
Security News · crowdstrike.com

CrowdStrike Announces AI-Powered Adversary Emulation and Threat Intelligence App

CrowdStrike announced early access to an AI-powered red-teaming capability that maps attack paths, recommends defenses and retests fixes, plus a mobile app for Falcon Adversary Intelligence Premium customers.

Nov 4, 2026
Security News · fieldeffect.com

Researchers Report Application Identity Abuse Targeting MSPs and Customers

Researchers report an active campaign using valid application credentials to access Microsoft Entra ID and Azure DevOps environments, with MSPs and their customers a primary focus. The credential source remains under investigation.

Nov 4, 2026
Security News · bleepingcomputer.com

US Indicts Two Canadians Accused of Hacking Universities for Crypto Mining

A federal grand jury indicted two Canadians over alleged malware infections, data and credential theft, and cryptocurrency mining on U.S. university networks. One was extradited; the other awaits extradition.

Nov 4, 2026
Security News · sysdig.com

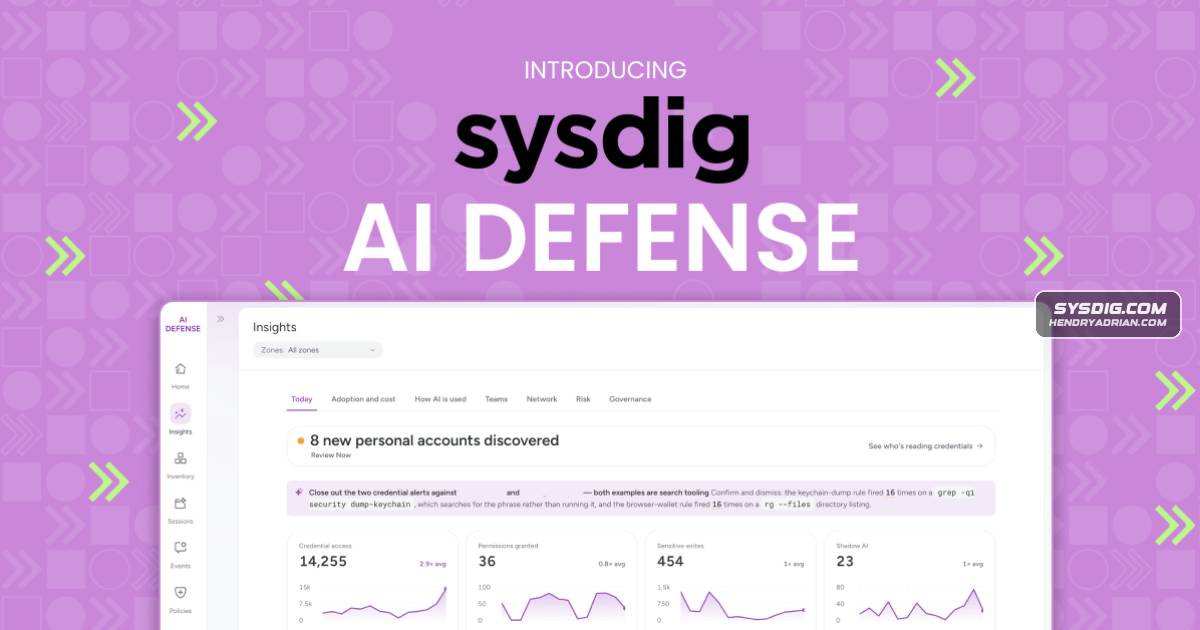
Sysdig Launches Runtime Security Product for AI Agents

Sysdig announced AI Defense, a runtime security product that inventories AI agents and can alert, block, request approval for, or terminate selected actions while keeping an off-device activity record.

Nov 4, 2026
Security News · darkreading.com

Yubico Opens YubiID Early Access and Post-Quantum YubiKey Beta

Yubico opened limited early access to YubiID, which links identity verification with credential enrollment and recovery across identity platforms. It also started a public beta for a post-quantum-ready YubiKey with non-upgradeable firmware.

Nov 4, 2026
Security News · darkreading.com

Google and Partners Disrupt XCPE Botnet Linked to 1.3 Million Android Devices

Google and partners disrupted the XCPE botnet, which Google attributes with high confidence to Videostrong and says backdoored more than 1.3 million Android devices. Google says broader C2 disruption could cut access to at least 10 million more devices.

Nov 4, 2026
Security News · bleepingcomputer.com

Sekoia Links Watering-Hole Campaign Using N-Day Exploits to APT29

Sekoia reports a watering-hole campaign using zero-click n-day exploit chains against iOS and Android, and attributes it with moderate-to-high confidence to APT29. The attacks profiled devices and targeted data; Apple and Google have patched the flaws.

Nov 4, 2026
Security News · databreachtoday.com

Sekoia Attributes Mobile Watering-Hole Campaign to Russia’s APT29

Sekoia attributes with moderate to high confidence a mobile watering-hole campaign to Russia’s APT29, which used compromised or look-alike sites and known vulnerabilities to steal browser cookies and other data.

Nov 4, 2026
Security News · cisecurity.org

CIS Announces November 2026 Updates to Security Benchmarks

CIS announced benchmark updates for Windows, Edge, Docker, Kubernetes, AWS, PostgreSQL and other platforms, alongside new benchmarks and build kits. Changes include revised recommendations, assessment content and support for newer platform versions.

Nov 3, 2026
Security News · thehackernews.com

Email Urges mSecure Users to Change Passwords After Suspicious Activity

An email sent in mSeven Software’s name urged current and former mSecure customers to change passwords and consider resetting 2FA and removing passkeys after unspecified suspicious activity. The company had not publicly confirmed it by Nov. 3, and exposure remains unpro

Nov 3, 2026
Security News · arstechnica.com

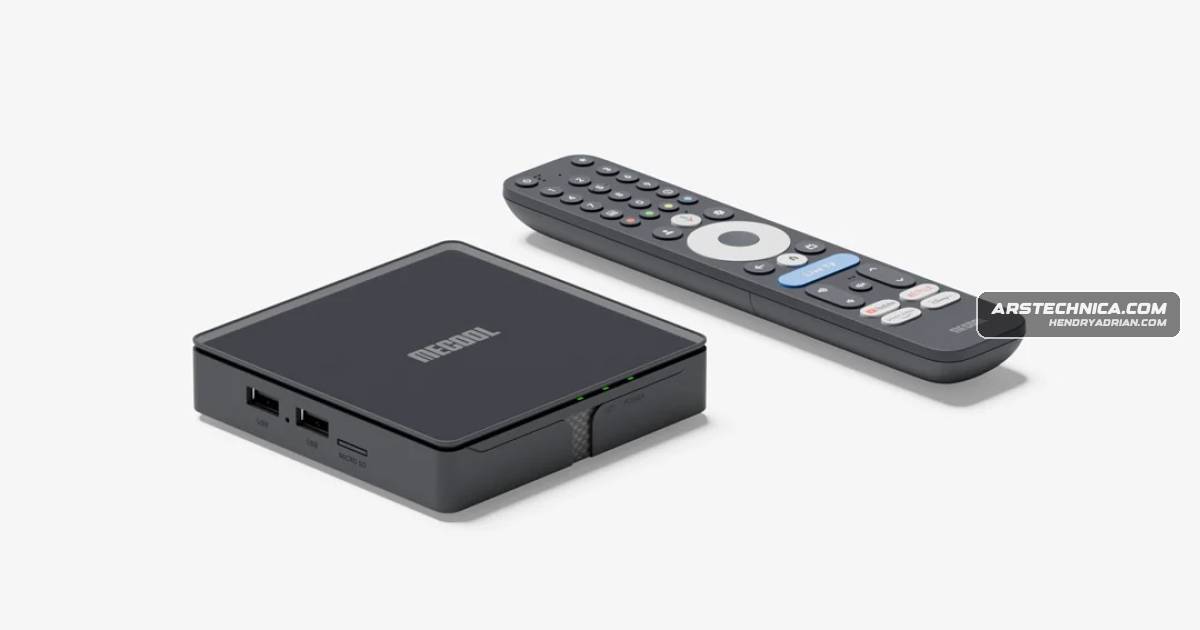
Google Disrupts x.cpe Botnet on More Than 1.3 Million Android TV Devices

Google says it disrupted the x.cpe botnet, which infected more than 1.3 million certified Android TV boxes, mainly sold as MECOOL devices. The malware enabled proxy and ad-fraud activity; Play Protect remains disabled on affected boxes.

Nov 3, 2026
Security News · microsoft.com

Microsoft Details Agent 365 Security and Governance Capabilities for AI Agents

Microsoft says Agent 365 provides identity, access controls, discovery, and governance for AI agents. The company describes integrations, planned discovery expansion, and an Action Center for automated governance actions.

Nov 3, 2026
Security News · blog.qualys.com

FedRAMP’s New Continuous-Monitoring Rules Become Mandatory December 7

CISA BOD 26-04 and FedRAMP’s upcoming VDR/VER requirements shift providers from monthly scans to continuous, risk-based validation. The rules become mandatory Dec. 7, 2026; Qualys promotes Policy Audit and Audit Fix for assessment and remediation.

Nov 3, 2026
Security News · thehackernews.com

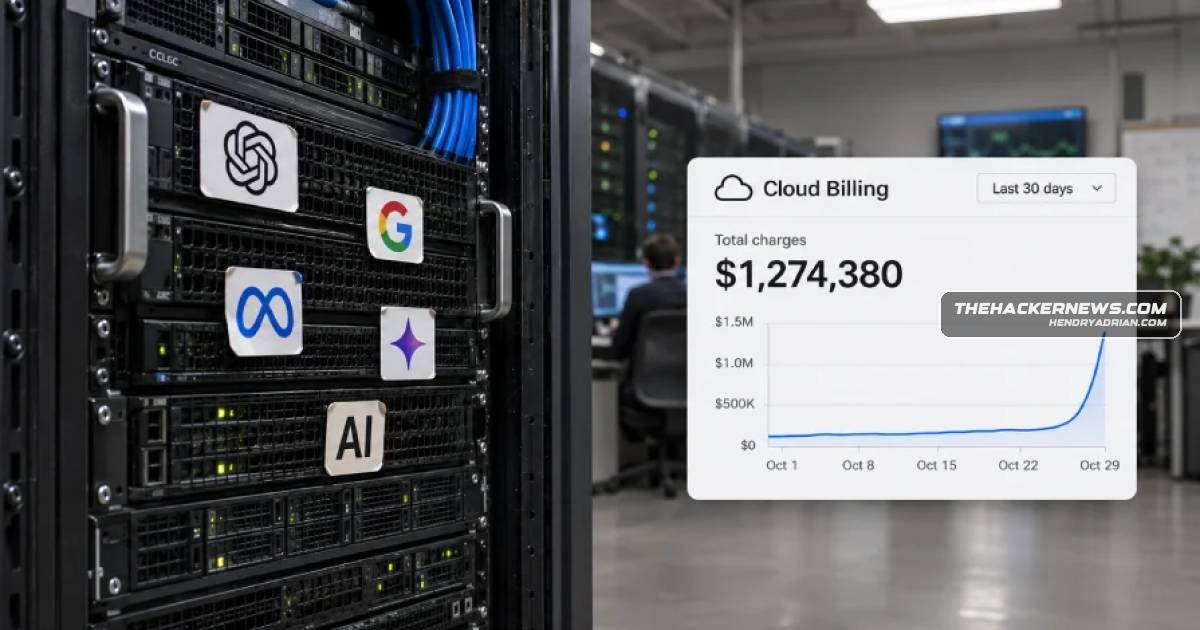
Google Warns LLMjacking Can Drive Enterprise Cloud Charges to $1 Million

Google reports LLMjacking incidents using exposed or stolen cloud and API credentials to misuse enterprise LLMs, with daily charges exceeding $100,000 and some bills reaching $1 million; illicit relays also resell access and reconfigure legitimate AI CLI tools.

Nov 3, 2026
Security News · securityweek.com

CrowdStrike to Acquire Fiddler AI and Dreadnode in Deals Reportedly Worth $495 Million

CrowdStrike agreed to acquire AI agent observability firm Fiddler AI and AI security testing company Dreadnode in deals reportedly worth $495 million. It also added an AI Kill Switch to Falcon Guardian.

Nov 3, 2026
Security News · malwarebytes.com

Google Says Videostrong Backdoor Put 1.3 Million Android TV Boxes in a Botnet

Google says Videostrong built the XCPE backdoor found in 1.3 million Android TV boxes and sold criminals access. A takedown disrupted the botnet, but the backdoor remains in infected devices’ firmware.

Nov 3, 2026
Security News · blog.cloudflare.com

Cloudflare Launches Zero Wire Vulnerability Intelligence Feed

Cloudflare announced Zero Wire, a public feed on Cloudflare Radar with briefings on critical internet-facing vulnerabilities, affected deployments, exploitation evidence, remediation guidance, and possible WAF mitigations.

Nov 3, 2026
Security News · cybersecuritypulse.net

Conference Recap Highlights AI Agent Attack Risks and Defenses

A [un]prompted conference recap details AI-agent attack demonstrations, reported agent-swarm outcomes and enterprise controls such as scoped identities, short-lived tokens, sandboxing and egress filtering.

Nov 3, 2026
Security News · wiz.io

Wiz Details Green Agent’s AI-Driven Cloud Remediation Workflow and Customer Results

Wiz says Green Agent links cloud risks to owners and source code, investigates exposure, and generates environment-specific fixes and pull requests. The article reports customer-reported improvements in triage time and remediation velocity.

Nov 3, 2026
Security News · securityweek.com

Google’s November 2026 Android Updates Patch More Than 200 Vulnerabilities

Google’s November 2026 Android updates fix more than 200 vulnerabilities, including critical flaws. The most severe, CVE-2026-58868, could enable remote code execution without user interaction.

Nov 3, 2026
Security News · malwarebytes.com

Leakers$ Claims Billboard Attacks Were “Far Too Easy”

Leakers$ claimed it accessed software used to manage digital billboards. Egyptian authorities said an operator’s website was compromised, leading to unauthorized footage in several countries; claims involving Iraq and China were less corroborated.

Nov 3, 2026
PreviousPage 5 of 149 Next
© 2026 cyber.hendryadrian.com