cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3801 articles

Security News · thecyberexpress.com

UK NCSC Urges Safeguards as AI-Generated Code Risks Scaling Vulnerabilities

At the RSA Conference, UK NCSC leaders warned that AI-generated code could replicate existing vulnerabilities and urged organizations to embed security principles, improve legacy systems, and consider safer frameworks and memory-safe languages.
Mar 25, 2026
Security News · thecyberexpress.com

Mario Kart Botnet Operator Sentenced to 61 Months for Selling Access to Ransomware Groups

A U.S. court sentenced Illya Angelov to 61 months for operating the Mario Kart botnet, which prosecutors said infected about 3,000 computers daily and sold backdoor access used by ransomware groups targeting 72 companies.

Mar 25, 2026
Security News · thecyberexpress.com

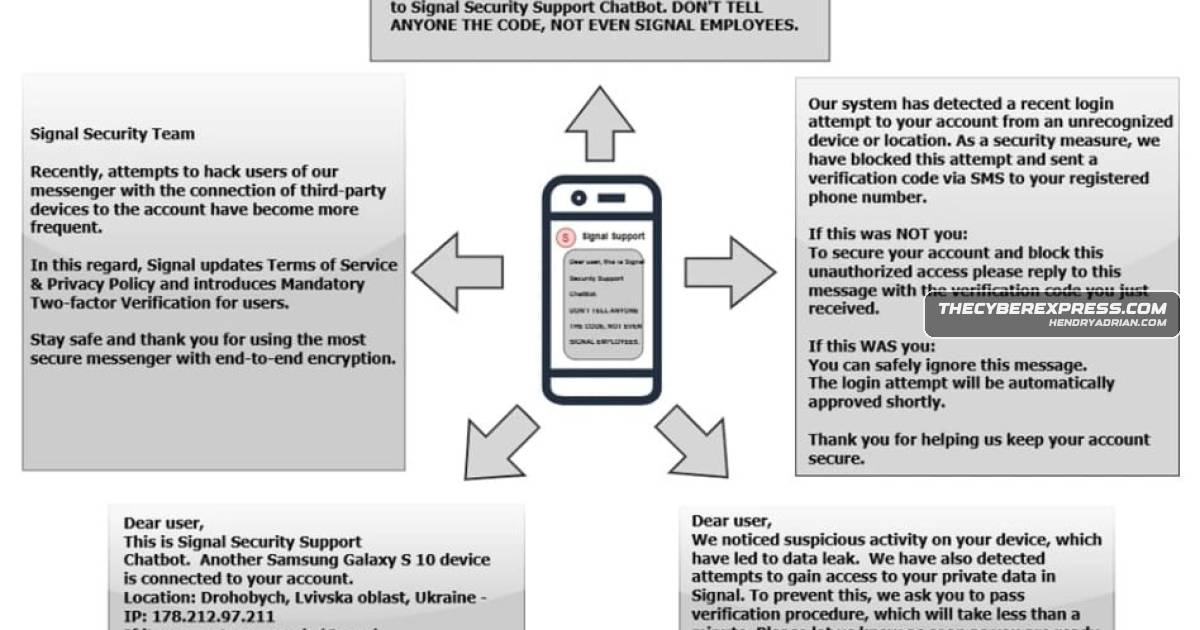
CISA and FBI Warn of Russian-Linked Phishing Targeting Messaging App Accounts

CISA and the FBI warn that actors linked to Russian Intelligence Services are using social engineering to take over commercial messaging app accounts. The agencies report thousands of compromised accounts and urge users to protect verification codes and scrutinize links

Mar 25, 2026
Security News · circleid.com

Researchers Trace DNS and WHOIS Artifacts Linked to HoneyMyte’s CoolClient

Researchers report HoneyMyte updated CoolClient in 2025 to deploy browser-login stealers and data-theft and reconnaissance scripts. DNS and WHOIS analysis refined its reported IoCs and found related domains and IPs; some flagged entities may be reclassified.

Mar 25, 2026
Security News · unit42.paloaltonetworks.com

Unit 42 Tracks Phishing Scam Impersonating Palo Alto Networks Recruiters

Unit 42 says it has tracked recruiter-impersonation phishing since August 2025, targeting senior professionals with personalized lures and fake ATS-compliance problems that pressure candidates to buy resume services. It advises verifying recruiters and never paying fees

Mar 25, 2026
Security News · thehackernews.com

TeamPCP-Linked Backdoors Found in LiteLLM PyPI Versions 1.82.7 and 1.82.8

LiteLLM versions 1.82.7 and 1.82.8 contained malware that harvested credentials, spread through Kubernetes clusters and installed a systemd backdoor. Researchers said the compromise likely involved Trivy CI/CD; both versions were removed from PyPI.

Mar 25, 2026
Security News · therecord.media

UK Cyber Agency Warns AI-Assisted Coding Could Increase Software Security Risks

The UK NCSC warned that AI-assisted “vibe coding” could spread insecure software as organizations build more bespoke tools. It urged secure-by-default code generation, model-integrity checks, and automated code review and testing.

Mar 25, 2026
Security News · bleepingcomputer.com

Paid AI Accounts Emerge as Underground Commodity

Flare's analysis of hundreds of posts in fraud-oriented online communities found recurring resale offers for premium AI accounts and API access. Suggested acquisition methods were not directly documented; the article recommends stronger account protections and activity

Mar 25, 2026
Security News · bleepingcomputer.com

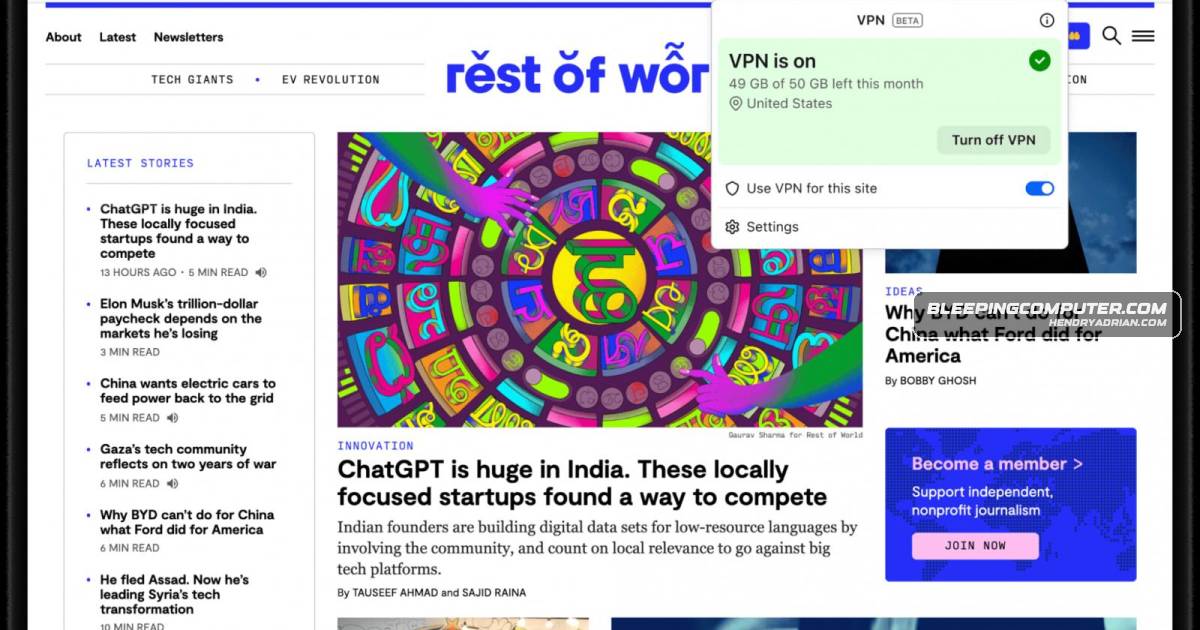
Firefox 149 Adds Browser-Only VPN and Fixes 46 Security Flaws

Firefox 149 adds a browser-only VPN with up to 50 GB of monthly traffic, blocks notifications from SafeBrowsing-flagged sites, and fixes 46 security vulnerabilities, more than half rated high severity.

Mar 24, 2026
Security News · bleepingcomputer.com

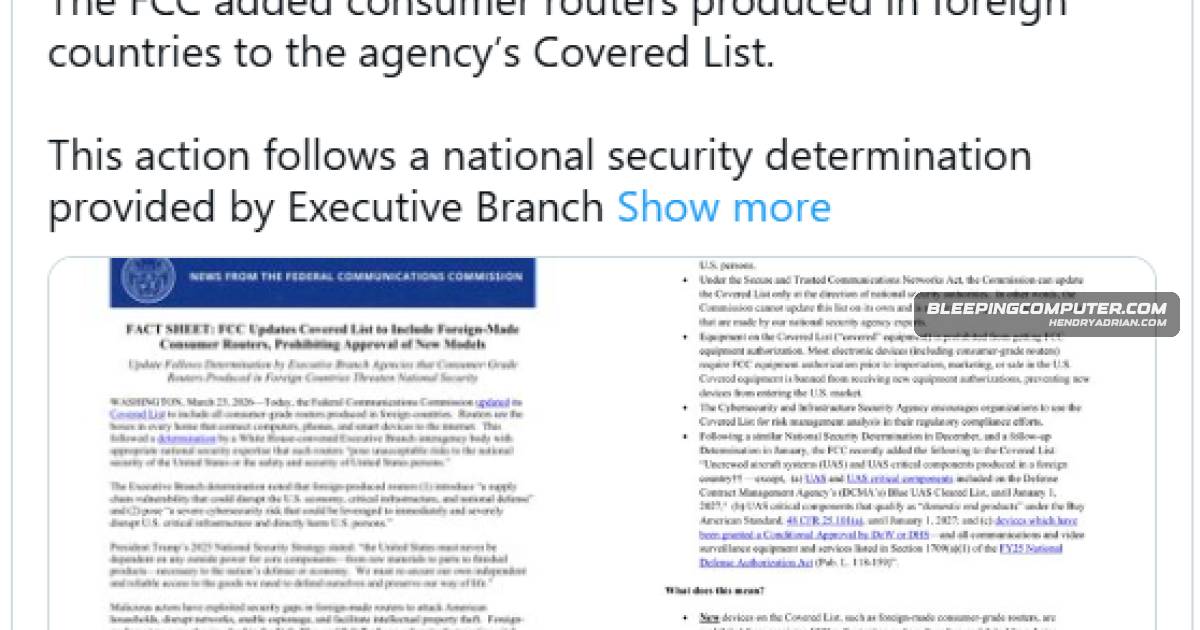
FCC Restricts Sales of New Foreign-Made Consumer Routers in U.S.

The FCC added foreign-made consumer routers to its Covered List, restricting sales of new models in the U.S. Conditional exemptions and an approval pathway apply; existing routers remain available, while consumers may face fewer models and higher prices.

Mar 24, 2026
Security News · securityweek.com

DOE Sets Five-Year Plan to Strengthen Energy Security

DOE’s CESER office published a 2026–2030 plan to develop security technologies, harden U.S. energy infrastructure, and improve emergency preparedness and recovery from natural disasters and cyberattacks.

Mar 24, 2026
Security News · cyberscoop.com

Huntress Reports AI-Assisted Phishing Campaign Compromised Hundreds of Microsoft Cloud Accounts

Huntress says a phishing campaign using Railway infrastructure obtained Microsoft OAuth tokens valid for up to 90 days and affected hundreds of organizations. Huntress blocked Railway domains for 60,000 tenants; Railway says it banned linked accounts and domains.

Mar 24, 2026
Security News · bleepingcomputer.com

Yanluowang Access Broker Sentenced to 81 Months in Prison

Aleksey Volkov pleaded guilty to selling corporate network access to Yanluowang affiliates and was sentenced to 81 months in prison. Investigators linked him to about $1.5 million in ransom proceeds; he must pay more than $9.16 million in restitution.

Mar 24, 2026
Security News · thecyberexpress.com

Russian Initial Access Broker Sentenced to 81 Months for Enabling Ransomware Attacks

Aleksei Volkov was sentenced to 81 months in U.S. prison after pleading guilty to selling unauthorized network access used in dozens of ransomware attacks. The article attributes over $9 million in actual losses and more than $24 million in intended losses to the cases.

Mar 24, 2026
Security News · thehackernews.com

U.S. Sentences Ransomware Access Broker to 81 Months, Charges BlackCat Negotiator

Aleksei Volkov was sentenced to 81 months for facilitating ransomware attacks that caused over $9 million in actual losses. Separately, prosecutors charged BlackCat negotiator Angelo Martino and seized nearly $9.2 million in cryptocurrency.

Mar 24, 2026
Security News · bleepingcomputer.com

Tycoon2FA Phishing Activity Rebounds Within Days of Domain Seizures

CrowdStrike observed Tycoon2FA activity drop to about 25% of pre-disruption levels after 330 domains were seized, then return to early 2026 levels within days. The platform continues targeting Microsoft 365 and Gmail accounts.

Mar 24, 2026
Security News · thehackernews.com

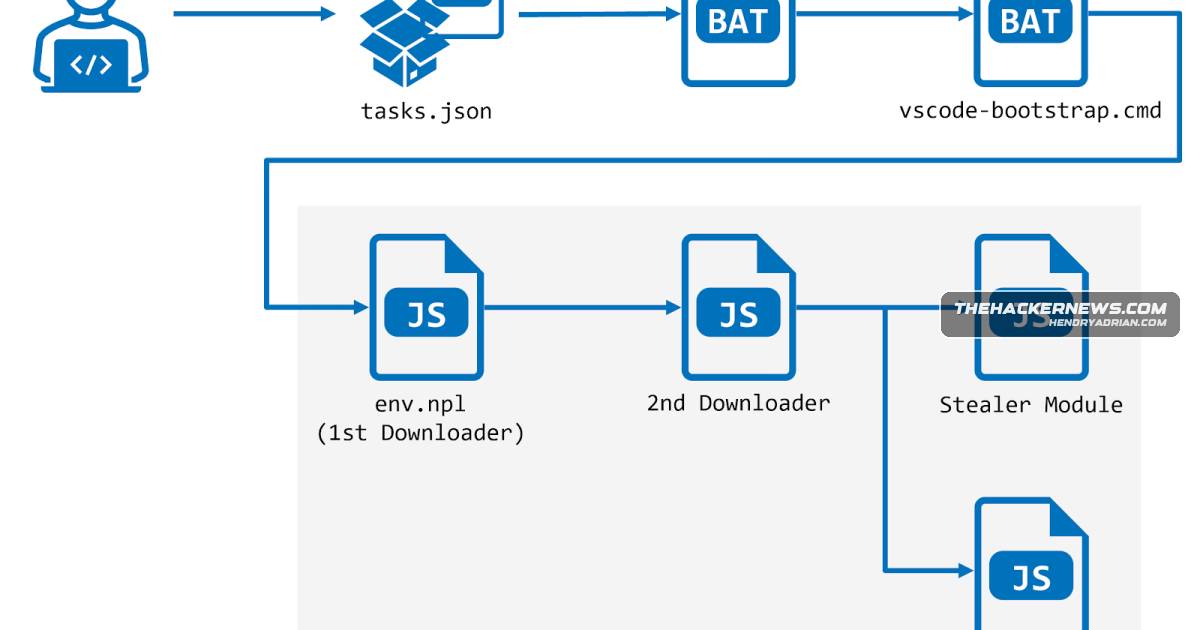
North Korean WaterPlum Uses VS Code Auto-Run Tasks to Deliver StoatWaffle

NTT Security reports that WaterPlum uses malicious VS Code projects to auto-run tasks and deliver StoatWaffle, which includes browser-stealing and RAT modules. Microsoft added settings and prompts to reduce unintended task execution.

Mar 24, 2026
Security News · huntress.com

Huntress Extends Managed Identity Threat Detection to Google Workspace

Huntress announced Managed ITDR for Google Workspace, which monitors suspicious logins and inbox rules. The company says its SOC stopped a stolen-credential attack involving suspicious infrastructure and alert-suppressing Gmail rules.

Mar 24, 2026
Security News · darktrace.com

Darktrace Expands Security Across Email, Collaboration Tools and AI Prompts

Darktrace announced updates combining adaptive security training, email defense, cross-channel message analysis for Slack, Teams and Zoom, and DMARC with attack-surface intelligence.

Mar 24, 2026
Security News · bleepingcomputer.com

Varonis Launches Atlas AI Security Platform for Enterprises

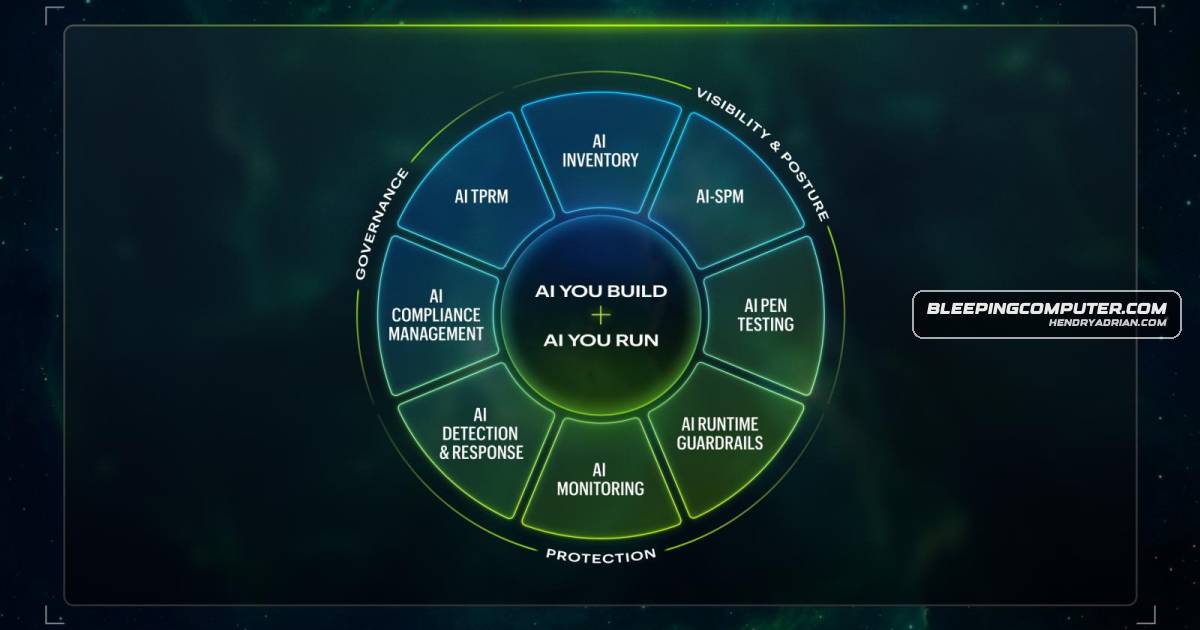
Varonis says its generally available Atlas platform inventories enterprise AI, assesses configurations and data exposure, tests live endpoints for prompt injection and jailbreaks, and provides runtime guardrails, monitoring, and compliance controls.

Mar 23, 2026
Security News · therecord.media

U.S. Sentences James Junior Aliyu to 90 Months for $6 Million Email Fraud Scheme

A U.S. court sentenced James Junior Aliyu to 90 months for his role in a business email compromise scheme that used spoofed payment instructions to redirect wire transfers. Prosecutors estimate the ring stole about $6 million since at least 2017.

Mar 23, 2026
Security News · therecord.media

FBI Warns of Russian and Iranian Campaigns Targeting Messaging Apps

The FBI and CISA warned that Russian actors are phishing users to take over Signal accounts, while an FBI alert linked Iran’s MOIS and Handala Hack to Telegram-connected malware used to monitor targets and exfiltrate files.

Mar 23, 2026
Security News · crowdstrike.com

CrowdStrike SIEM Adds Support for Microsoft Defender and Other Third-Party EDR Tools

CrowdStrike says Falcon Next-Gen SIEM will support third-party EDR, beginning with Microsoft Defender, without requiring a Falcon sensor. The announcement also covers data pipelines, federated search, indicator management, and query translation.

Mar 23, 2026
Security News · securityweek.com

RSAC 2026 Pre-Event Roundup Details Security Product Launches

A pre-RSAC 2026 roundup covers security vendors’ product launches, including AI-agent governance and runtime protection, prompt-injection defenses, AI-driven SOC and exposure remediation, identity security, and vulnerability-management integrations.

Mar 23, 2026
PreviousPage 127 of 159 Next
© 2026 cyber.hendryadrian.com