

AiLock Claims Attack on Artso International, Inc.
AiLock reportedly claimed an attack on Artso International, Inc., alleging encryption to pressure the US-based furniture company and disrupt operations. The claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2828 articles
AiLock reportedly claimed an attack on Artso International, Inc., alleging encryption to pressure the US-based furniture company and disrupt operations. The claim is unconfirmed.

A ransomware.live monitoring record attributes a ransomware claim involving Alberta contractor Prologic Construction to DragonForce. The post says the claim is unconfirmed.

Ransomware.live reports that DragonForce claimed an incident involving UK-based HELIX INTERNATIONAL. The record lists the claim as published May 24, 2026, and says its accuracy cannot be confirmed.

A ransomware.live post attributes a ransomware claim against Indiana-based Heartland Growers to DragonForce. The article says operations were disrupted but notes the information is based on the group’s public claims and is unconfirmed.
A monitoring post lists Turkish energy-sector equipment manufacturer Emek Elektrik as a Bravox victim. It says the claim involved disruption, but provides no independent confirmation.
Ransomware[.]live lists the Salvation Army in Canada as a Bravox victim and reports claimed disruption to its services. The article says the information comes from public group claims and is unconfirmed.
Stormous claims a data dump from vspsolutions.com.au containing 40+ GB of financial backups and other records. The monitoring post says the group’s claims are unconfirmed.
Incransom claims it stole about 100GB of confidential and business data from Spanish aerospace manufacturer Mecanizados y Montajes Aeronáuticos. The monitoring post says the claim is unconfirmed.
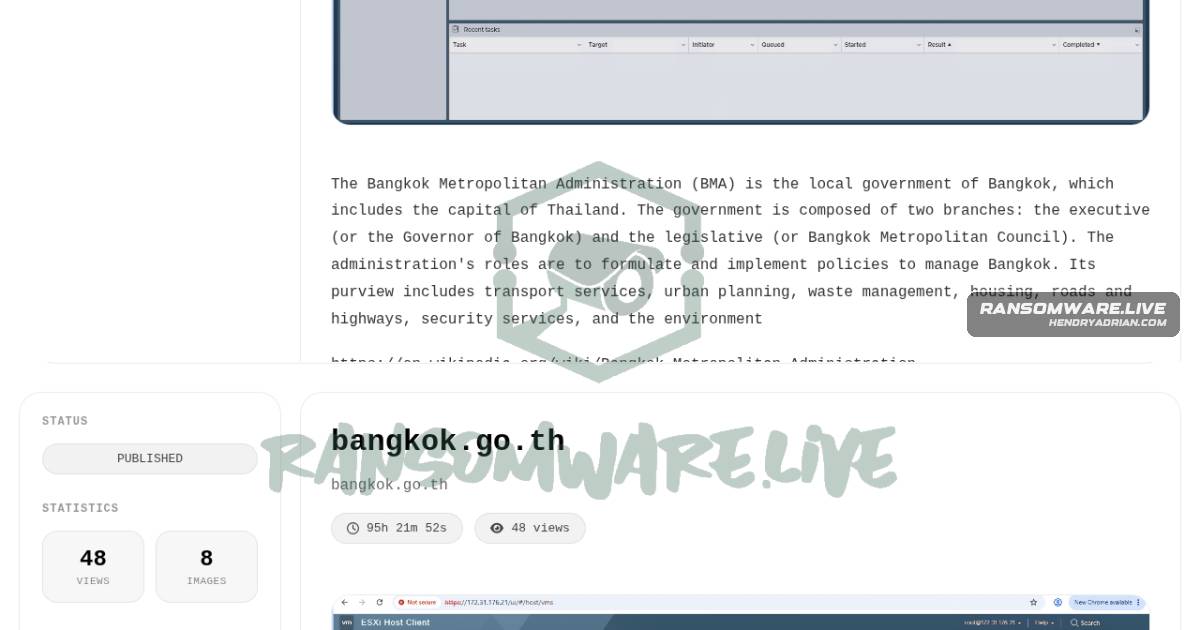
Ransomware.live recorded a Krybit claim naming the Bangkok Metropolitan Administration (BMA) and bangkok[.]go[.]th. The post says services were disrupted, but the information is based on the group’s claim and is unconfirmed.
A ransomware.live post attributes to AuditTeam a ransomware attack on Turkish retailer Mopas Online Supermarket, claiming its online shopping and delivery services were disrupted. The claim is unconfirmed.
The ransomware actor nova claims to have stolen personal data from the University of Valencia, including student records, staff files and children’s photos. The claim is unconfirmed; the actor reportedly offered to negotiate.
A claim attributed to apt73 says Turkey’s TKGM was targeted by ransomware. The monitoring post cites the actor’s leak site and says the claim is unconfirmed.
ShinyHunters claims it ransomware-attacked DentaQuest[.]com and threatens to leak allegedly compromised information unless the victim responds by May 27, 2026. The claim is unconfirmed and attributed to ransomware.live monitoring.
ShinyHunters reportedly claimed it compromised over 42 million Charter Communications records containing PII and issued a final warning on May 23, 2026, demanding contact by May 27. The claim is unconfirmed.
A ransomware.live monitoring record attributes to ShinyHunters a claim that Baker Distributing Company’s Salesforce data was compromised, with a May 27, 2026 leak deadline. The claim is unconfirmed.
Akira claims it hit Karlin Foods with ransomware and says it plans to publish company data, including employee and client information, contracts, financials, and project materials. The claim is unconfirmed.

Ransomware.live lists lasevillanita.com as a victim claimed by Krybit, citing the group’s blog. The post says the claim is unconfirmed.
A monitoring record lists Cablematic Dos Mil SLU as the subject of a ransomware claim attributed to gunra. The post says the claim is based on the group's public assertions and that it cannot confirm their accuracy.
Ransomware.live reported an unconfirmed nova claim naming Virginia-based Hoy Construction. The actor allegedly offered a “tree” and samples from purported stolen data if the company contacted its support department.
Ransomware group nova claims it targeted Vietnam-based AMACCAO and says it will provide a data tree and stolen-data samples through the company's support department. The claim is unconfirmed.
Ransomware.live lists Semgrep as a Qilin ransomware victim, citing a group leak-site post dated May 22, 2026. The report is based on the group's public claim, which the author says is unconfirmed.
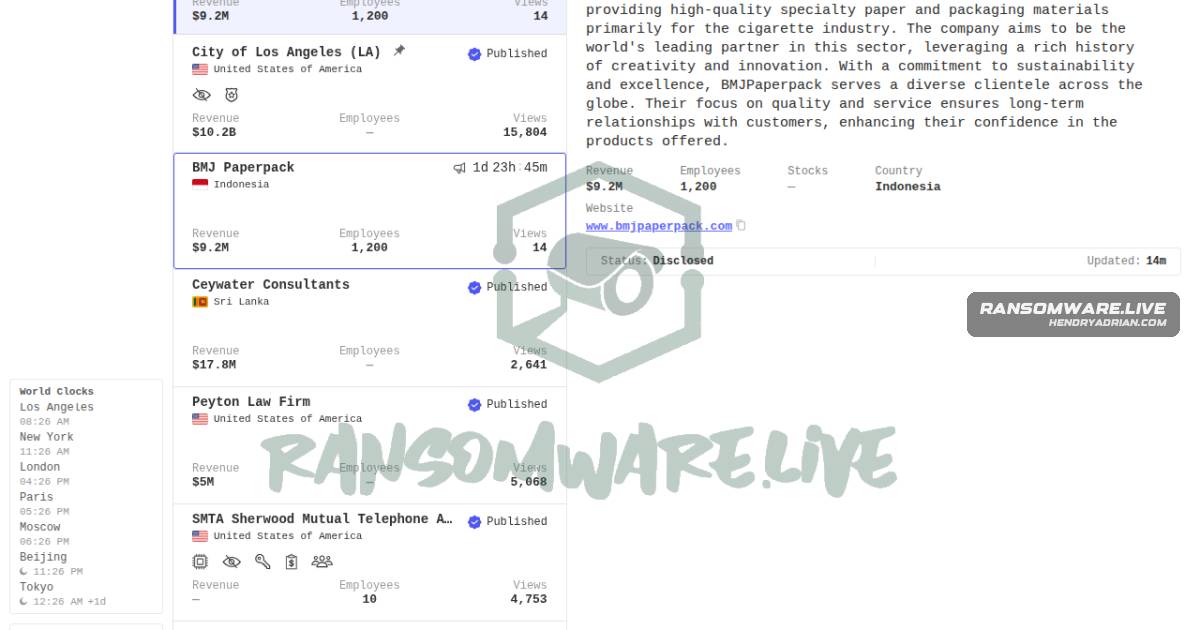
A monitoring post lists BMJ Paperpack in Indonesia as a worldleaks ransomware victim and reports disruption to systems and data access. The post says the group's claims are unconfirmed.
Akira allegedly threatened to publish about 30GB of data from Russian manufacturer GITIS S.r.l., including employee information, contracts, financial records, client data, project files, and NDAs. The claim is unconfirmed.
The incransom group claims it accessed Thread Innovations’ confidential files, including client data, proprietary R&D and financial documentation. The claim was listed by ransomware.live and is unconfirmed.