
Krybit Claims Ransomware Attack on French MSP EURODITEL/RESOTELECOM
Ransomware.live records an unverified krybit claim targeting French managed services provider EURODITEL/RESOTELECOM, published and discovered on October 1, 2026.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2769 articles
Ransomware.live records an unverified krybit claim targeting French managed services provider EURODITEL/RESOTELECOM, published and discovered on October 1, 2026.
A ransomware group called ransomhouse claims it attacked Brazilian logistics operator Terca, disrupting some operations. The monitoring post says the claim is unverified and has not been confirmed by Terca.

Booba Project claims it stole 70 GB of medical data from Associated Gastroenterologists of Central New York. The report, monitored by ransomware[.]live, says the claim is unverified.
The Booba Project claimed it targeted Brazil’s FUNAP and stole 26 GB of data. The monitoring post says the claim is unverified.
A ransomware.live monitoring post records Krybit’s claim against DISK PRECISION GROUP (diskprecision[.]com), alleging operational disruption. The post says the claim is unverified.
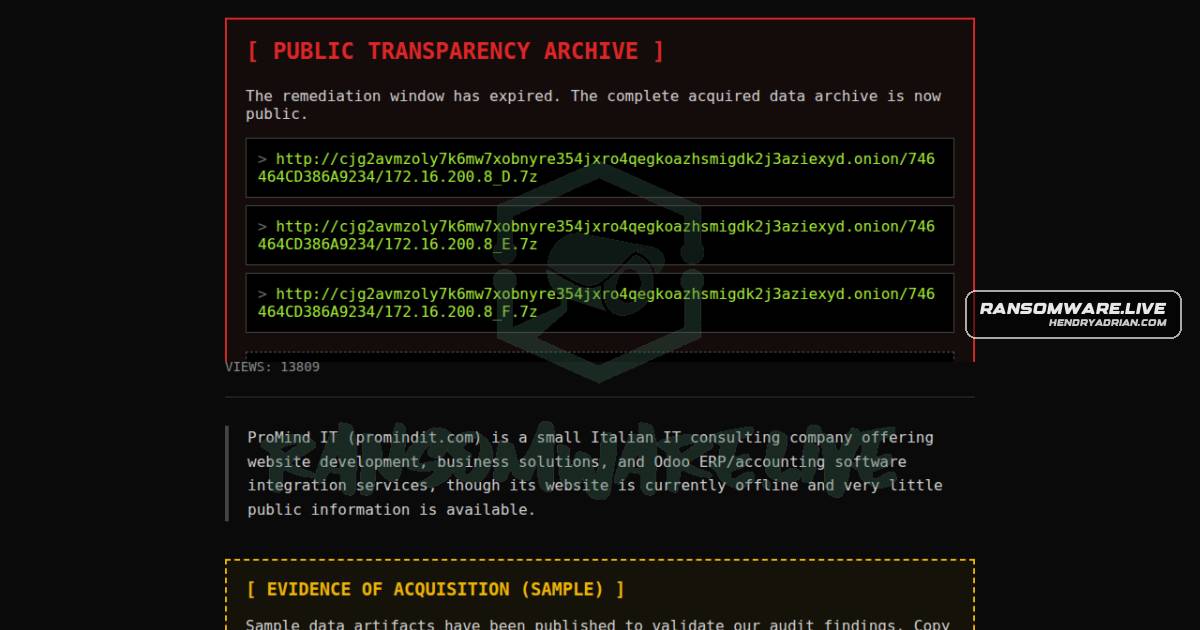
Ransomware.live reports an unverified AuditTeam claim targeting Italian IT firm ProMind IT. The post says the company’s website is offline; the group’s claims have not been confirmed.
AuditTeam claimed it targeted Italian medical device maker Steelco and affected its operations in Italy. The claim is based on public group claims and has not been confirmed.
A public claim attributed to the Genesis ransomware actor says it targeted US healthcare provider TLC Perinatal. The report says operations were disrupted, but notes the claim is unconfirmed.
Ransomware group chaos claims Park Dental has not responded to its demands and threatens to release allegedly stolen data. The monitoring post says the claims are unverified.
Ransomware.live recorded an unverified Safepay claim targeting wolfusofsky[.]de in Germany, with the claim published and discovered on September 30, 2026.
A ransomware.live monitoring post says Vexy Ransomware allegedly targeted Summit Electric Supply; the claim and reported operational disruption are unconfirmed.
A ransomware.live record says Eclipse claimed an attack on The Japan Times, allegedly disrupting services and subscriptions. The claim is unverified.
Ransomware group pear claimed Software Answers, a US-based accommodation software provider, as a victim. The monitoring post says the claim is unverified.
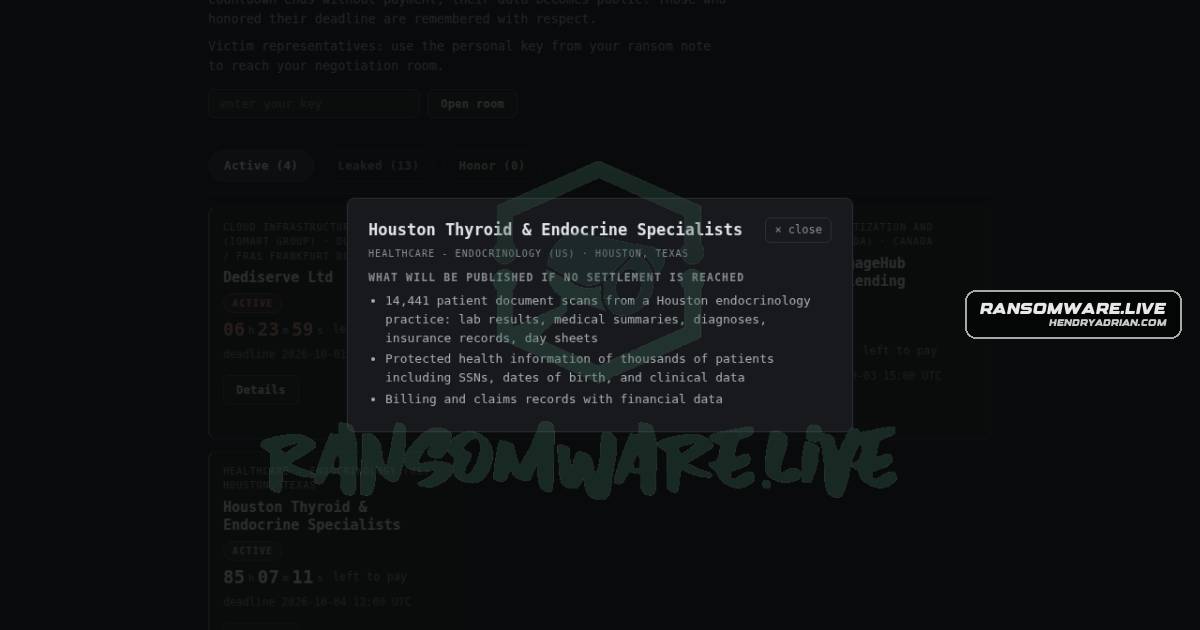
Ransomware group N0n claims it stole 14,441 patient document scans and other sensitive records from Houston Thyroid & Endocrine Specialists. The monitoring post says the claims are unverified.
A ransomware.live monitoring post says the Play group claimed to target German manufacturer Orth Automobile. The post says the claim could not be independently confirmed.
The Play ransomware group claimed Airtech Mechanical Services in the United States was affected by an attack. The monitoring post says the claim has not been independently confirmed.
A ransomware.live monitoring post records Play’s claim that it targeted German technology firm Titus. The claim is unverified, and the post says it cannot confirm the information.
Ransomware group settra claims it has 27 years of DFI Retail Group email archives, records on 397 stores, and 40,000 medical files. The monitoring post says the claims are unverified.
The ransomware group emperador claims it breached SitePro Rentals and threatens to leak employee data unless contacted within 72 hours. The claim is unverified; the post says a law firm is investigating.
A ransomware.live monitoring post says the netrunner group allegedly targeted P***** M***** I** to encrypt files and disrupt operations. The claim is unverified.
Rhysida claimed clicks digital GmbH, a German online marketing agency, as a victim. The monitoring post cites the group’s claim, which it says it cannot independently verify.

The ransomware group Storm reportedly targeted California landscaping company Gardeners’ Guild, with claimed operational impact in the US. The post says the claim has not been independently confirmed.
A ransomware-monitoring post says the Storm group claimed West County Health Centers, a California healthcare provider, as a victim and reported operational impact. The claim is unverified.
Ransomware.live lists www.newyjh.com in Korea as a claimed ULose ransomware victim, with the status marked “Sale.” The report says systems were disrupted and files encrypted, but notes the claim is unconfirmed.