
Nova Claims Data Theft at IBENA Textilwerke
Ransomware.live records an unverified claim by the nova actor targeting IBENA Textilwerke in Germany. The actor claims data exfiltration and offers decryption for two files.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2822 articles
Ransomware.live records an unverified claim by the nova actor targeting IBENA Textilwerke in Germany. The actor claims data exfiltration and offers decryption for two files.
Ransomware.live reports that actor nova claimed Everlite Concept data theft and provided a data tree and samples to the French company’s support team. The claim is unverified; no company statement is included.

A ransomware.live monitoring post attributes a ransomware claim against Taos Mountain Casino to DragonForce, alleging operational impact and remediation efforts. The post says the claims are unconfirmed.

Abyss ransomware reportedly made data-extortion and disruption claims against School Facility Consultants, a California school-facility planning and funding company. The post says the claims are unconfirmed and was monitored by ransomware[.]live.
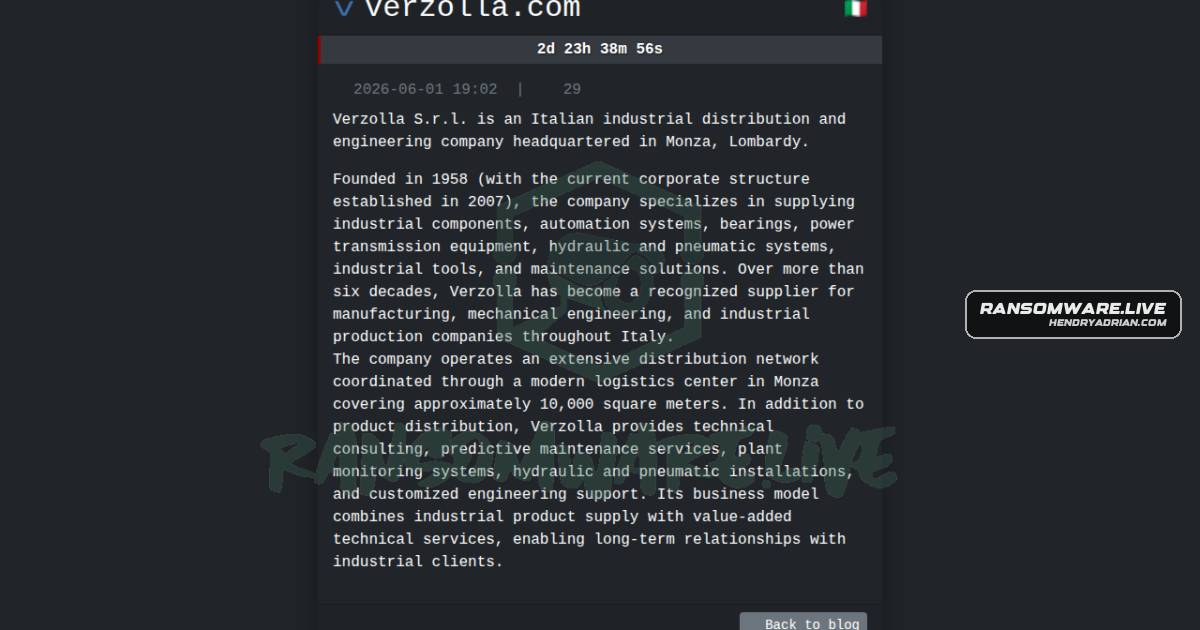
Ransomware[.]live reports SafePay listed verzolla.com, an Italian industrial components and automation supplier. The post is based on the group’s public, unconfirmed claim.
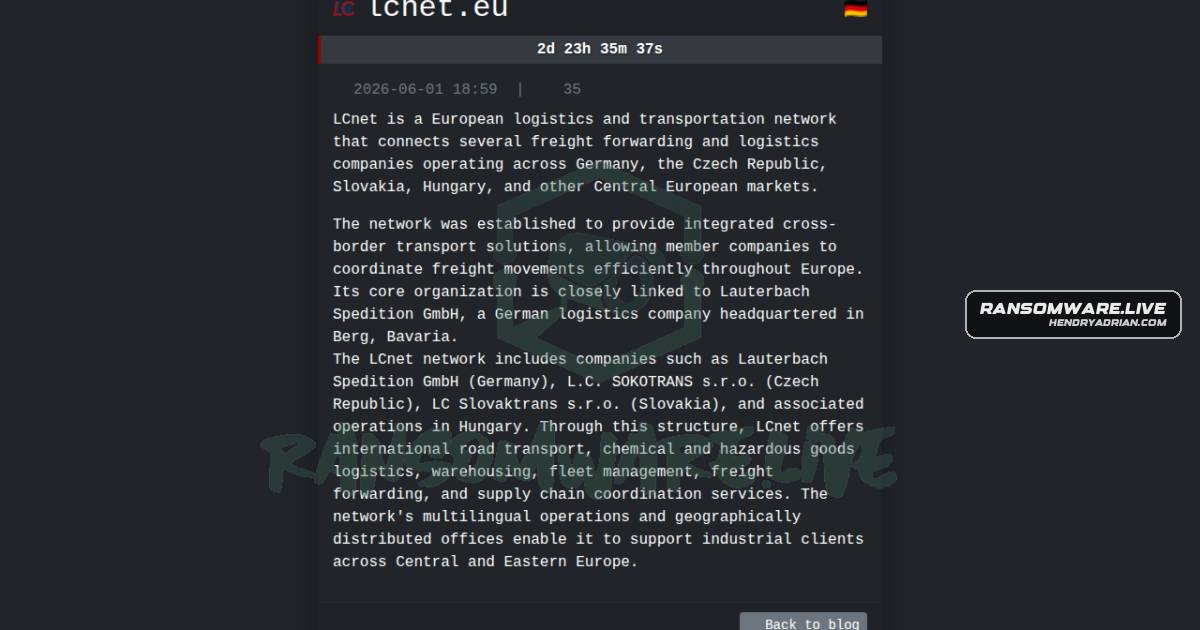
SafePay claims disruption to lcnet[.]eu, a German cross-border transport coordination network. The claim was published June 1, 2026; ransomware.live says it cannot confirm its accuracy.
A ransomware.live-monitored post attributes an extortion claim against Cropwise (Syngenta Group) to shadowbyt3$. The actor claims it stole 10.4 MB of data and demands payment; the post says the claims are unconfirmed.

A monitoring record attributes an Anubis ransomware claim to Power & Tel and says data affecting ecommerce platforms was exposed. The post says the claim is unconfirmed.
Safepay claims it targeted soraris[.]it, an Italian waste-management company. The post describes disruption to its operations, but the publisher says it could not confirm the group's claims.
Ransomware.live lists Parsa Beauty (parsa-beauty[.]de) as a SafePay ransomware claim, dated June 1, 2026. The article says the group’s claim is unconfirmed.
Ransomware.live records an unconfirmed SafePay claim naming tavolaspa[.]com in Italy. The claim says the group targeted the company and extorted data; no independent confirmation is provided.

DragonForce claims it targeted Sri Lanka-based Synex International Pvt Ltd. The monitoring post says the company’s MEP, ELV and solar operations were affected, but the claim is unconfirmed.
Ransomware.live attributes a ransomware claim concerning squamish[.]net, a Canadian ISP, to BrainCipher. The post says services were disrupted but states the information is based on the group’s public claim and is unconfirmed.
Kairos claimed responsibility for targeting Mortensen Law Offices, PLLC. The monitoring post says the claim is unconfirmed and offers to share an official statement from the firm.
A ransomware.live monitoring post attributes a claim against US telecommunications organization Hightower Communications to the Play ransomware group. The post says disruption and encryption occurred but notes the claim is unconfirmed.
Ransomware.live lists Digitall Graphics in Canada as a claimed Play ransomware victim, citing a public group claim. The post alleges system disruption and possible file encryption but says the information is unconfirmed.
Incransom reportedly claimed an attack on Champaign-Urbana Public Health District that disrupted public health and support services. The monitoring post says the group’s claims are unconfirmed.
Ransomware.live reports an unconfirmed AiLock claim that Schneebeli AG, a Swiss carpentry firm, was compromised. The post alleges ransomware deployment, operational disruption, and a payment demand.
A ransomware monitoring post attributes an attack on Limburg-Weilburg County’s district administration in Hesse, Germany, to abyss. The post says public services were disrupted, but the claim is unconfirmed.
ransomware.live reports that bravox listed Grupo Mau as a victim. The claim is attributed to the group’s blog and is unconfirmed; the post says it cannot verify the information.
A ransomware.live monitoring post attributes to Lapsus$ a claim that data from MAPFRE ASSURANCE in Spain was acquired by a private party and would not be publicly leaked. The claim is unconfirmed.
A ransomware.live record attributes to Lapsus$ a claim that MERCOR data was acquired by a private party and will not be publicly leaked; the report says it cannot confirm the claim.
A ransomware claim by cmdorganization targets Lee Law Offices, a law firm serving North and South Carolina. The claim is unverified; the article does not confirm compromise, encryption, or data theft.
Nova claims it targeted LTI Services and Larick Towing, seized their websites, and threatens to leak database material. The claims are unconfirmed; Nova offered to decrypt two files as proof and set an 11-day response deadline.