

Anubis Claims Small Breach at D&M Contractors
Ransomware.live lists D&M Contractors as a victim claimed by Anubis, which alleges a small breach involving real employee data. The claim appeared June 5, 2026, and is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2821 articles
Ransomware.live lists D&M Contractors as a victim claimed by Anubis, which alleges a small breach involving real employee data. The claim appeared June 5, 2026, and is unconfirmed.
Ransomware.live lists Shantou Huashan Electronic Devices Co., Ltd. (SHEDCL), associated with huashan[.]com[.]cn, in a krybit ransomware claim dated June 6, 2026. The post says the claim is unconfirmed.
Ransomware.live lists schultz[.]com[.]br as a victim of a claim by krybit, citing the group’s post. The listing gives June 5, 2026, as the discovery and publication date; the claim is unconfirmed.
Nova claims it encrypted Aspire Hospital’s servers and stole patient data, citing aspirehospitals[.]co[.]in and aspirehospitals[.]in. The claims are unconfirmed; the post says it is based on the group’s public claims.
A ransomware.live record lists Demand.ioNEW (also referred to as Demand.io in the text) as the target of a coinbasecartel claim, citing a leak-site entry and demanding payment under threat of data disruption. The claim is unconfirmed.

Akira claims it accessed and encrypted systems at Kennon Worldwide and says 30 GB of corporate data—including contracts, client information and NDAs—will be uploaded. The claim is unconfirmed; ransomware[.]live monitors it.
Ransomware.live lists Kriete Truck Centers as the subject of an AWAITING claim by securotrop, estimating 221 GB of data impacted. The claim has not been confirmed by the victim.
Qilin listed Central Florida Cosmetic & Family Dentistry as a U.S. ransomware victim on June 5, 2026, according to ransomware.live. The post says the claim is unconfirmed.
A ransomware.live monitoring post attributes to nightspire a claim targeting Krum Public Library files, including financial, HR and supervisor information. The post says the claim is unconfirmed.
Akira claims it will encrypt and leak 35 GB of T/CCI Manufacturing data, allegedly including employee identity and payment documents, contracts, and financial records. The claim is unconfirmed.
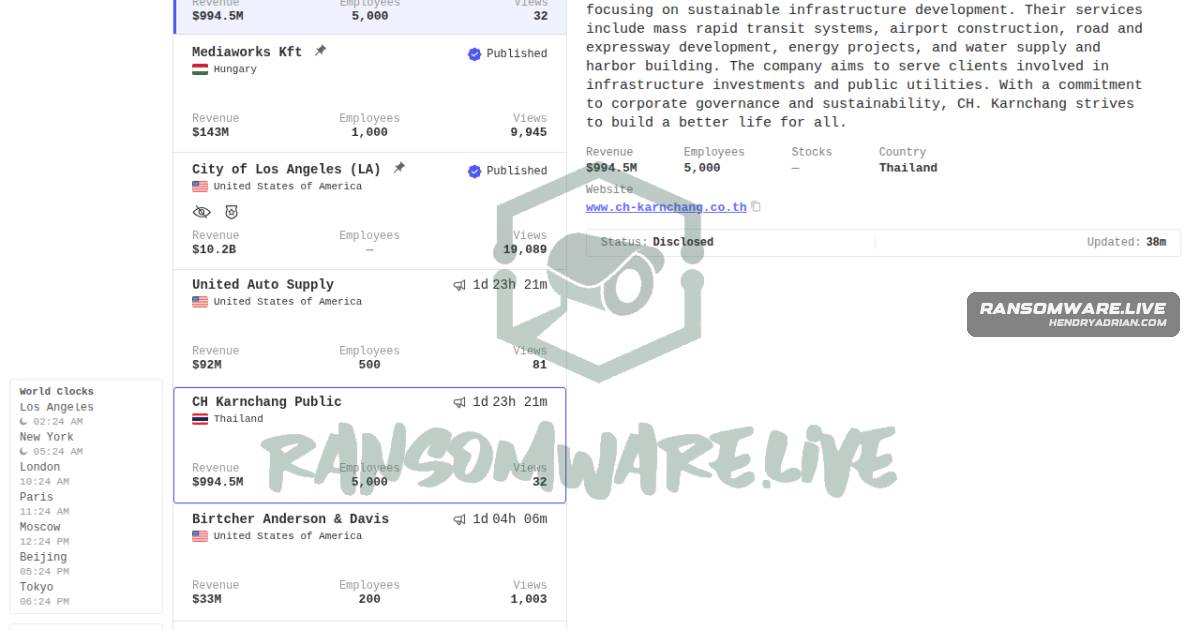
Ransomware.live lists a WorldLeaks claim dated June 5, 2026, alleging that the Thai construction firm CH Karnchang Public was targeted and its operations disrupted. The post says the claim is unconfirmed.
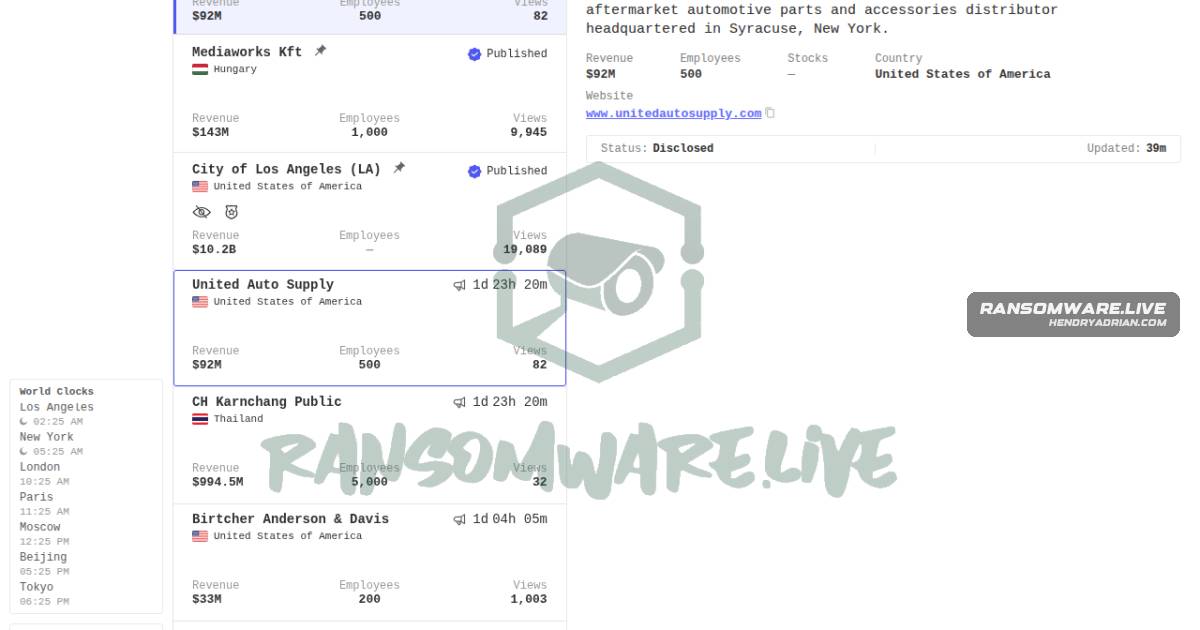
A ransomware.live monitoring post lists United Auto Supply as a Worldleaks victim, citing the group's leak-site entry. The alleged attack, disruption, and data held for ransom are unconfirmed.
Ransomware.live records an unverified Play group claim against The Chapel in the United States. The post attributes claims of unauthorized access and encryption to the group; the incident is not independently confirmed.
A ransomware.live monitoring record attributes to the Play group a claim targeting Dallis Law Firm and alleges files were encrypted or locked and a ransom demanded. The claim is unconfirmed.
Play claimed Urschel Laboratories was targeted and that the incident caused service disruption and data compromise. The monitoring post says the claims are unconfirmed.
Qilin claimed it compromised Trican in Canada, encrypted data and threatened further disruption unless a ransom is paid. The article says the claim is unconfirmed and is based on the group’s public post.
A ransomware.live record attributes a claim targeting Austrian company Avcon Jet to Qilin. The post says systems were encrypted and disrupted, but notes the group’s claims are unconfirmed.
Qilin claimed SKUPINA Don Don in Slovenia as a ransomware victim. The claim was reported by ransomware[.]live and is unconfirmed; the article provides no independent confirmation.
A ransomware[.]live listing attributes to Akira a claim that Northern Ohio Regional Multiple Listing Service was affected, alleging theft and encryption of corporate files including board information, contracts, NDAs and financial records. The claims are unconfirmed.
Akira claims 53 GB of National Standard Parts Associates data is at risk of exfiltration and encryption, including employee documents, contracts, client information, NDAs and financial records. The claims are unconfirmed.
Ransomware monitoring reports that incransom listed US-based CUSTOMSIGN on its disclosure page. The claim is unverified; the article says it cannot confirm the information.
Stormous allegedly claims to have extracted 150 GB of data from Saudi Arabia’s SA2000[.]COM, including financial, customer, employee and business records. The claim is unconfirmed; the company’s response is pending.
SpaceBears claims it exfiltrated employee and client personal information, financial documents, and other files from Brazilian company Sicol. The allegation is based on a leak-site claim and is unconfirmed.

Ransomware.live lists an Anubis claim involving Singing River Health System, published June 3, 2026. The article says the claim is unconfirmed and provides no details on affected data or impact.