

Lapsus$ Claims AYA Bank Data Theft, Threatens Sale
Lapsus$ claims it exfiltrated AYA Bank’s main-platform data, including PII, and threatens to sell it if the bank does not contact the group or pay. The claims are unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2817 articles
Lapsus$ claims it exfiltrated AYA Bank’s main-platform data, including PII, and threatens to sell it if the bank does not contact the group or pay. The claims are unconfirmed.
A monitoring post lists Singapore’s Lee International as a Qilin ransomware victim, citing the group’s leak-site claim. The post alleges systems were disrupted; the claim is unconfirmed.
A ransomware[.]live monitoring post attributes an unconfirmed claim to Interlock that Reynella East College in Australia had 600 GB of files and sensitive student and staff data leaked; the post says it cannot verify the claim.
Nova allegedly claimed it exfiltrated CloudQuantum data and threatened disclosure unless the company contacted its support team. The post says Nova provided a data-tree and samples; the claim is unconfirmed.
Icarus reportedly claimed it stole compressed Salesforce data from Cbassociations. The claim is unconfirmed; the post says it is based on public group claims and offers to share an official statement.
Icarus claims it compromised Cqcrm’s Salesforce environment and stole compressed Salesforce data. The report attributes the information to public claims by the group and says it is unconfirmed.
Ransomware.live lists Randa Apparel & Accessories as a victim of a ransomware claim by the Chaos actor, alleging encrypted systems and operational disruption. The claims are unconfirmed, and no official response is provided.
A ransomware.live record attributes to Icarus an unconfirmed claim that Salesforce data belonging to Gms-net was stolen and exfiltrated in compressed form.
Icarus reportedly claims it stole compressed Salesforce data from HDS (Hdscorp). The article attributes the claim to the ransomware group but says it cannot confirm the information.
Incransom claims Belpointe Asset Management/Belpointe was affected and alleges 400 GB was stolen. ransomware.live says it cannot confirm the claim.
Ransomware.live reports an unverified Icarus claim that Huntress's Salesforce data was encrypted and compressed data stolen. The post says the claim has not been confirmed.
Qilin claims it targeted U.S. homebuilder Schumacher Homes in a ransomware incident. The claim alleges disruption to systems and data availability, but its accuracy is unconfirmed.
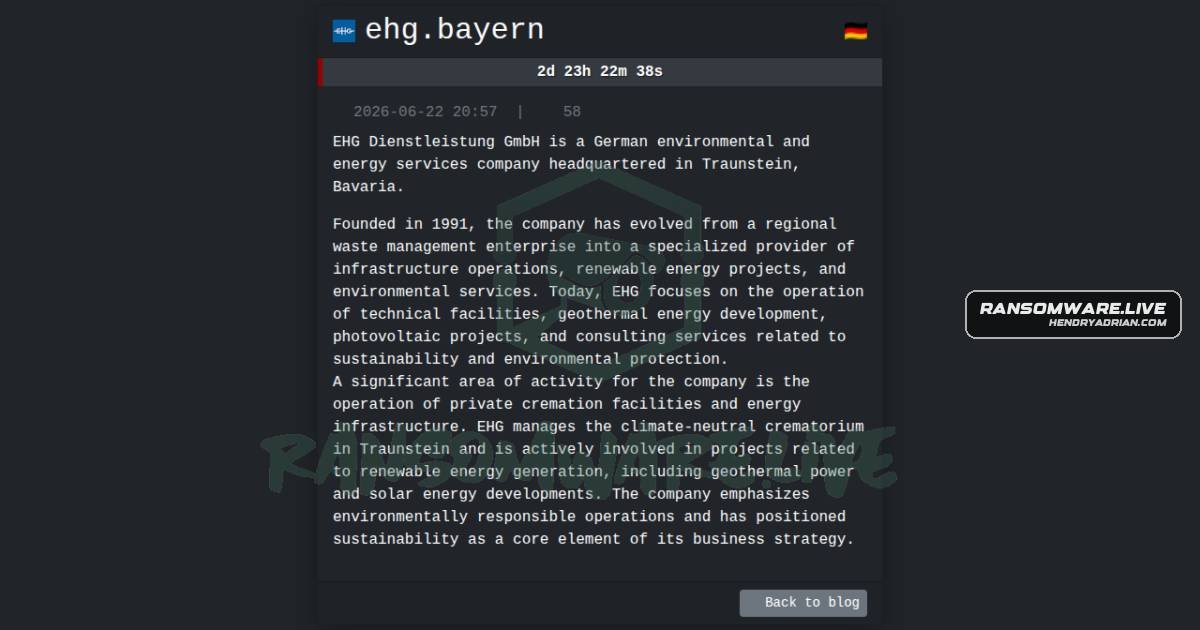
Safepay claims it compromised ehg[.]bayern’s infrastructure in Germany and disrupted services and systems. The monitoring post says the claim is unconfirmed.
Akira allegedly claims it will upload 62 GB of Ntd Apparel data, including employee personal information, projects, client information, and confidential agreements. The claim is unverified.

A ransomware claim naming BITS Pilani and attributed to DragonForce was listed on the group's leak site. The monitoring post says the claim is unconfirmed; it provides no independently verified incident details.
Ransomware.live reports that Qilin claimed the Central Bank of Libya as a victim. The claim is unconfirmed; the record cites a Qilin leak-site URL.
Aurora claims it took extensive data from Aerospace & Advanced Composites GmbH, including engineering records, credentials, HR files and financial data. The monitoring article says the claim is unconfirmed.
A monitoring post attributes an unconfirmed ransomware incident involving Union Tractor to cmdorganization. The record lists the discovery and publication date as June 22, 2026.
A ransomware.live post says Qilin listed US construction company Homes By J Anthony as a victim. The claim is unconfirmed; the article reports alleged impacts to business operations and data availability.
A monitoring post reports an unconfirmed Nightspire ransomware claim targeting US-based Dean Cosmetic Dentistry; the post says no data details are available.
Ransomware.live reports that Qilin claims Florida Engineering Services was targeted, with alleged disruption and data impact. The record is based on the group’s public claims and is not independently confirmed.
A ransomware.live monitoring post attributes a ransomware attack claim against US-based Tri-tec to Qilin. The post says files were encrypted, but notes that the information is based on the group’s public claims and is unconfirmed.
Wall ISD in Texas was named in a ransomware claim attributed to cmdorganization and monitored by ransomware.live. The post says the claim is unconfirmed.
A ransomware.live-monitored post attributes a ransomware claim targeting Sivatel Bangkok to Qilin. The reported disruption and data impact are unconfirmed; the article says it is based on the group’s public claim.