
Qilin Claims Filtronic as a Ransomware Victim
Ransomware.live records an unconfirmed Qilin claim naming UK manufacturer Filtronic as a victim. The claim was listed on August 7, 2026; the article says its accuracy could not be confirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2801 articles
Ransomware.live records an unconfirmed Qilin claim naming UK manufacturer Filtronic as a victim. The claim was listed on August 7, 2026; the article says its accuracy could not be confirmed.
A ransomware.live monitoring post attributes a claim targeting US manufacturer Astro Electroplating to Qilin. Reported encryption and business disruption are unconfirmed; the post says it is based on the group’s public claim.
Ransomware.live records a bravox ransomware claim naming French packaging manufacturer MEDICOS, published on Aug. 7, 2026. The report says the claim is unconfirmed.
Ransomware[.]live lists Brazilian engineering and construction company Alya Construtora as a ransomhouse target; the group reportedly claims operational disruption. The post says the claim is unconfirmed.

A ransomware.live monitoring post attributes a claim targeting Hartfiel Automation to thegentlemen and reports an impact on operations in Germany. The post says the claim is unconfirmed.
A ransomware.live monitoring record attributes a claim of operational disruption at Pioneer Bank to the Storm ransomware group. The article says the claim is unconfirmed.
A ransomware claim attributed to SpaceBears names Italian IT provider Hitech Distribuzione Informatica (HTDI) as a victim. The monitoring post says the claim was published August 7, 2026, and could not be independently confirmed.
BlackNevas claims it targeted OTE Group (OTEGROUP), an Oman-based business group. The post cites an onion source and was monitored by ransomware[.]live; the claim is unconfirmed.
Unverified ransomware claim monitoring by ransomware[.]live names Rose Kennedy Greenway Conservancy as a victim of L Group and alleges disruption to its U.S. services.
L Group claims ausfec1[.]com[.]au was affected by a ransomware incident, with the claim attributed to the group’s leak-site post and monitored by ransomware[.]live. The report says the claim is unconfirmed and encryption is only potential.
Ransomware.live lists Universidade Veiga de Almeida in Brazil as a claimed L Group victim, citing a group leak-site post. The alleged compromise is unconfirmed, and the article provides no independent evidence.
Krybit’s leak site reportedly claimed an attack on French cooperative ERNAT (www[.]ernat-bureau-etudes[.]fr). The claim is unverified; the article says it cannot confirm the information.
Ransomware[.]live lists Actini Group (ACTINI SAS) in France as a Krybit ransomware claim, linked to the actor’s onion post. The publisher says the claim is unconfirmed.
Ransomware.live lists French cleaning company REFLET 2000 as a Krybit target, citing the group’s blog. The post is dated Aug. 7, 2026; the incident is unconfirmed.
A ransomware.live monitoring record lists Mayer Brown as a victim of SilentRansomGroup. The record says the activity disrupted services, but the claim is unconfirmed.
Ransomware.live lists HYMIASA, a Mexican fluid-systems company, as a Krybit victim in Peru. The post alleges operational disruption, encryption and data compromise; the information is unconfirmed.
Ransomware.live records an unverified krybit claim targeting Serengeti Golf and Wildlife Estate in South Africa, published Aug. 7, 2026. The article does not independently confirm compromise.
A ransomware.live monitoring entry attributes a claim concerning Singapore-based manufacturing company Platinum Group to the play ransomware actor. The post says the claim is unconfirmed.
A ransomware.live-monitored record attributes a claim about GCATS Investments to the Play ransomware group; the post says the claim is unconfirmed.
Ransomware.live reports an unverified Play ransomware claim targeting U.S.-based Signature Services, published Aug. 6, 2026. The post says the information has not been independently confirmed.
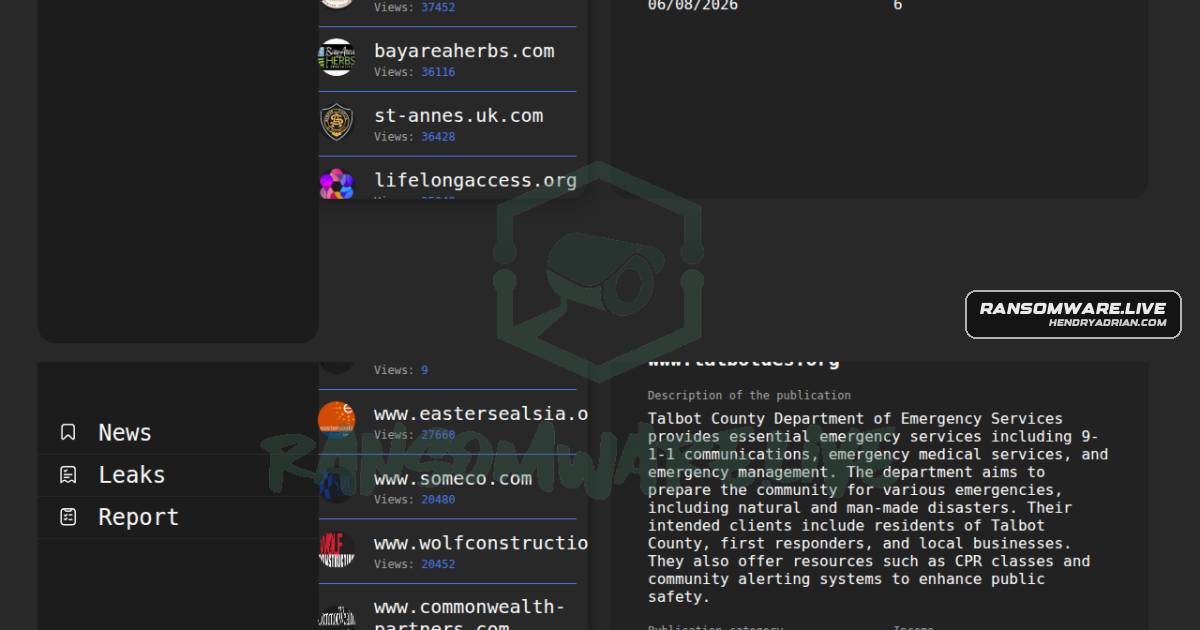
Ransomware.live records a Lynx claim involving www[.]talbotdes[.]org and alleged disruption to emergency communications, medical services and emergency management. The post says the claim is unconfirmed.
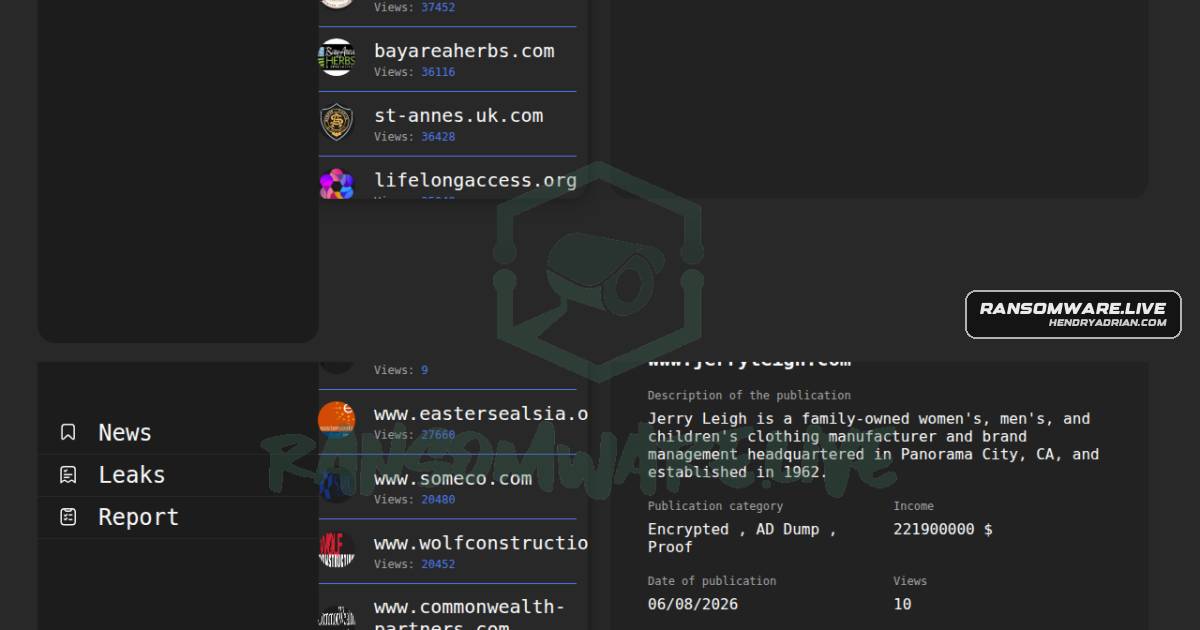
ransomware[.]live lists Jerry Leigh as a Lynx victim based on the group’s public claims. The alleged disruption to systems and data is unconfirmed.
Ransomware.live reports that Qilin claimed ALIZE, a French professional-services organization, as a victim on Aug. 6, 2026. The claim is unverified, with no independent confirmation provided.
ransomware.live reports that Qilin listed US-based AmSpec as a ransomware victim on August 6, 2026. The claim is unconfirmed; the article says it is based on the group's public claims.