
Dire Wolf Claims AliveCor Targeting in August 2026
Ransomware.live lists AliveCor, Inc. as a Dire Wolf ransomware target, with an August 10, 2026 claim that attackers sought to disrupt critical-system access; the claim is unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2797 articles
Ransomware.live lists AliveCor, Inc. as a Dire Wolf ransomware target, with an August 10, 2026 claim that attackers sought to disrupt critical-system access; the claim is unconfirmed.
A ransomware.live monitoring record says the direwolf group listed Swyft Inc., a US-based retail technology and SaaS company. The claim is unconfirmed; the post says it cannot verify the group’s assertions.
Qilin claimed HIGEN MOTOR in South Korea as a ransomware victim, with critical data reportedly involved. The monitoring post says the claim is unconfirmed.

Akira claims it will upload 180 GB of One Vision Imaging data, including employee and HR files, contracts, and client information. The claim is unverified and monitored by ransomware[.]live.
Ransomware.live lists Verona 83 in Italy as a bravox ransomware claim dated Aug. 10, 2026. The post alleges operational disruption, but the incident and impact are unconfirmed.
Global Secret Group claims it targeted Florida’s Coggins Insurance Agency and encrypted 85.9 GB of data. The post reports 245,768 files across 26,563 folders; the claim is unconfirmed.
Ransomware.live lists a Panzer claim involving Thailand’s Minor Food Group. The post links to the actor’s claim but says it cannot confirm the information; no compromise is independently established.
Ransomware.live lists an unverified Akira claim that 170 GB of ALCAST corporate data was exfiltrated and may be uploaded, potentially including employee personal files, customer data, projects and contracts.
Ransomware.live reports that the unsafe group claims it encrypted Presentations.AI’s systems and demanded payment. The post alleges operational impact and $5 million in revenue loss, but says the claims are unconfirmed.
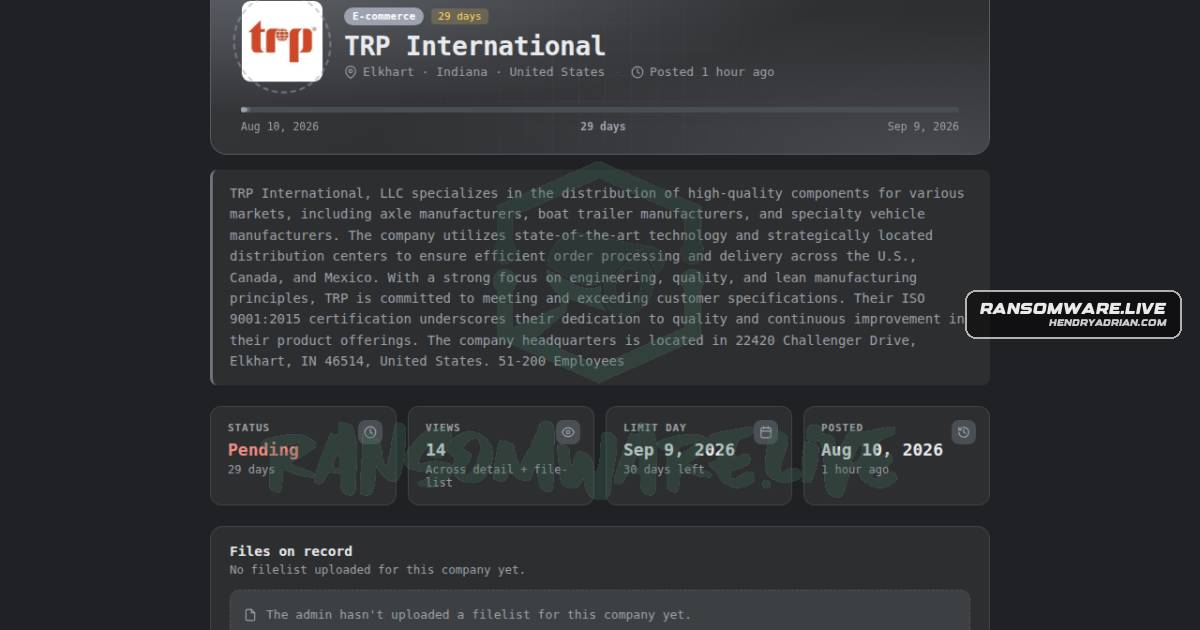
Ransomware.live records an unverified Storm ransomware claim naming TRP International in the U.S. The post says distribution and operations were disrupted, but provides no independent confirmation.
Storm claimed it targeted Southern Metals, a US metal recycler, and allegedly affected its operations. The monitoring post says the claim is unconfirmed.
Ransomware.live lists Cook Remodeling as a Global Secret Group victim, alleging 23.2 GB of data across 47,193 files and 8,323 folders was exposed. The post says the claims are unconfirmed.

Ransomware.live reports that Dragonforce claimed Baicizhan, a Chinese English-learning platform, as a target. The post alleges service disruption but says the group's claims are unconfirmed.
A ransomware monitoring post attributes a claim against Finland’s Naval Interior Team to Qilin. The post says disruption and file encryption were reported but states the group’s claims could not be confirmed.
Ransomware.live lists a Qilin ransomware claim involving Mexico’s Price Shoes. The post says systems were accessed and encrypted or disrupted, but the information is based on the group’s public claim and is unconfirmed.
A ransomware.live monitoring post attributes a claim to Qilin against Chun Tai Sing Chemical Industry in Hong Kong, alleging encrypted files and business disruption. The post says the claim is unconfirmed.
Ransomware.live reports that Qilin claimed to target Japan’s East Field Corporation, with alleged disruption to access to systems and data. The claim is unconfirmed.
A ransomware monitoring record attributes a claim involving Panda Logistics Taichung Branch in Taiwan to Qilin. The post cites the group’s leak site, but says the claim’s accuracy has not been confirmed.
Qilin is reported to have claimed a ransomware attack against Taiwan’s Energetic Development Corp. The claim is attributed to the group and monitored by ransomware.live; the information has not been independently confirmed.
Ransomware.live lists Synergy Interactive as a Qilin ransomware-group victim, citing a group leak-site post dated Aug. 9, 2026. The claim is unconfirmed, and no official victim statement is included.
A ransomware.live monitoring post attributes a ransomware claim against Marconi Industrial Services in Italy to Play. The post says encryption reportedly disrupted operations, but notes the claim is unconfirmed.
Ransomware.live lists Rilpa Enterprises in Canada as a Play ransomware claim dated Aug. 9, 2026. The post says the claim is unconfirmed; no statement from the affected organization is provided.
Ransomware.live lists UK professional-services firm MIE Solutions as a Play ransomware victim, citing the group’s public claim. The post alleges systems and data impact and operational disruption, but says the claims are unconfirmed.
Ransomware.live reports that Qilin claimed Harplast SRL in Romania as a victim. The post attributes alleged file encryption and operational disruption to the group; these claims are unconfirmed.