
Majinahanashi Claims SON-VIDEO as a Ransomware Victim
Ransomware group Majinahanashi claimed SON-VIDEO, a French hi-fi and home-cinema retailer, as a victim. The claim is unverified, and the article provides no confirmation from the company.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2764 articles
Ransomware group Majinahanashi claimed SON-VIDEO, a French hi-fi and home-cinema retailer, as a victim. The claim is unverified, and the article provides no confirmation from the company.

Ransomware group incransom claims it accessed and exfiltrated sensitive Health Sciences Centre data in Winnipeg. The hospital’s management reportedly said no sensitive data was affected; the claims have not been independently confirmed.
Ransomware.live records an unverified Majinahanashi claim targeting KT RESTAURANT, a Thai restaurant operator behind the Santa Fe steakhouse chain in Bangkok. The source says the claim’s accuracy has not been confirmed.
A ransomware-monitoring post says actor Majinahanashi claimed an attack on India’s BONJOUR GROUP. The post notes the claim is unverified.
Threat actor Majinahanashi claims PIO PIO, a Colombian rotisserie restaurant chain with more than 10 locations, as a ransomware victim. The claim has not been independently confirmed.

A ransomware.live record says Qilin claimed an attack on Colombia-based ACI Proyectos SAS, reportedly disrupting access to systems and data. The claim has not been independently confirmed.
Ransomware.live lists DexCom as a Redact ransomware victim and reports operational disruption, based on the group’s unverified public claim. The article says the information has not been independently confirmed.
Ransomware.live reports that UmBra claimed an attack on Helwan University in Egypt. The post says university services and critical systems were disrupted, but notes the claim has not been independently confirmed.

Rhysida claims it stole data from law firm Gress Clark Young & Schoepper, including client and firm records, medical information, and e-file system credentials. The claims have not been independently verified.
Ransomware group exitium claims it stole 5.8 TB of data from Japanese manufacturer KOIKE Sanso Kogyo and threatens to sell it unless the company makes contact by October 13, 2026. The claims are unverified.

Ransomware.live reports that the group thegentlemen claimed to target AnyTech365, a Spanish IT security and remote support provider. The claim is unverified; the post provides no details about compromised data or operational impact.

Ransomware group thegentlemen claims it accessed or encrypted systems at Aquatech, a US water treatment technology company. The report says the claim is unverified.

A ransomware group called thegentlemen claimed the Saskatoon Tribal Council as a victim. The post says the claim is unverified and reports no confirmed impact or official statement from the council.
The ransomware group thegentlemen claims it targeted D.W. McMillan Memorial Hospital in Brewton, Alabama. The post says the claim is unverified and reports no official confirmation from the hospital.
The ransomware group ThreeAM claims it targeted California fleet-services company Fleetworks Inc. The claim was posted on October 9, 2026, and has not been independently confirmed.
Ransomware.live reports that Qilin claimed an attack on Sweden’s Vadeto Group, with alleged encryption and operational disruption. The claims have not been independently confirmed.
A ransomware.live listing says Settra targeted northshoresun.timesreview.com and associates the claim with the NEWSPAPER ransomware family. The post says the claim has not been independently confirmed.

Ransomware.live reports that the Panzer group claimed Solutend, a Bolivian technology company, as a victim. The claim was published on October 9, 2026, and has not been independently confirmed.

Ransomware.live reports that Panzer claims to have targeted Indonesian renewable-energy company Supreme Energy. The claim was published on October 9, 2026, and has not been independently confirmed.

The ransomware group Chaos reportedly claimed to publish 1,500 GB of Astrana Health patient data and diagnoses. The monitoring post says the claim is unverified.
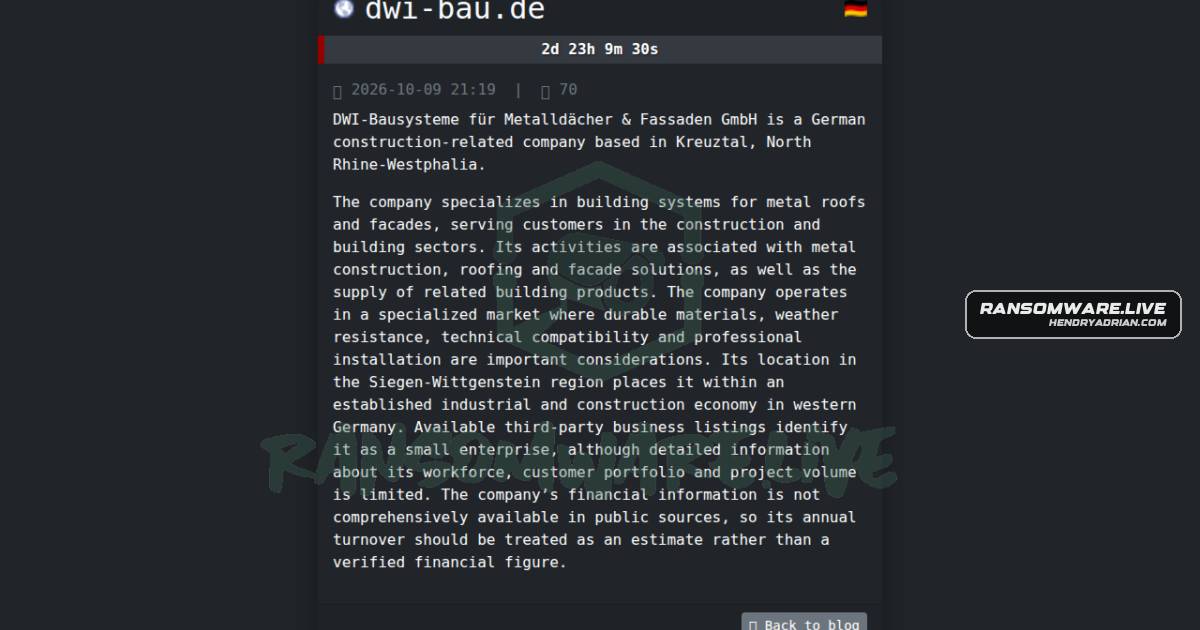
Ransomware group SafePay claimed it targeted German building systems company DWI-Bau. The claim was published on October 9, 2026, and has not been independently confirmed.
Ransomware.live lists Hotel Delfino Lugano in Switzerland as a SafePay ransomware claim dated October 9, 2026. The post says operations were disrupted and extortion demands made, but notes the claims are unverified.

Ransomware group Deadlock claims to have leaked data from Italian pharmaceutical company idi pharma, including proprietary formulations and dosage technology. The claim has not been independently confirmed.
Ransomware group Deadlock claimed Saber1, a US supplier of machine vision components and industrial cameras, as a victim. The claim has not been independently confirmed.