
Ransomhouse Claims to Have Targeted Namibia’s Defence Force
Ransomhouse claims it compromised the Namibian Defence Force’s systems and sought a ransom. The post attributes the claim to the group and says it cannot confirm its accuracy.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2774 articles
Ransomhouse claims it compromised the Namibian Defence Force’s systems and sought a ransom. The post attributes the claim to the group and says it cannot confirm its accuracy.
Safepay claims it attacked Swiss kitchen company Stöcklin Küchen. The monitoring post lists the claim’s source and September 15, 2026 publication and discovery times, but says it cannot confirm the claim.
A ransomware.live monitoring record says Safepay publicly listed meterex.com, a technology company in Germany. The publisher says it cannot confirm the claim.
Ransomware.live recorded a SafePay claim targeting laconcepcion[.]com[.]mx in Mexico, published September 15, 2026. The site says it could not confirm the claim.
A ransomware.live monitoring post attributes a claimed attack on US healthcare organization triniticaring.org to Safepay and reports operational disruption. The post says the group’s claims are unconfirmed.

A ransomware.live post attributes a ransomware claim against UK optometry practice Owen Leigh Optometry to DragonForce, which claimed more than 400 GB of data loss. The post says the claim is unconfirmed.

A ransomware.live monitoring post says DragonForce claimed a ransomware incident affecting Community Property Management and reported 200+ GB of data impact. The claim is unverified.
Ransomware.live reports that Qilin claimed an attack on Swedish manufacturer Aarsleff on September 16, 2026, with disruption and possible data encryption. The claim is unconfirmed.
SafePay claimed Neumerkel GmbH in Germany as a ransomware victim on Sept. 15, 2026. The monitoring post says it cannot verify the claim.
A ransomware group identified as Safepay claimed an attack on Marlin HVAC, listed as marlinhvac[.]com. The monitoring post gives September 15, 2026, as the discovery and publication date and says the claim is unconfirmed.

A ransomware.live post reports Vexy Ransomware’s claim that it encrypted critical IT systems at Japanese company Hashimoto Jimuki, disrupting operations. The claim has not been independently confirmed.
Dark Project claims it stole 489 GB of data from Cumar Marble & Granite, including personal information, technical drawings and financial documents. The report says the claims are unconfirmed.
Interlock claims it compromised Fort Smith and leaked 5.6 TB of data, including public safety, infrastructure, law enforcement, and resident information. The claims have not been independently confirmed.
Ransomware.live reported a metaencryptor claim targeting South Korean manufacturer SFA Engineering Corporation, with disruption reported. The post is based on the group’s public claim, which the publisher could not verify.
A ransomware.live monitoring post says Qilin claimed ADM as a victim on September 15, 2026. The post attributes the claim to the group and says it could not confirm its accuracy; attack details and outcomes were not provided.
A ransomware.live post attributes an incident involving encryption-related impacts at US-based Winston Contracting to Qilin. The post says the claims are unverified.
A ransomware-monitoring post records Anubis’s claim of a data breach at Better Accounting Solutions, but says the claim could not be confirmed.
Ransomware.live reports that Qilin claimed an attack on Geieg in Spain, with encrypted or disrupted data and ransom demands. The post says the group's claims are unconfirmed.

Ransomware group ShadowByt3$ claims it obtained sensitive HandyTrac data and demands negotiation within 72 hours to prevent a leak. The post says the claims are unverified.
The group iah6477 claimed responsibility for a ransomware incident involving about 1.9 TiB of Veritiv data. The monitoring post says the claim could not be confirmed.
A ransomware.live record says Panzer targeted Honda Peru and claims the attack disrupted operations and data access. The post says the group’s claims are unconfirmed.
Qilin claimed it targeted US manufacturer Foremost Mfg; the monitoring post reports system and data disruption but says the claim could not be confirmed.
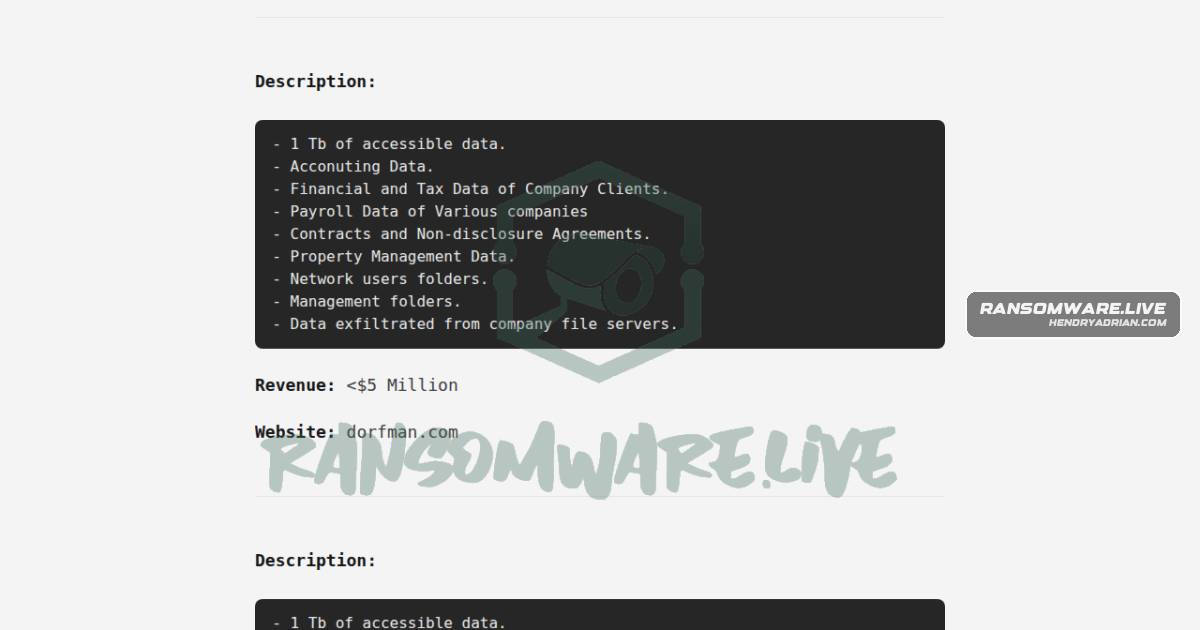
Ransomware.live recorded an unverified Genesis claim targeting US CPA firm Dorfman Abrams Music, P.C. The claim was published September 13, 2026, and discovered September 14.
The ransomware group unsafe claimed an attack on geekybunch[.]com and cited $5 million in lost revenue. The monitoring post says the claim is unconfirmed.