
Scanner-Evading JavaScript Campaign Targets 953 Online Stores, Mostly Magento
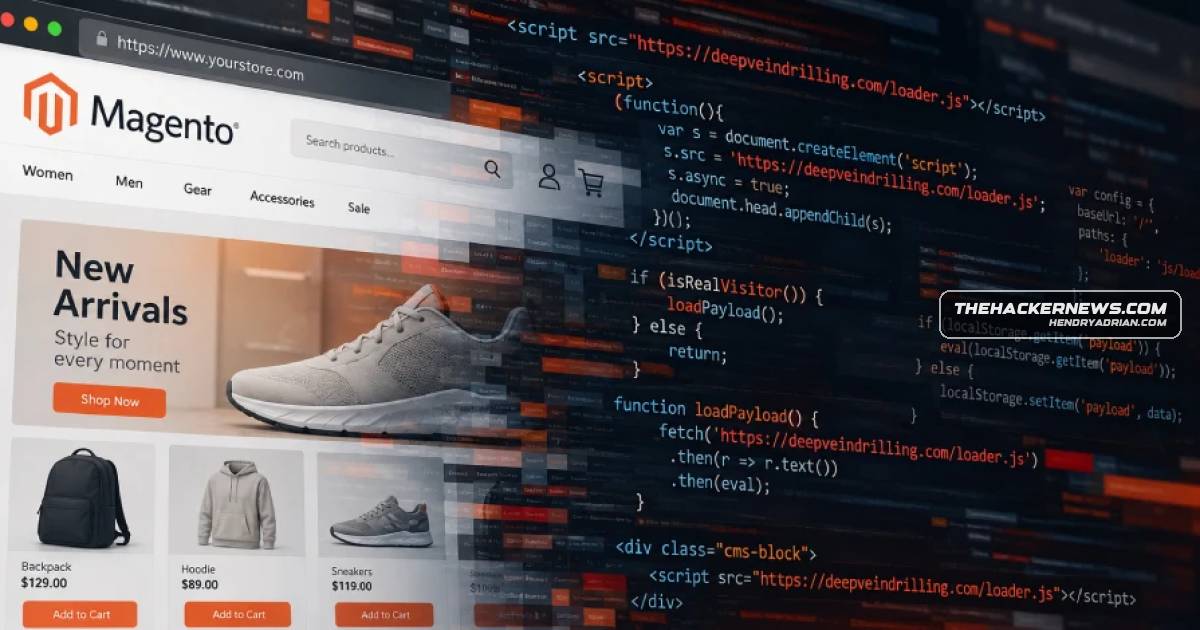
Summary
Sansec reports that a campaign active since July 2025 has infected 953 online stores, mostly Magento, with JavaScript loaders that filter out scanners. The final payload is unknown.
Key points
- Sansec found the loader in Magento CMS blocks; it checks whether a visitor appears to be a real shopper before serving code.
- One loader version stores payload code in browser localStorage; another adds browser fingerprinting to filter bots and scanners. The final payload is unknown.
- Sansec observed deepveindrilling[.]com in CMS blocks on 83 stores since the domain was registered on October 6, 2026.
- Sansec estimates 471 stores were injected through PolyShell (CVE-2026-48356); another 102 had files uploaded through PolyShell or SessionReaper (CVE-2025-54236).
- An earlier campaign version used Keitaro as a traffic distribution system; the latest loader integrates bot-filtering logic itself.
- Sansec recommends checking for suspicious accounts and unexpected CMS blocks or pages, keeping stores updated, and enforcing strong passwords.
- Separately, researcher Adel Karimi recorded what appeared to be successful PHP2Shell exploitation to run shell commands on honeypots; no downloaded second-stage artifacts were observed.
Article Details
- Event Type
- Long-running campaign infecting online stores with malicious JavaScript loaders, alongside reported exploitation of PHP vulnerabilities.
- Impact
- Sansec reported 953 infected online stores, mostly running Magento. The loaders expose store visitors to attacker-controlled code, but the final payload is unknown. Separately, successful exploitation of the PHP vulnerabilities was observed on honeypot servers to run shell commands and fetch additional payloads; no second-stage artifacts were observed.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | additionalver[.]com | Identified as an attacker domain serving a JavaScript loader associated with the campaign. |
| DOMAIN | deepveindrilling[.]com | Sansec found this campaign domain in CMS blocks on 83 online stores; it served the malicious JavaScript loader. |
| IPV4 | 162[.]35[.]99[.]94 | Remote server observed being contacted to fetch additional payloads during successful PHP vulnerability exploitation on honeypot servers. |
MITRE ATT&CK
T1059.007 · JavaScriptThe campaign used malicious JavaScript loaders embedded in Magento CMS blocks and served to visitors.T1189 · Drive-by CompromiseVisitors to compromised online stores could receive and run malicious code when the affected page was opened.T1190 · Exploit Public-Facing ApplicationThe article reports exploitation of Magento and PHP vulnerabilities to upload files or inject malicious code into internet-facing stores and servers.T1505.003 · Web ShellA Magento store was reported to contain PolyShell webshells disguised as PNG images.
CVE
CVE-2025-54236vulnerability. Another 102 stores saw files uploaded through the PolyShell or SessionReaper (aka CVE-2025-54236) vulnerabilities.CVE-2026-109618The disclosure comes against the backdrop of PHP2Shell, a set of two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) that have witnessed widespread exploitation attempts following their disclosureCVE-2026-109619against the backdrop of PHP2Shell, a set of two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) that have witnessed widespread exploitation attempts following their disclosure last week.CVE-2026-48356471 Magento stores are estimated to have been injected with the loader through the PolyShell (aka CVE-2026-48356) vulnerability. Another 102 stores saw files uploaded through the PolyShell or SessionReaper (aka
People
Vendors
Products
Keitaro TrackerEarly iterations of the campaign have also been observed using Keitaro, an advertising tracker and analytics platform, as a traffic distribution system (TDS), to route visitors to different responses – i.e., return aMagentoAn unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025.PHPThe disclosure comes against the backdrop of PHP2Shell, a set of two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) that have witnessed widespread exploitation attempts following their disclosure