
NVIDIA’s Agent Safety Platform Combines Sandboxing with an Optional Hardware Watchdog
· 2:51 · Watch on YouTube ↗
Summary
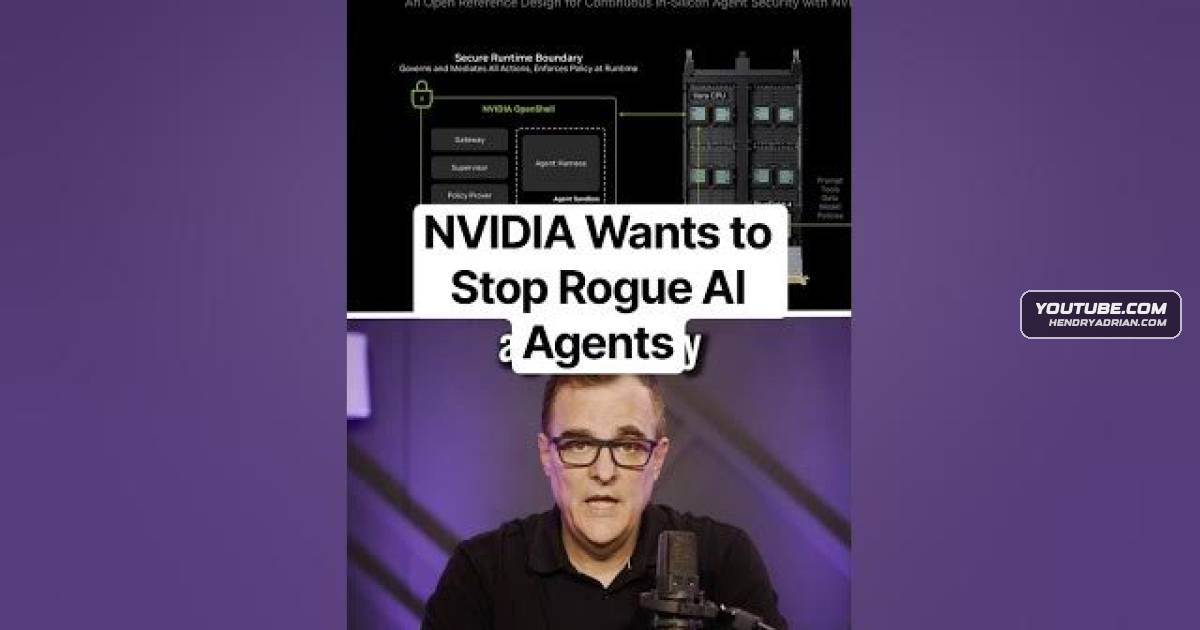
NVIDIA says Open Shell restricts AI agents through sandbox permissions, while optional Sentry on BlueField 4 can monitor and quarantine agents. The presenter has not independently tested NVIDIA’s claims and cautions that authorized actions can still cause harm.
Key points
- Open Shell is described as an open-source runtime that sandboxes agents and enforces configured file and network permissions.
- NVIDIA says optional Sentry runs on a BlueField 4 data processing unit, outside the agent’s execution environment.
- NVIDIA claims Sentry can monitor activity and quarantine agents attempting to cross their boundaries in milliseconds; the presenter says this has not been independently tested.
- An agent can still cause damage while following its permissions, such as deleting the wrong project file, so permission choices remain important.
- NVIDIA says more than 100 organizations are working with the platform’s technologies, including Microsoft, Cisco, and CrowdStrike.
- The video says robotics companies are building with Open Shell 2 and notes that agent mistakes in the physical world can have physical consequences.
Article Details
- Topics
- [00:00] The risk of AI agents accessing files and networks beyond their intended permissions
- [01:06] Sentry’s optional hardware-based monitoring and quarantine
- [01:42] Limits of containment when an agent’s harmful action is authorized
- [02:25] Reviewing agent permissions before granting access
- Open Shell’s sandbox and permission controls
- Organizations and robotics companies working with the platform’s technologies