
Sysdig shows AI agents tracing 2,731 vulnerability findings to one approved fix
Summary
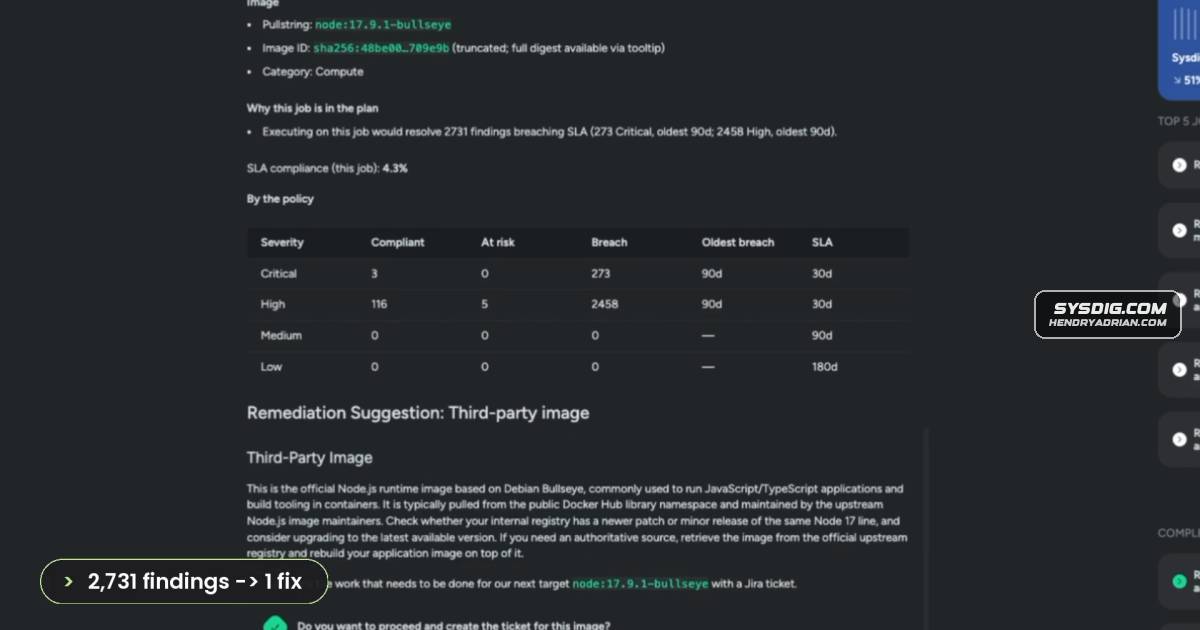
In a Sysdig demo, Secure AI agents grouped 2,731 SLA-breaching findings in a Node.js base image into one proposed fix, then routed a Jira ticket for human approval. Sysdig says the workflow is also available through its MCP server in Claude.
Key points
- In a live demonstration, Sysdig says its agents triaged 119,443 findings and traced 2,731 SLA-breaching findings to one Node.js base-image remediation.
- The image, node:17.9.1-bullseye, had 273 critical findings; the oldest was 90 days past its SLA deadline.
- The demonstrated SLA Compliance plan prioritized findings with published fixes; other workflows use runtime reachability, exploitability signals, EPSS probability, and CISA KEV status.
- A human reviewed and approved the proposed remediation before Sysdig Secure AI created Jira ticket DEJI-342.
- Sysdig says its MCP server exposes the workflow to Claude and other compatible assistants, with scoped tool permissions and explicit approval required before remediation changes.
- The vendor says the remediation skill will not commit or push to repositories, expose credentials, or make changes without approval.
Article Details
- Event Type
- Demonstration of agentic vulnerability-management capabilities in Sysdig Secure AI
- Impact
- In a live demo, Sysdig Secure AI triaged 119,443 findings and traced 2,731 SLA-breaching findings in a Node.js base image to one proposed fix. A human approved the remediation before Jira ticket DEJI-342 was created. Sysdig says the workflow uses runtime reachability, exploitability signals, EPSS probability, and CISA KEV status to prioritize findings. The article's cost and throughput figures are attributed to Sysdig internal analysis.
CVE
CVE-2026-32740strukturag · libheif[CVE identifiers ] vulnerable packages/critical findings – CVE-2026-55200, CVE-2026-32740, and 2 more CVEs mentioned in the Claude query/results.CVE-2026-55200Libssh2 · Libssh2[CVE identifiers ] vulnerable packages/critical findings – CVE-2026-55200, CVE-2026-32740, and 2 more CVEs mentioned in the Claude query/results.
Vendors
Products
ClaudeThe same capability also runs headless in Claude via the Sysdig MCP server, using runtime data to prioritize issues by exploitability, KEV status, and reachability.Jirafindings in a Node.js base image to one fix, and route the remediation through human approval into Jira ticket DEJI-342.Node.jscloud security to continuously triage vulnerability backlogs, trace 2,731 SLA-breaching findings in a Node.js base image to one fix, and route the remediation through human approval into Jira ticket DEJI-342.Sysdig MCP serverThe same capability also runs headless in Claude via the Sysdig MCP server, using runtime data to prioritize issues by exploitability, KEV status, and reachability.Sysdig Secure AISysdig Secure AI uses agentic cloud security to continuously triage vulnerability backlogs, trace 2,731 SLA-breaching findings in a Node.js base image to one fix, and route the remediation through human approval into
Tools
List Vulnerability Findings[T1059 ] Command and Scripting Interpreter – The headless workflow operates through Claude and tool calls via MCP, enabling assistant-driven actions (‘Allow Claude to use List Vulnerability Findings’).Sysdig RemediateSay yes to remediation and the agent launches the Sysdig Remediate skill.