
CERT-AGID Disrupts ARERA-Impersonation Phishing Campaign Using Water Bonus Lure
Summary
CERT-AGID reports taking down a typosquatted site impersonating ARERA. The site used a fake water-bonus refund to solicit phone numbers and payment-card details; campaign indicators were shared with accredited organizations.
Key points
- The site copied ARERA’s name and logo and used typosquatting to appear legitimate.
- The phishing lure claimed users could receive a refund linked to the water social bonus.
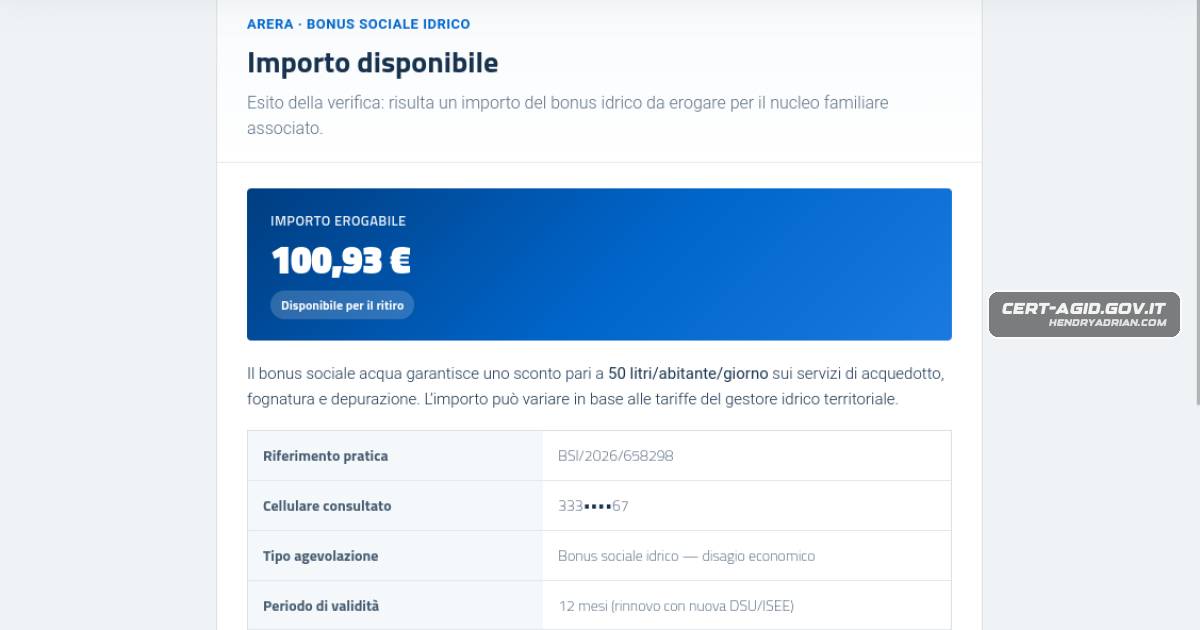
- The site requested a phone number, then displayed a fake €100.93 payment amount.
- A subsequent page solicited the cardholder’s name, card number, expiration date and CVV.
- CERT-AGID reports securing the malicious domain’s takedown and notifying the relevant organization.
- Campaign indicators were distributed through the CERT-AGID feed to accredited organizations.
Article Details
- Event Type
- Phishing campaign impersonating ARERA and using a fake water social bonus refund to solicit personal and payment details.
- Impact
- The fraudulent site requested users’ phone numbers, cardholder names, card numbers, expiration dates, and CVVs. The article does not confirm that data was successfully collected. CERT-AGID secured the site’s takedown and distributed campaign indicators to accredited organizations.
MITRE ATT&CK
T1036 · MasqueradingThe fraudulent site copied ARERA’s name and logo to appear legitimate.T1056 · Input CaptureThe site used forms to solicit phone numbers and payment-card details.T1566.002 · Spearphishing LinkUsers were directed through deceptive web pages designed to capture sensitive information.T1583.001 · DomainsThe campaign used a malicious domain to host fake ARERA pages; CERT-AGID secured its takedown.T1621 · Multi-Factor Authentication Request GenerationThe article identifies the purported card-verification step as Multi-Factor Authentication Request Generation; the page requested payment-card details under the pretext of processing a payout.