
CERT-AGID Finds AI Document Checks and Visual Instruction Flaw in INPS Phishing Site
Summary
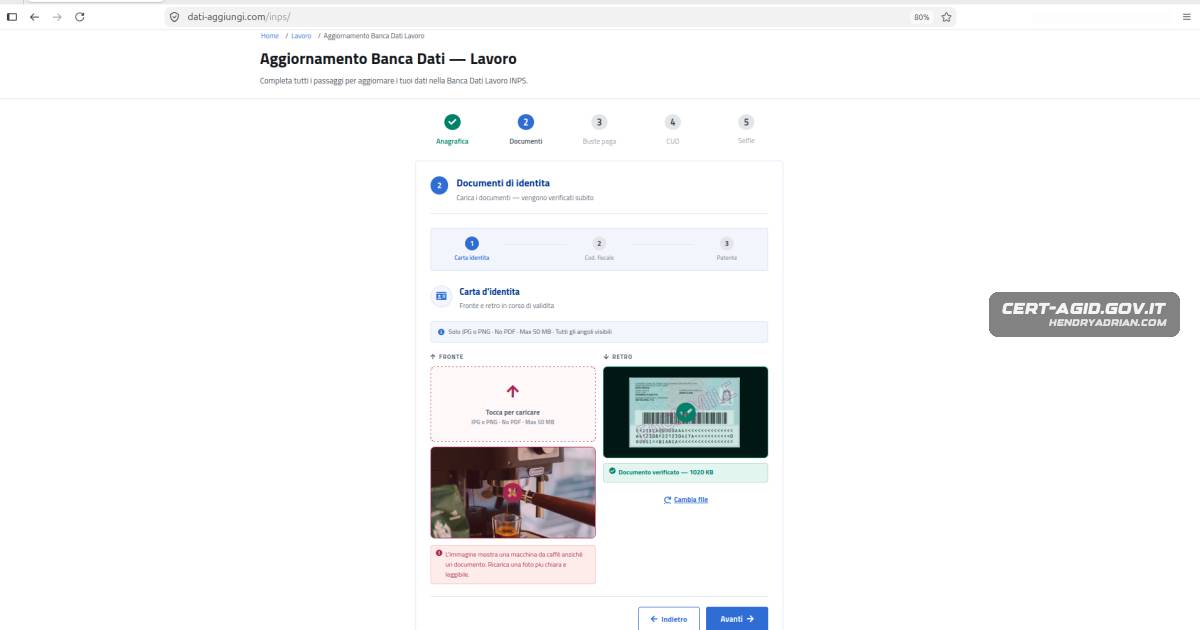
CERT-AGID analyzed an INPS-themed phishing site that used AI to check uploaded documents. Tests found it accepted a fake ID and that instructions embedded in images could affect its responses; takedown procedures were initiated.
Key points
- Fraudulent SMS messages impersonated INPS and directed recipients to a counterfeit site with a five-step flow requesting personal details, identity documents, pay slips, CUD forms, and selfies.
- CERT-AGID found the site used an AI-based image-validation component that identified itself as Gemini 1.5 PRO.
- In tests, the system described and rejected some irrelevant images but accepted an evidently fake identity card marked “FACSIMILE.”
- The upload_ajax.php endpoint returned structured validation responses; rejection reasons were exposed in a public error field.
- Further tests showed that text embedded in images could affect the system’s responses, indicating a failure to separate untrusted visual content from control instructions.
- CERT-AGID activated takedown procedures, informed the relevant public body, and distributed campaign indicators to accredited organizations.
Article Details
- Attack Vectors
- Fraudulent SMS messages impersonating INPS direct recipients to a counterfeit website.
- The site uses a guided five-step submission flow to collect personal details, identity documents, pay slips, CUD forms, and selfies.
- An AI-based file-validation component checks uploaded images and documents, sometimes rejecting irrelevant uploads but also accepting invalid documents.
- Defensive Notes
- CERT-AGID activated takedown procedures for identified malicious domains and informed the relevant public body.
- CERT-AGID distributed campaign indicators through its feed to accredited organizations.
MITRE ATT&CK
T1056.003 · Web Portal CaptureThe counterfeit web portal collects personal details and uploaded identity and payroll documents through a multi-step form.T1204.001 · Malicious LinkThe attack relies on recipients clicking the SMS link and proceeding through the counterfeit site's upload flow.T1566.002 · Spearphishing LinkThe campaign sends fraudulent SMS messages containing a link to a counterfeit INPS website.