
Spacebears Claims SEARS (Grupo Sanborns) as a Ransomware Target
Summary
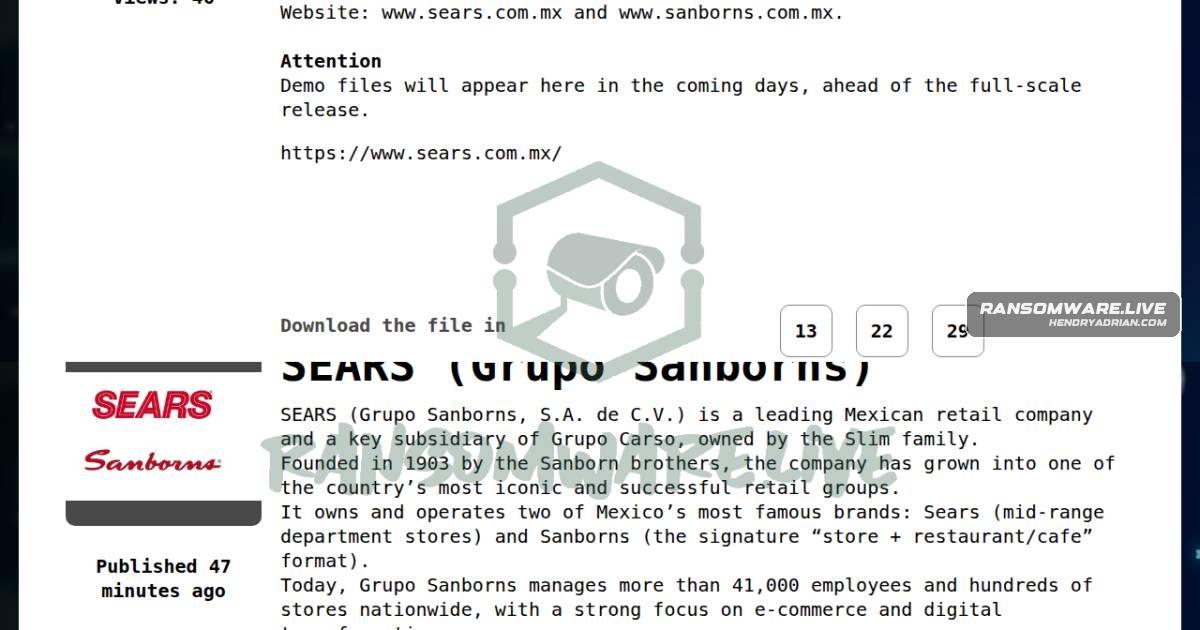
A ransomware.live record says spacebears claimed SEARS (Grupo Sanborns) in Mexico as a target. It anticipates “AttentionDemo” files ahead of a full release; the claim is unconfirmed.
Key points
- The record names SEARS (Grupo Sanborns) as the claimed victim and spacebears as the ransomware actor.
- The claim is attributed to the actor’s listing and monitored by ransomware.live; the article says it cannot confirm the claim’s accuracy.
- The post says “AttentionDemo” files are expected before a full-scale release; it does not report that files have appeared.
- The record gives August 15, 2026 as the discovery and publication date.
Article Details
- Victim
- SEARS (Grupo Sanborns)
- Claim Date
- 2026-08-15
- Encryption Status
- Unknown; the source reports a ransomware-group claim but does not confirm encryption.
- Exfiltration Status
- Unknown; the source does not report whether data was exfiltrated.
- Leak Status
- The group reportedly expected to publish “AttentionDemo” files before a full-scale release; the source does not confirm that any files were published.