
xpl0itrs Claims Ransomware Attack on Dynatrace
Summary
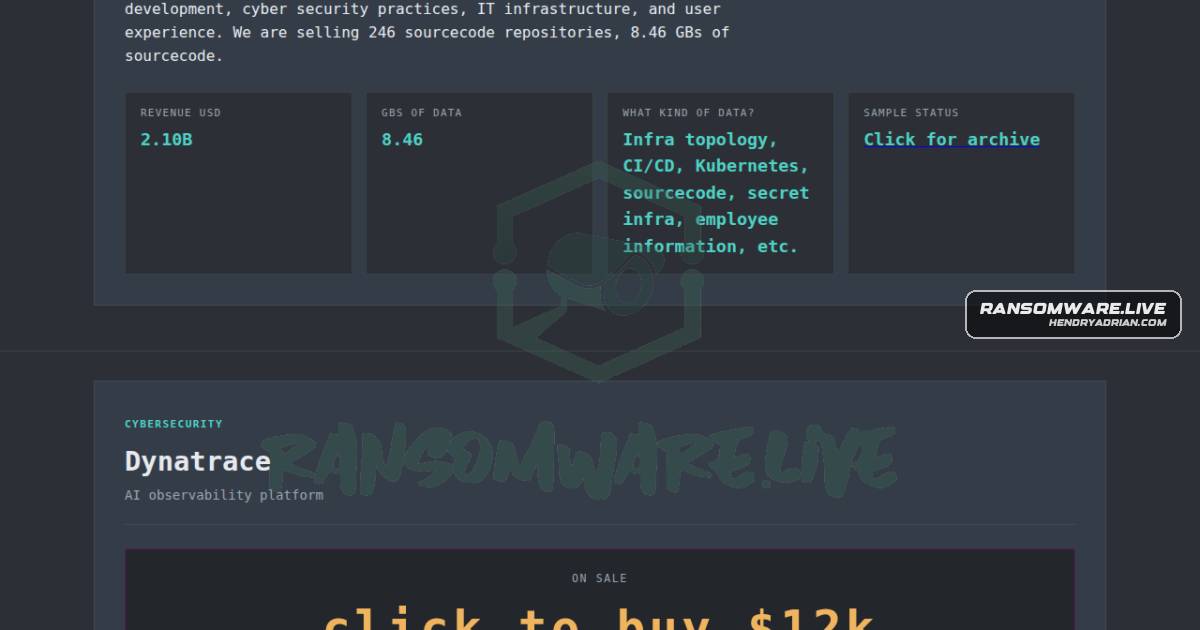
Ransomware group xpl0itrs reportedly claimed Dynatrace as a victim; the post says the alleged incident affected systems and availability in Austria. The publisher says the claim is unconfirmed.
Key points
- The record names Dynatrace as the victim and xpl0itrs as the ransomware actor.
- The claim is attributed to an xpl0itrs leak-site listing and monitored by ransomware.live.
- The post alleges effects on Dynatrace systems and availability in Austria.
- The publisher says it cannot confirm the claim's accuracy.
Article Details
- Victim
- Dynatrace
- Encryption Status
- Unknown; ransomware targeting is reported, but encryption is not confirmed.
- Exfiltration Status
- Unknown
- Leak Status
- Unverified group claim; no leak or publication status is reported.