
xpl0itrs Claims RapidFort as a Ransomware Victim
Summary
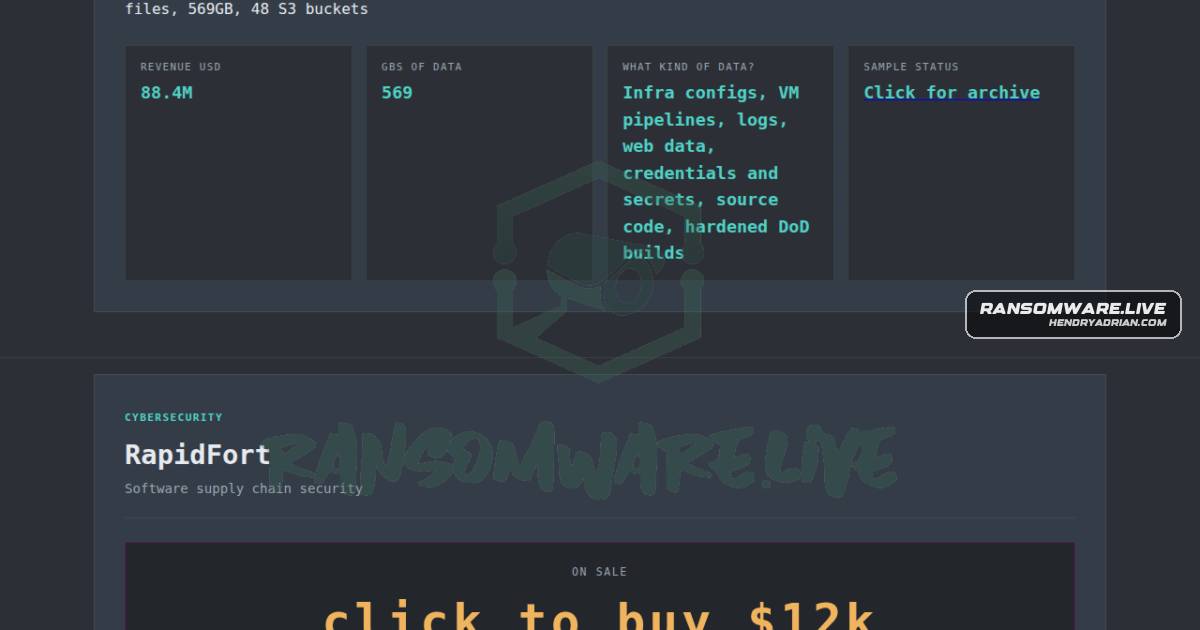
Ransomware.live reports that the xpl0itrs group claimed RapidFort as a victim. The claim is unconfirmed; the article says it cannot verify the group's statement.
Key points
- The named victim is RapidFort, a US technology organization.
- The claim is attributed to the xpl0itrs ransomware group and a leak-site listing.
- The article states that the claim is unconfirmed; it provides no independent evidence of compromise.
Article Details
- Victim
- RapidFort
- Victim Domain
- Unknown
- Attack Date
- 2026-08-15
- Claim Date
- 2026-08-15
- Encryption Status
- Unknown; the source does not state whether systems were encrypted.
- Encrypted Size
- Unknown
- Exfiltration Status
- Unknown; the source does not state whether data was exfiltrated.
- Exfiltrated Data
- Unknown
- Exfiltrated Size
- Unknown
- Ransom Demand
- Unknown
- Leak Status
- xpl0itrs claimed RapidFort; the source does not confirm that data was published or that any alleged data is authentic.