
Eclipse Claims Moscord as a Ransomware Victim
Summary
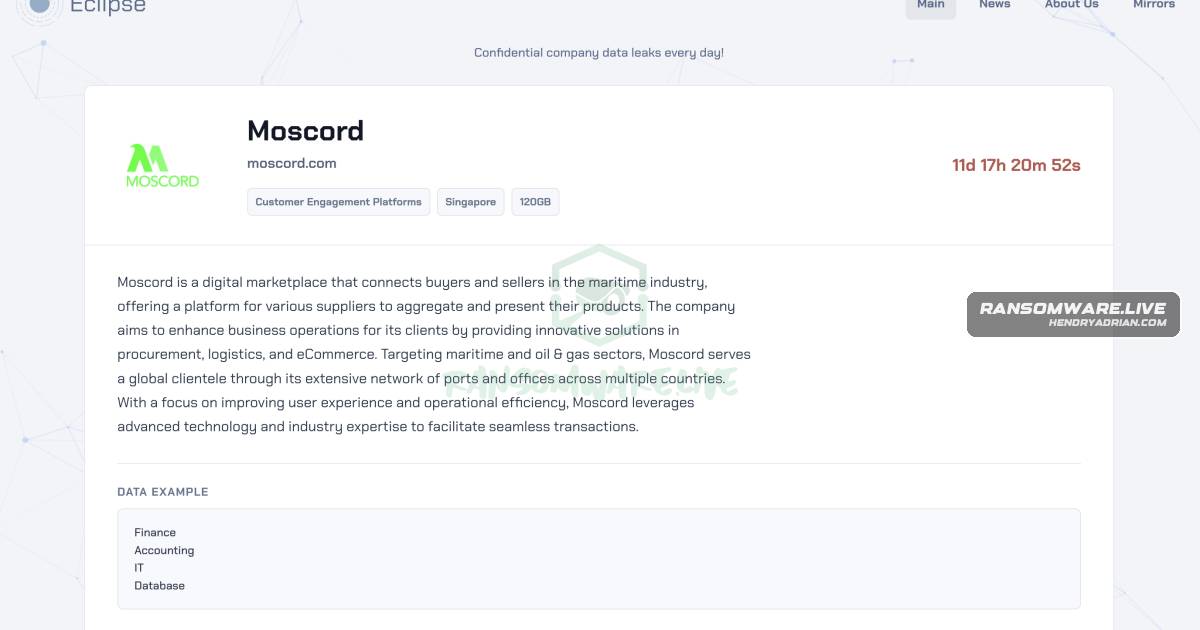
A ransomware.live record attributes an unconfirmed ransomware claim naming maritime marketplace Moscord to the Eclipse group and links to the group's leak site.
Key points
- The record names Moscord as the victim and Eclipse as the ransomware actor.
- It attributes the claim to Eclipse and links to the group's leak site; ransomware.live says it monitored the record.
- The post says the claim is unconfirmed and offers to share an official statement from Moscord.
- The supplied content does not establish whether Moscord was compromised or what, if anything, was affected.
Article Details
- Victim
- Moscord
- Victim Domain
- Not disclosed
- Claim Date
- 2026-08-14
- Encryption Status
- Unknown
- Encrypted Size
- Not disclosed
- Exfiltration Status
- Unknown
- Exfiltrated Data
- Not disclosed
- Exfiltrated Size
- Not disclosed
- Ransom Demand
- Not disclosed
- Leak Status
- An Eclipse listing was published; the source says the group's claims are unconfirmed. Victim confirmation and the authenticity of any leaked data are not established.