
DireWolf Claims PayUp as a Ransomware Target
Summary
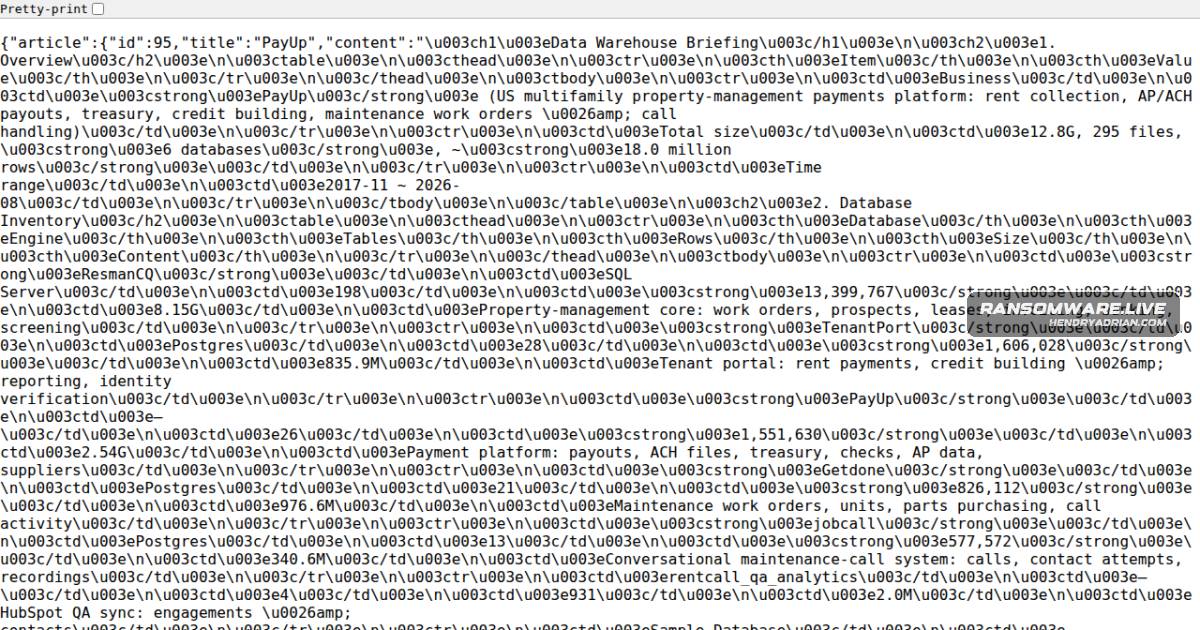
A ransomware.live monitoring post attributes a claim targeting financial software company PayUp to the DireWolf ransomware group. The post says the claim is unconfirmed.
Key points
- The post names PayUp, a financial software company, as the claimed victim and DireWolf as the ransomware actor.
- The post alleges disruption and data-encryption demands, but does not independently verify them.
- The claim is attributed to DireWolf and the post is identified as monitored by ransomware.live; no official statement from PayUp is included.
Article Details
- Victim
- PayUp
- Victim Domain
- Not disclosed
- Encryption Status
- Unconfirmed; the article mentions data-encryption demands but says the information is based on unverified group claims.
- Encrypted Size
- Not disclosed
- Exfiltration Status
- Unknown
- Exfiltrated Data
- None reported
- Exfiltrated Size
- Not disclosed
- Ransom Demand
- Unconfirmed; the article mentions data-encryption demands but does not provide an amount.
- Leak Status
- Unknown