
Huntress Reports 155-Fold Surge in Password Spraying, Citing LSHIY Campaign
Summary
Huntress reported password-spraying activity rose 155-fold in H1 2026, including an LSHIY campaign abusing Azure CLI’s legacy ROPC flow where Conditional Access left MFA gaps. It observed 78 compromised accounts but no post-login activity.
Key points
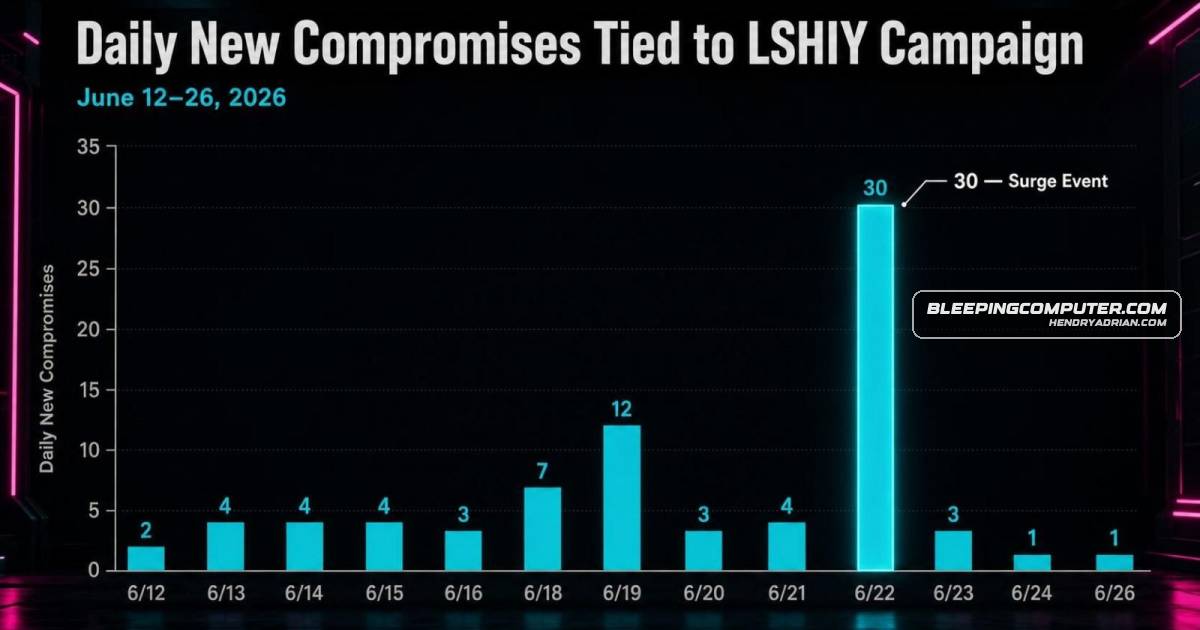
- Huntress reported a 155-fold rise in password-spraying attacks in the first half of 2026; in a two-week period in June, it observed more than 81 million related login attempts and 78 account compromises.
- The LSHIY campaign targeted Azure CLI and Entra resources, reusing valid username-and-password pairs from earlier breaches.
- The campaign abused legacy Resource Owner Password Credentials (ROPC), which sends credentials directly to the /token endpoint without an interactive MFA prompt.
- Huntress analyzed 23 affected businesses: eight had no MFA, while the other 15 had MFA policies that did not cover the attackers’ sign-in attempts.
- The activity originated from LSHIY’s IPv6 BYOIP range, then shifted to IPv6 ranges hosted by FranTech and IPv4 activity from 3xK Tech. LSHIY later terminated the original activity and confirmed the attacker used its BYOIP offering.
- Huntress observed no post-compromise activity after the successful logins. A Huntress product manager speculated that credentials may have been validated for resale.
- Recommended measures include disabling ROPC, applying MFA across users and cloud apps, restricting Azure CLI access, and prioritizing response based on credential validity rather than spray volume.
Article Details
- Event Type
- Password-spraying campaign exploiting legacy ROPC authentication and gaps in MFA policy coverage.
- Impact
- Huntress reported a 155x increase in password-spraying attacks in the first half of 2026. In a two-week period in mid-June, it observed more than 81 million related login attempts and 78 account compromises. Huntress observed no post-compromise activity tied to the LSHIY campaign; Rich Mozeleski suspected the attacker may have been validating credentials for resale. LSHIY later terminated activity from the original IP range.
MITRE ATT&CK
Vendors
3xK TechSubsequent activity appeared from 3xK Tech using IPv4.FranTechAfter LSHIY shut down the original activity, the spray attempts first shifted to FranTech-hosted IPv6 ranges.LSHIY LLCThe traffic originated from an IPv6 range controlled by internet hosting provider LSHIY LLC.MicrosoftHuntress reported a 155x surge in password spraying during the first half of 2026, driven in part by the LSHIY campaign targeting Microsoft Azure CLI and abusing legacy ROPC authentication.
Products
AzureHuntress reported a 155x surge in password spraying during the first half of 2026, driven in part by the LSHIY campaign targeting Microsoft Azure CLI and abusing legacy ROPC authentication.Azure CLIHuntress reported a 155x surge in password spraying during the first half of 2026, driven in part by the LSHIY campaign targeting Microsoft Azure CLI and abusing legacy ROPC authentication.Conditional AccessThe attacks used IPv6 BYOIP infrastructure, exposed gaps in Conditional Access coverage, and succeeded where MFA did not apply to the specific sign-in flow.Entra#LSHIY