
Hunt.io Attributes 14,530 Dahua Device Compromises to Operation CameraSwarm
Summary
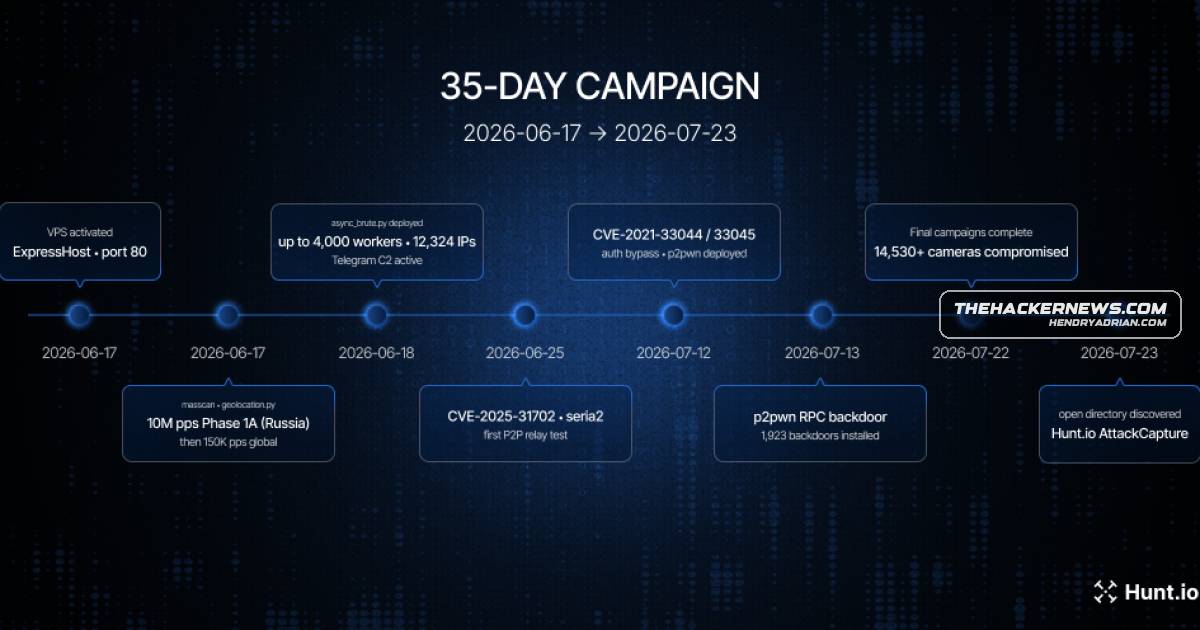
Hunt.io says Operation CameraSwarm compromised 14,530+ Dahua devices using credential attacks, two authentication-bypass flaws and P2P relays. Public sources support the underlying mechanisms but do not independently verify the campaign totals.
Key points
- Hunt.io attributes more than 14,530 device compromises between June 17 and July 22, 2026, to the campaign; the totals remain unverified independently.
- Hunt.io reports 12,324 IP addresses across 13,229 credential-attack records, 1,923 cameras reached using CVE-2021-33044 and CVE-2021-33045, and 283 reached through P2P.
- The two authentication-bypass vulnerabilities remain listed in CISA’s KEV catalog as of August 19, 2026; Dahua advises installing fixed software or newer firmware.
- A Dahua serial number could reportedly establish an Easy4IP relay path to devices behind NAT on firmware predating mid-2024; device-level authentication may still be required.
- Hunt.io says recovered operator code recorded 89.4% of live serial numbers returning an open channel without authentication; that campaign-specific figure has not been independently reproduced.
- Researchers described the operator as Russian-speaking based on language artifacts, but did not attribute the activity to a named threat actor or government.
- Defenders are advised to update firmware, disable unnecessary P2P, use strong unique credentials, remove unused accounts and segment surveillance systems.
Article Details
- Event Type
- Reported campaign compromising Dahua devices through credential attacks, authentication-bypass vulnerabilities, and P2P relay abuse.
- Impact
- Hunt.io attributes more than 14,530 device compromises to the campaign: 12,324 unique IP addresses across 13,229 credential-attack records, 1,923 cameras reached through CVE-2021-33044 and CVE-2021-33045, and 283 devices reached through the P2P path, including devices behind NAT. Hunt.io's campaign totals and related claims have not been independently confirmed. The activity could expose cameras and network video recorders to unauthorized access; recommended mitigations include applying fixed firmware, disabling unnecessary P2P access, and securing credentials and accounts.
CVE
CVE-2021-33044Hunt.io uncovered Operation CameraSwarm, a campaign that compromised more than 14,530 Dahua devices by combining credential attacks, CVE-2021-33044, CVE-2021-33045, and a P2P relay method.CVE-2021-33045Hunt.io uncovered Operation CameraSwarm, a campaign that compromised more than 14,530 Dahua devices by combining credential attacks, CVE-2021-33044, CVE-2021-33045, and a P2P relay method.
People
Vendors
Products
Easy4IPThe recovered tooling and logs suggested concentrated activity in Ukraine and Russia, while defenders are urged to update firmware, disable unnecessary P2P access, and review Easy4IP exposure.Easy4IPCloudThe dh-p2p proof-of-concept repository also shows that the Dahua P2P protocol locates a device through Easy4IPCloud using its serial number and can establish a tunnel to the camera or network video recorder.
Tools
dh-p2pThe dh-p2p proof-of-concept repository also shows that the Dahua P2P protocol locates a device through Easy4IPCloud using its serial number and can establish a tunnel to the camera or network video recorder.p2pwnAs of August 19, 2026, the public p2pwn repository remains accessible and independently confirms that the tool accepts Dahua serial numbers as input, checks CVE-2021-33044 and CVE-2021-33045, and contains a default
Countries
RussiaThe recovered tooling and logs suggested concentrated activity in Ukraine and Russia, while defenders are urged to update firmware, disable unnecessary P2P access, and review Easy4IP exposure.UkraineThe recovered tooling and logs suggested concentrated activity in Ukraine and Russia, while defenders are urged to update firmware, disable unnecessary P2P access, and review Easy4IP exposure.