
Helix Claims Delek US Is Listed as a Ransomware Victim
Summary
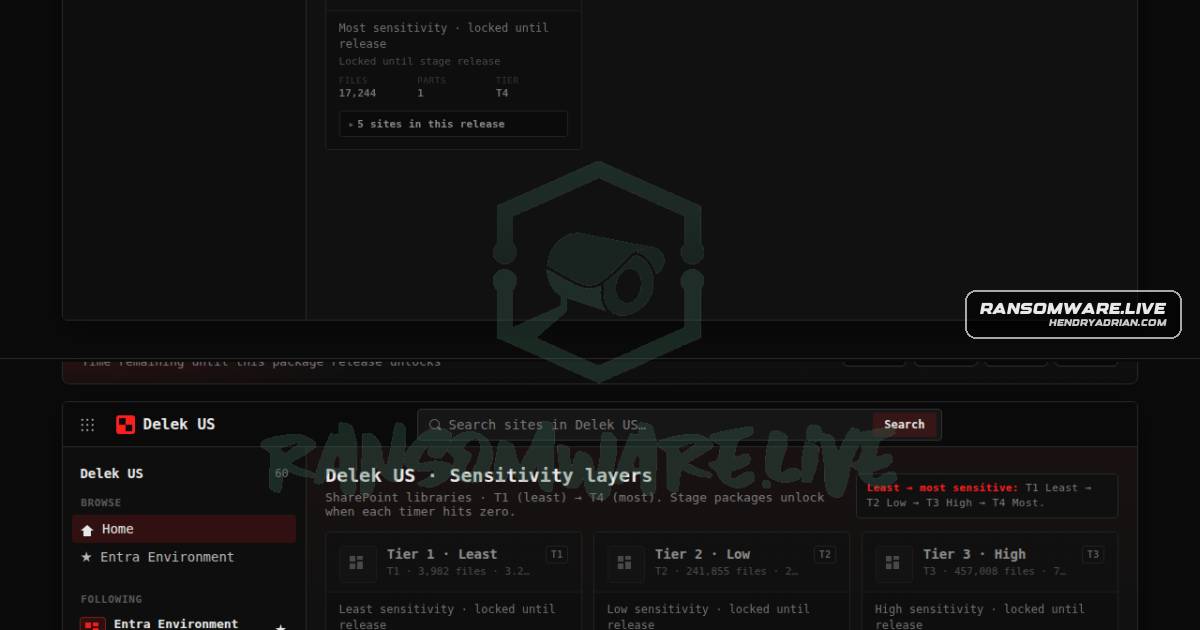
Ransomware.live lists Delek US in a Helix ransomware claim; the post says the victim is “live” and describes tiered unlock timing. The site says the claim is unconfirmed.
Key points
- The record names Delek US as the victim and Helix as the ransomware actor.
- The claim is attributed to Helix’s leak site and marked as monitored by ransomware.live.
- The post says Delek US is “live” and that T1 unlocks in 12 hours, with subsequent tiers unlocking every 24 hours.
- The publisher says it cannot confirm the group’s claims.
Article Details
- Victim
- Delek US
- Victim Domain
- Unknown
- Claim Date
- 2026-08-19
- Encryption Status
- Unknown
- Encrypted Size
- Unknown
- Exfiltration Status
- Unknown
- Exfiltrated Data
- Unknown
- Exfiltrated Size
- Unknown
- Ransom Demand
- Unknown
- Leak Status
- Helix's listing says Delek US is live; the source says the claim could not be confirmed. No data publication is confirmed.