
Titan ransomware group claims attack on Italy’s ELCON MEGARAD
Summary
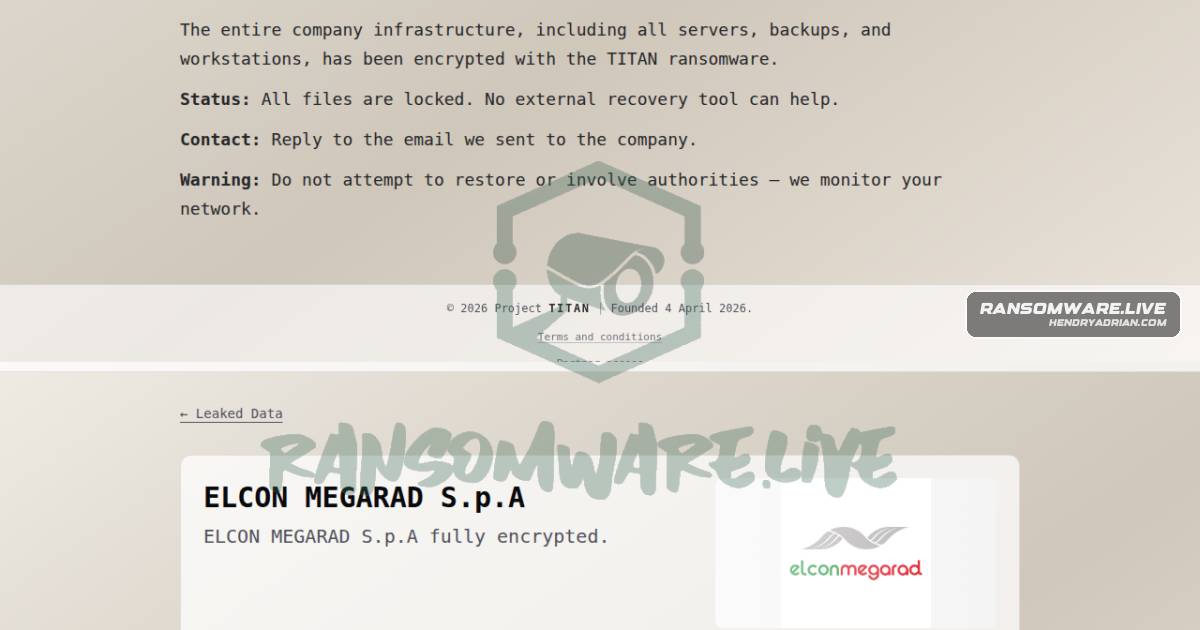
The Titan ransomware group claims it attacked Italy-based ELCON MEGARAD S.p.A. and caused operational disruption. The post cites the group’s blog and says the claim is unconfirmed.
Key points
- The record names ELCON MEGARAD S.p.A., an Italy-based manufacturer, as the victim and Titan as the actor.
- The linked source is hxxps://titanblog[.]org/post/elcon-megarad-s-p-a-fully-encrypted-nv34pi6ihb.
- The post says the group’s claims, including operational disruption, are unconfirmed.
- The claim was listed as discovered and published on August 20, 2026, and is attributed to monitoring by ransomware.live.
Article Details
- Victim
- ELCON MEGARAD S.p.A
- Victim Domain
- Unknown
- Claim Date
- 2026-08-20
- Encryption Status
- Titan's source URL describes the victim as fully encrypted; this is an unverified group claim.
- Encrypted Size
- Unknown
- Exfiltration Status
- Unknown
- Exfiltrated Data
- Unknown
- Exfiltrated Size
- Unknown
- Ransom Demand
- Unknown
- Leak Status
- Unknown; the source reports a public group claim but does not establish that data was published.