
Researchers Find 64,024 Live AWS Credentials Exposed in Public Sources
Summary
Truffle Security researchers say they found 64,024 live AWS access-key pairs and root credentials across public repositories, datasets, container images and CI logs, spanning 9,945 accounts. Many had administrative privileges; AWS and identifiable owners were notified.
Key points
- Researchers identified 64,024 unique live AWS key pairs across 431,875 public findings, covering 9,945 AWS accounts, including 768 corporate environments.
- The findings included 10,625 root keys; 130 reportedly controlled organization management accounts.
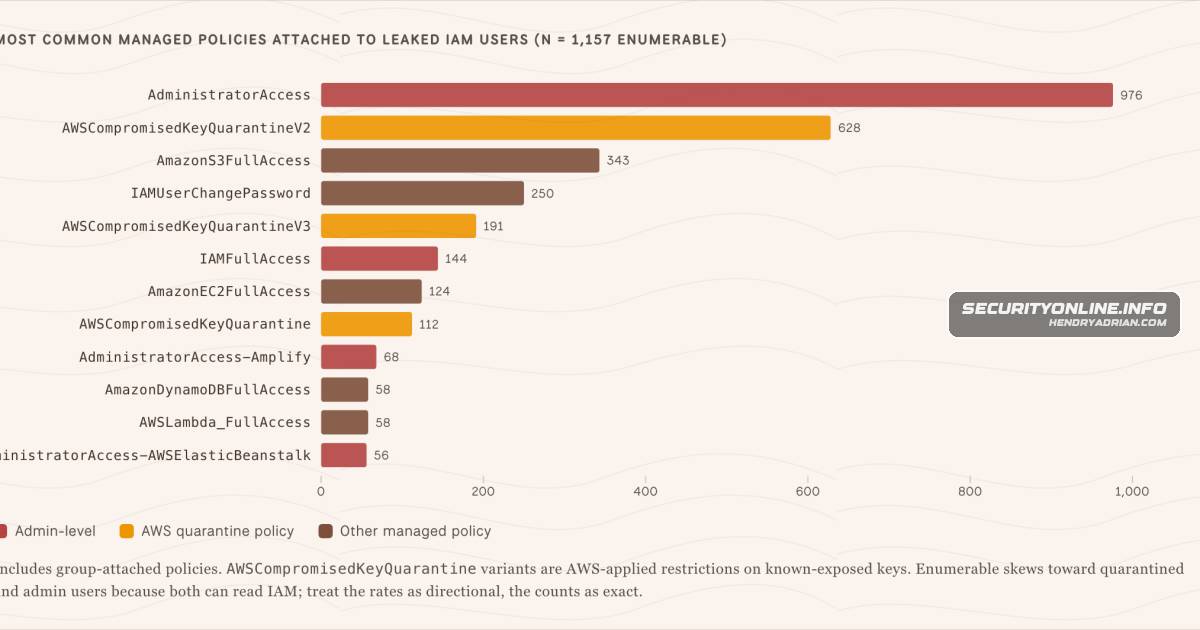
- Of 7,590 active IAM user accounts examined, 84% of those with inspectable policies had full administrative permissions.
- Researchers found 8,482 live keys in 3,394 public Hugging Face datasets, which they described as the largest exposure source.
- The median live leaked key was 1,831 days old, and 86% of examined credentials had not been superseded or revoked.
- Accounts behind readable keys generated $420,631 in cloud spending during July 2026; the article does not establish that this spending was unauthorized.
- Truffle Security said it withheld key material, notified identifiable owners and coordinated with AWS. Recommended steps include revoking root keys, rotating credentials, setting billing alerts and monitoring AWS quarantine tags.
Article Details
- Event Type
- Exposure of live AWS access keys and root credentials in public repositories, datasets, container images, package registries, and CI logs
- Impact
- Researchers reported finding 64,024 live AWS access key pairs and root credentials across more than 9,900 AWS accounts, including 768 corporate environments. Many credentials had administrative privileges, and 130 root keys controlled organization management accounts. Accounts behind readable keys generated $420,631 in cloud spending during July 2026; the article does not establish that this spending was unauthorized.
Vendors
Products
AWSResearchers from Truffle Security found 64,024 live AWS access key pairs and root credentials exposed across public repositories, AI datasets, container images, and CI logs, affecting more than 9,900 AWS accountsHugging FacePublic Git commits, Docker images, package registries, CI logs, and Hugging Face datasets were major exposure sources.