14 Trojanized npm Packages Can Deploy RedShell Linux Backdoor on Import
Summary
Researchers found 14 npm packages that masquerade as utilities but can launch RedShell, the Linux beacon for RedC2 4.0, when imported. The framework includes Red Agent, an LLM-backed command execution component.
Key points
- Researchers identified 14 trojanized npm packages posing as functional calendar and streak utilities.
- Importing a package can launch its bundled Linux payload automatically, without an install hook or an exported function call.
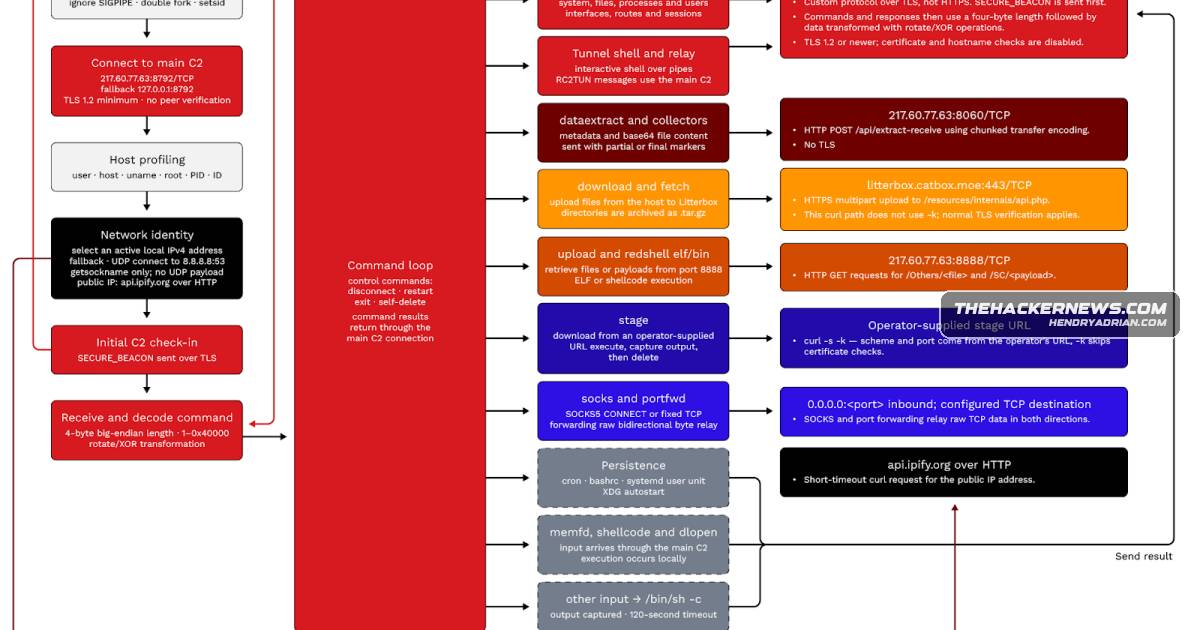
- The payload is RedShell, the Linux beacon for RedC2 4.0, which communicates with a remote server for post-exploitation activity.
- The Linux beacon supports shell commands, system discovery, file operations, data collection, persistence, SOCKS5 proxying, and network pivoting.
- RedC2 4.0 was advertised by a threat actor identified as MarlboroMan; its Red Agent component translates natural-language commands into beacon commands.
Article Details
- Event Type
- Trojanized npm packages distributing a Linux backdoor
- Impact
- The packages masquerade as calendar and streak utilities but launch the RedShell Linux beacon when imported, enabling remote command execution and post-exploitation activity on compromised hosts. The article also describes a separate Rust-crate supply-chain attack that deployed malware for profiling, persistence, and payload delivery.
MITRE ATT&CK
People
Threat Actors
Malware
Vendors
Products
Tools
Red AgentRedC2 4.0 includes AI-driven command execution through its Red Agent component.RedC2 EXTRedC2 extends its control layer with a command-line extension referred to as RedC2 EXT as well as a large language model (LLM)-drivenâ¯componentâ¯called Red Agent, the latter of which lets operators orchestrate