
Authorities and CrowdStrike Disrupt Sality Botnet After Two Decades
Summary
Authorities seized Sality-linked domains in the U.S. and Europe, while CrowdStrike and partners sinkholed the botnet’s peer-to-peer control channels. CrowdStrike says the disruption took the botnet out of its operators’ control.
Key points
- The DOJ, FBI, and DCIS seized Sality-linked domains in the U.S.; law enforcement partners in Bulgaria, Hungary, and Romania seized additional domains.
- CrowdStrike and partners sinkholed Sality’s known super peers, disrupting its peer-to-peer communications and isolating infected machines.
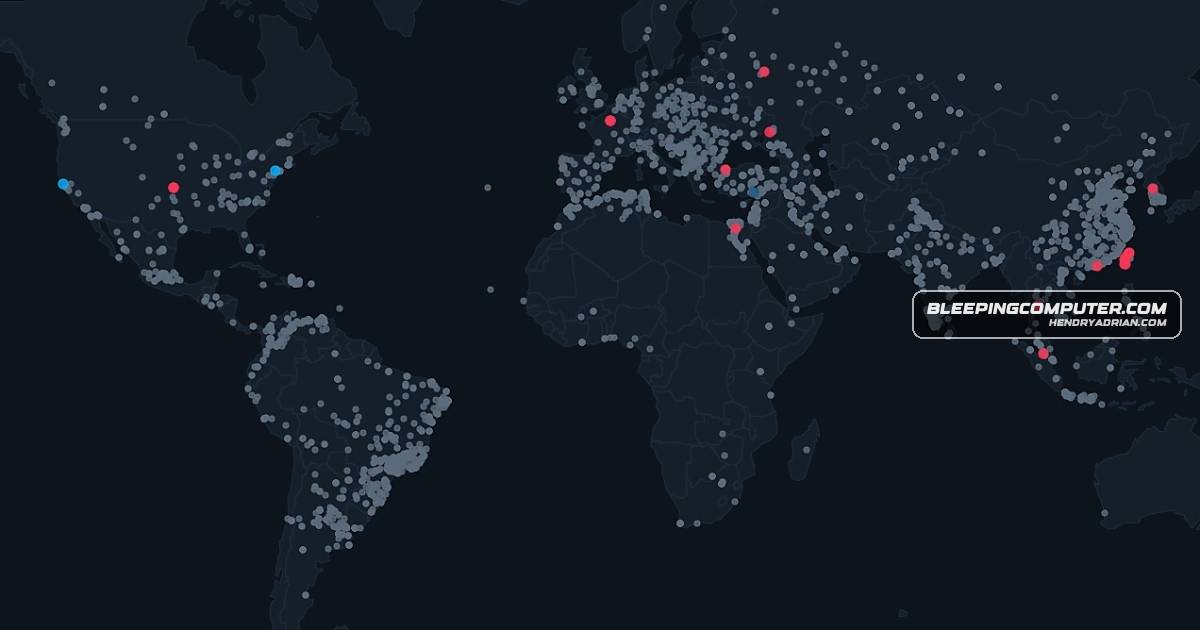
- CrowdStrike says Sality has operated since at least 2003 and infected more than 15,000 devices.
- CrowdStrike attributes Sality to the criminal group it tracks as SALTY SPIDER, which it believes is likely operating from Russia’s Republic of Bashkortostan.
- The two Sality networks active at the time of the operation were mainly used to distribute EggJagger, according to CrowdStrike.
- EggJagger monitors clipboards for cryptocurrency wallet addresses and silently replaces them with addresses controlled by the operator.
Article Details
- Event Type
- Joint international law enforcement and private-sector takedown of the Sality botnet, including seizure of linked domains and sinkholing of its peer-to-peer control infrastructure.
- Impact
- The operation disrupted Sality's control channels and isolated infected machines. CrowdStrike said the botnet was no longer under the operator's control. Sality had infected more than 15,000 devices since at least 2003; its networks were mainly used to distribute EggJagger payloads in clipjacking attacks targeting cryptocurrency wallets.
Threat Actors
Malware
Vendors
Countries
BulgariaDepartment of Justice (DOJ), FBI, and DCIS seized Sality-linked domains in the United States, while law enforcement partners in Bulgaria, Hungary, and Romania seized additional Sality-linked domains hosted in Europe.HungaryDepartment of Justice (DOJ), FBI, and DCIS seized Sality-linked domains in the United States, while law enforcement partners in Bulgaria, Hungary, and Romania seized additional Sality-linked domains hosted in Europe.RomaniaDepartment of Justice (DOJ), FBI, and DCIS seized Sality-linked domains in the United States, while law enforcement partners in Bulgaria, Hungary, and Romania seized additional Sality-linked domains hosted in Europe.RussiaSALTY SPIDER is believed to operate from the Republic of Bashkortostan in Russia.United StatesLaw enforcement seized Sality-linked domains in the United States and Europe.