Dropbox Accounts Accessed Through Lenovo Email Verification Flaw
Summary
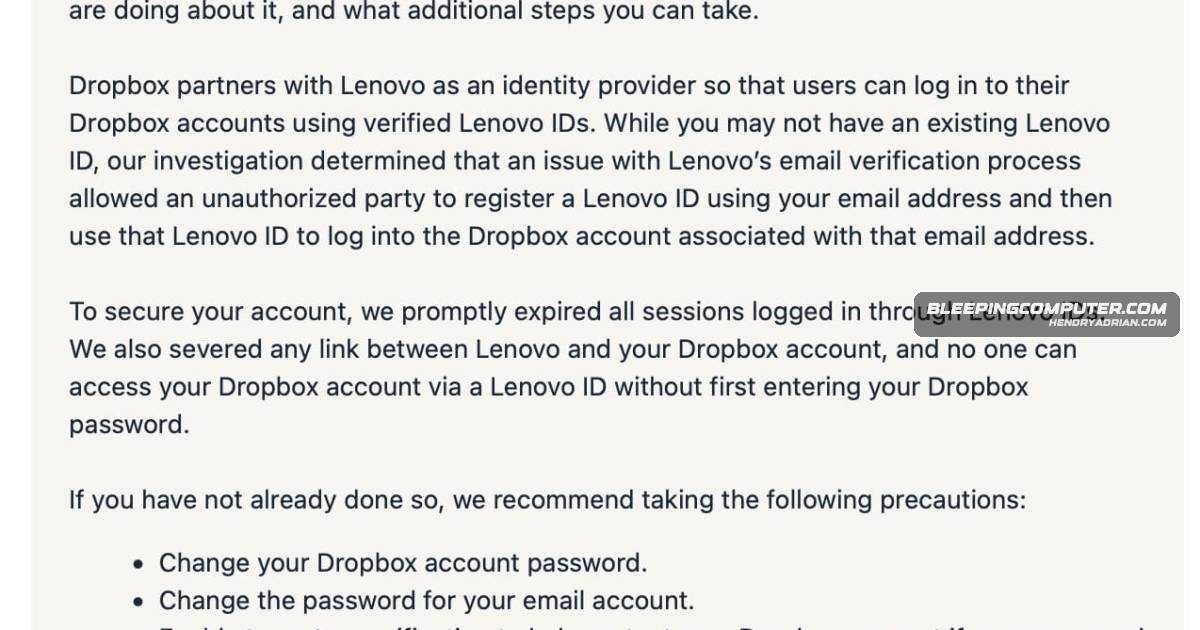
Dropbox said attackers used fraudulent Lenovo IDs, created through an email-verification flaw, to access accounts without passwords from Aug. 4–21. It expired Lenovo-authenticated sessions and now requires Dropbox passwords; Reuters reported about 5,000 accounts were.”
Key points
- Dropbox said an unauthorized party accessed some accounts between August 4 and 21 through Lenovo Identity Provider Services.
- A flaw in Lenovo’s email verification process allowed an attacker to register a Lenovo ID using someone else’s email address.
- The fraudulent Lenovo ID was used to sign in to the associated Dropbox account without its password.
- Reuters reported that about 5,000 accounts were accessed and that content from some users was viewed and downloaded.
- Dropbox and Lenovo described the issue as involving a legacy integration; Lenovo customers were not affected, and the investigation was continuing.
- Dropbox expired sessions authenticated through Lenovo IDs and added a requirement to enter the Dropbox password when using that sign-in option.
Article Details
- Victim Organization
- Dropbox
- Incident Type
- Unauthorized account access through abuse of a flaw in Lenovo’s email verification and Dropbox’s legacy Lenovo ID authentication integration
- Data Types Exposed
- Dropbox account content; specific content types were not disclosed
- Affected Records
- Approximately 5,000 accounts were reportedly accessed, according to Reuters; the article does not report Dropbox confirming this figure.
- Operational Impact
- The attacker accessed affected accounts between August 4 and 21 (year not specified). Dropbox expired sessions authenticated through Lenovo IDs and required users to enter their Dropbox password when signing in with Lenovo ID.
- Claim Status
- confirmed
Vendors
DropboxDropbox warned users that an unauthorized party accessed some accounts by abusing a flaw in Lenovo’s email verification process to create fraudulent Lenovo IDs tied to victims’ email addresses.LenovoDropbox warned users that an unauthorized party accessed some accounts by abusing a flaw in Lenovo’s email verification process to create fraudulent Lenovo IDs tied to victims’ email addresses.
Products
Lenovo IDThe attacker then used Lenovo ID-based authentication to log into Dropbox without needing the account password, prompting Dropbox to expire affected sessions and require passwords for Lenovo ID sign-ins.Lenovo Identity Provider ServicesDropbox said some accounts were accessed through Lenovo Identity Provider Services.