
Spectator Loader Advertised With Persistence and Evasion Claims
Summary
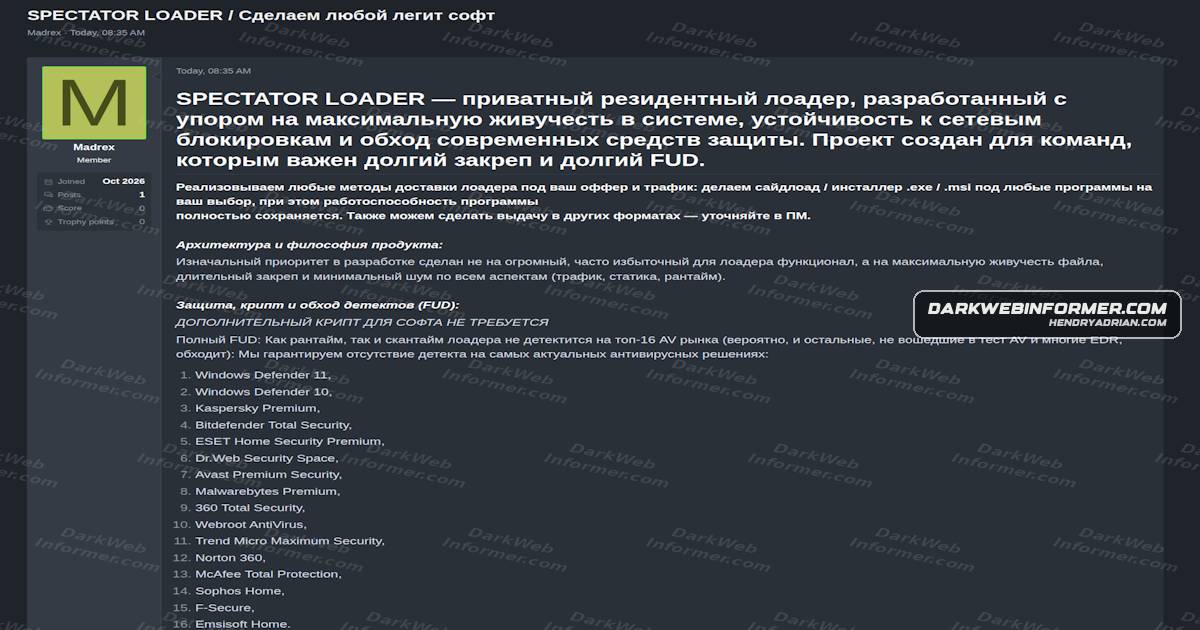
An actor using the handle “Madrex” advertised Spectator Loader as a persistent malware loader with anti-analysis and evasion features. The capabilities are based on the advertisement and remain unverified.
Key points
- The advertisement describes Spectator Loader as a private resident loader focused on long-term persistence and avoiding detection.
- Advertised delivery methods include sideloading, EXE and MSI installers, and custom formats.
- The actor claims the loader uses obfuscation, anti-sandbox checks, and low-level system calls to evade security products.
- Advertised remote-management functions include in-memory payload execution, file transfer, system-information collection, process control, and registry and filesystem operations.
- The report identifies the advertiser as “Madrex” and says screenshots show the service advertisement and a Tox contact identifier.
- The capabilities and delivery methods have not been independently verified; the supplied screenshots document the advertisement only.
Article Details
- Event Type
- An actor advertised Spectator Loader as a private resident malware loader with anti-analysis, evasion, persistence, and remote-management capabilities; the claims are unverified.
- Impact
- If genuine, the advertised capabilities could enable stealthy persistence, payload delivery and in-memory execution, file transfer, process control, registry modification, and filesystem access on compromised hosts. The article reports no confirmed infections or independently verified capabilities.
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe advertisement claims custom obfuscation and build-to-build variation intended to reduce static detection; this capability is unverified.T1105 · Ingress Tool TransferThe article maps file downloading to Ingress Tool Transfer, based on advertised management features; the capability is unverified.T1497 · Virtualization/Sandbox EvasionThe advertisement claims detection of sandboxes, virtual machines, hypervisors, and reverse-engineering environments; this capability is unverified.