
AuditTeam Claims Ransomware Attack on PIT.local in Colombia
Summary
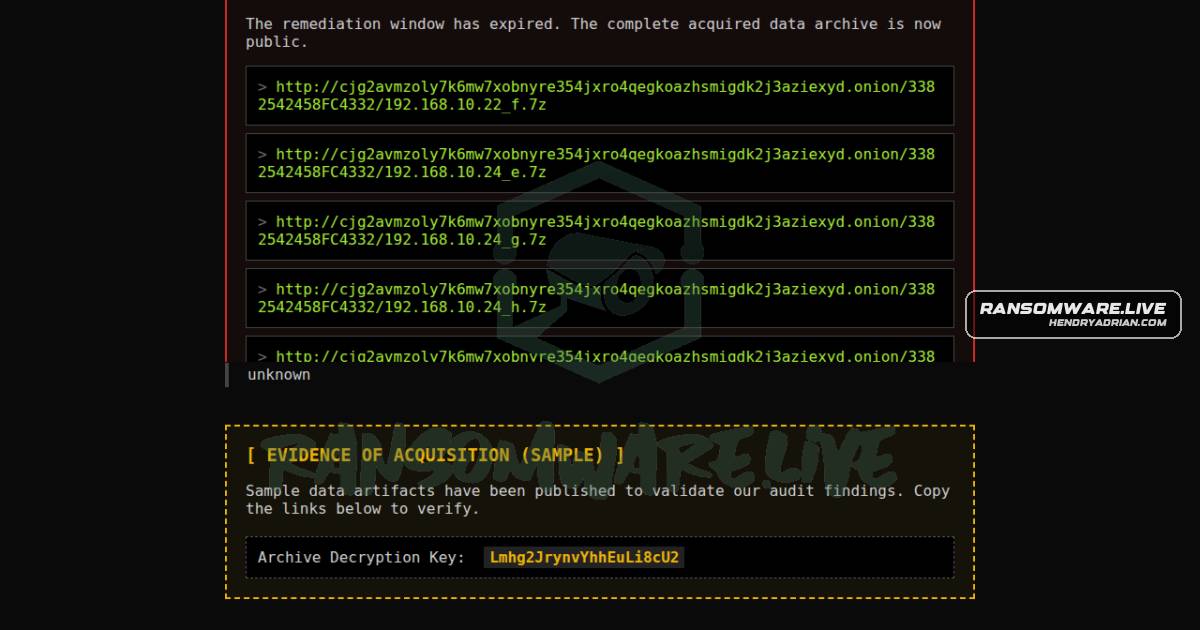
A ransomware.live monitoring post attributes an alleged attack on PIT.local in Colombia to AuditTeam, claiming unauthorized access, encrypted files, and a ransom demand. The information is unverified.
Key points
- The ransomware claim names PIT.local in Colombia as the victim.
- The post attributes the claim to AuditTeam, while noting there is no additional verified information about the actor.
- The claim alleges unauthorized access, file encryption, and a ransom demand.
- The post lists August 27, 2026, as the publication date and September 4, 2026, as the discovery date.
- The post says the claim is based on public statements by the ransomware group and has not been confirmed.
Article Details
- Victim
- PIT.local
- Victim Domain
- PIT.local
- Claim Date
- 2026-08-27
- Encryption Status
- The claim alleges that files were encrypted; this is unverified.
- Exfiltration Status
- Unknown; no exfiltration is reported.
- Ransom Demand
- A ransom demand is alleged, but no amount or other details are provided.
- Leak Status
- A ransomware claim was published; no data leak or publication of victim data is reported.